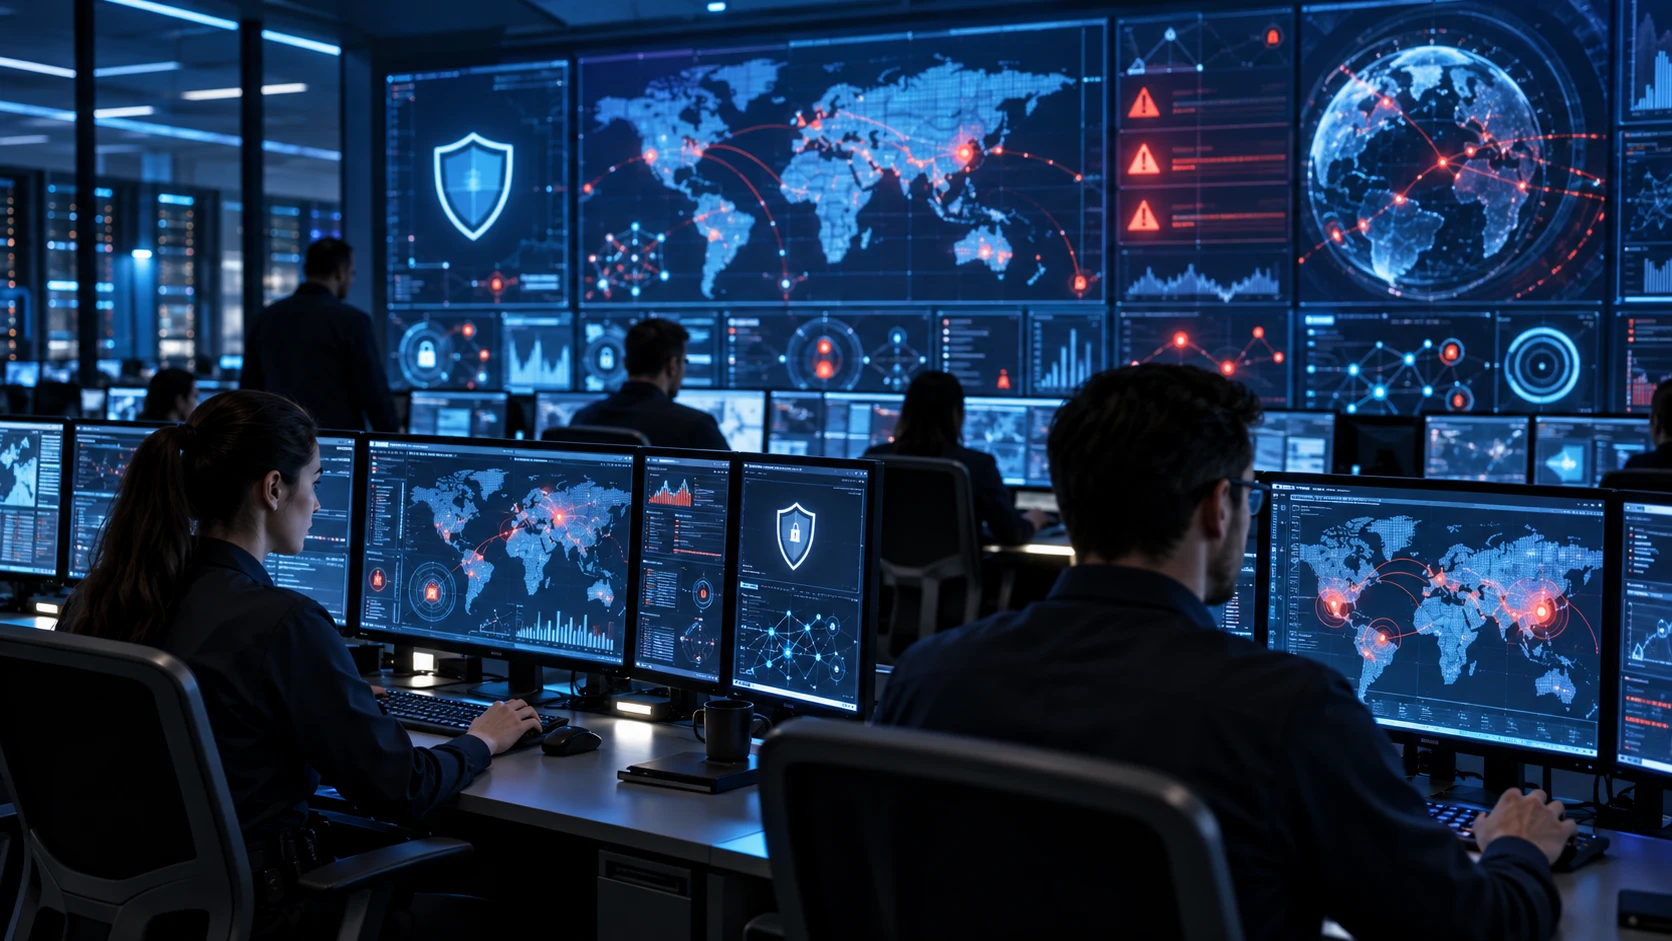
SOC stands for Security Operations Center in cyber security. It is a centralized security function responsible for monitoring systems, detecting suspicious activity, investigating threats, and coordinating responses to cyber incidents. Organizations use SOC teams to gain better visibility into what is happening across networks, endpoints, cloud platforms, applications, and user accounts.
A modern Security Operations Center combines trained security professionals, monitoring technologies, threat intelligence, automation, and documented response procedures. Instead of waiting for a cyber attack to cause visible damage, SOC analysts continuously look for warning signs. Their goal is to identify threats early enough to reduce data loss, downtime, and business disruption.
Understanding what SOC stands for and how it works is useful for students, business owners, IT professionals, and anyone exploring a cyber security career. This guide explains the meaning of SOC, its responsibilities, common tools, analyst roles, monitoring processes, incident response methods, and the benefits organizations can gain from effective security operations.
What Does SOC Stand for in Cyber Security?
SOC stands for Security Operations Center. It refers to a dedicated team or function that continuously monitors an organization’s digital environment for potential security threats. A SOC may operate from a physical office, remotely, or through a managed service provider depending on the organization’s size, resources, and security requirements.
The primary purpose of a SOC is to detect, investigate, and respond to cyber threats. Analysts monitor security alerts from networks, endpoints, cloud systems, applications, and user accounts. When suspicious behavior appears, the team investigates whether the activity is harmless, a false positive, or evidence of a genuine security incident.
A Security Operations Center is more than a room filled with screens and dashboards. Effective security operations depend on trained people, reliable processes, and properly configured technologies working together. These elements help the organization understand threats quickly and take appropriate action before attackers gain additional access or cause greater damage.
Why Is a Security Operations Center Important?
Organizations generate enormous amounts of security data every day. Firewalls, servers, employee devices, cloud applications, and identity systems can produce thousands of alerts and log events. Without a dedicated monitoring process, important warning signs may become buried among normal activity and remain unnoticed until an incident becomes much more serious.
A SOC improves visibility by bringing security information together and assigning trained analysts to review suspicious activity. Early detection matters because attackers may attempt to steal credentials, spread malware, access sensitive files, or move between systems after gaining an initial foothold. Faster investigation can reduce the time they remain undetected.
Security operations also make incident handling more organized. Instead of responding differently every time a problem occurs, teams can follow documented procedures for investigation, escalation, containment, and recovery. This consistency helps reduce confusion during stressful incidents and gives organizations a repeatable process for improving their cyber security defenses over time.
What Does a SOC Team Do?
SOC teams continuously monitor security alerts and activity across the organization’s environment. Analysts may review unusual login attempts, suspicious network connections, malware detections, unexpected file changes, and other warning signs. Their first responsibility is often determining whether an alert requires further investigation or can safely be closed.
When an alert appears suspicious, analysts gather additional evidence. They may review authentication records, endpoint activity, network traffic, application logs, user behavior, and threat intelligence. Combining several sources of information helps the team understand what happened, which systems may be involved, and whether an attacker still has access.
SOC teams also document incidents and improve detection processes. After investigating a threat, analysts may update alert rules, recommend stronger controls, or share lessons with other security teams. This continuous improvement helps organizations identify similar attacks more quickly and reduces repeated weaknesses that attackers could attempt to exploit again.
What Roles Work Inside a SOC?
Entry-level SOC analysts often handle initial alert review and basic investigation. They examine alerts, collect evidence, document findings, and escalate suspicious activity when deeper analysis is required. These positions are common starting points for people building careers in defensive cyber security and security operations.
More experienced analysts may investigate complicated incidents, perform threat hunting, analyze malware behavior, or coordinate containment actions. Security engineers may maintain detection tools, improve integrations, and develop new alert rules. Larger SOC teams can also include incident responders, threat intelligence specialists, digital forensics professionals, and security automation engineers.
SOC managers coordinate the overall security operations program. Their responsibilities may include staffing, reporting, incident escalation, process improvement, tool strategy, and communication with leadership. Although job titles differ between organizations, every role contributes to the same objective: detecting threats and helping the organization respond effectively.
What Tools Are Used in a SOC?
SIEM platforms are among the most common technologies used inside Security Operations Centers. SIEM stands for Security Information and Event Management, and these platforms collect security logs from multiple systems. Analysts use them to search activity, correlate events, create detection rules, and identify patterns that may indicate malicious behavior.
Endpoint Detection and Response tools are also widely used. EDR platforms monitor computers and servers for suspicious processes, malware, unusual file activity, and other endpoint threats. Analysts can investigate affected devices and, when appropriate, isolate compromised systems to prevent malicious activity from spreading through the network.
SOC teams may also use firewalls, intrusion detection systems, vulnerability scanners, threat intelligence platforms, identity security tools, network monitoring systems, and security automation technologies. Combining these tools gives analysts broader context and helps them investigate incidents without relying on one source of information alone.
How Does SOC Monitoring Work?
SOC monitoring begins with collecting data from systems throughout the organization’s environment. Security logs may come from endpoints, servers, applications, cloud platforms, firewalls, identity services, and other infrastructure. Monitoring tools organize this information and generate alerts when suspicious activity or predefined security conditions are detected.
Analysts review these alerts and compare them with normal activity. A failed login may be harmless, but hundreds of login attempts from an unusual location could indicate a password attack. Context is therefore essential because the same event can have very different meanings depending on the user, system, timing, and surrounding activity.
Effective monitoring also requires continuous tuning. Poorly configured tools may generate too many false positives or miss important events entirely. SOC teams regularly review detection rules, add new data sources, adjust alert thresholds, and evaluate threat intelligence so monitoring remains useful as the organization’s systems and attacker techniques change.
How Does a SOC Respond to Cyber Incidents?
Incident response usually begins when an alert is confirmed as a genuine security issue. SOC analysts determine what happened, which accounts or systems are affected, and how the attack may have started. They gather evidence carefully so the organization can understand the scope and make informed decisions about containment.
Containment is designed to stop the threat from spreading. The SOC may disable compromised accounts, isolate infected devices, block malicious addresses, restrict network access, or coordinate with other teams to protect affected systems. The exact response depends on the incident type, available evidence, business impact, and established security procedures.
After containment, teams work toward eradication and recovery. Malicious files may be removed, credentials reset, vulnerabilities patched, and systems restored from clean backups. The SOC then documents what happened and identifies lessons that can improve detection, prevention, and response if a similar cyber attack occurs again.
How SOC Supports Data Protection and Compliance
Security Operations Centers can support data protection by identifying unauthorized access, suspicious data transfers, compromised accounts, and other activity that may expose sensitive information. Fast detection is especially important when personal, financial, healthcare, or confidential business data is involved because delays can increase the amount of information affected.
Organizations subject to privacy requirements also need processes for investigating security incidents and determining whether personal data has been compromised. Understanding topics such as GDPR in cyber security can help teams see how monitoring, incident response, and data protection responsibilities connect within a broader security and privacy program.
A SOC does not make an organization compliant by itself. Compliance can also require policies, access controls, documentation, employee training, risk assessments, and other measures. However, security operations provide important evidence and monitoring capabilities that help organizations identify incidents, investigate them accurately, and support appropriate reporting or remediation decisions.
What Is the Difference Between SOC and NOC?
A SOC focuses primarily on cyber security threats. Its analysts monitor for malicious activity, compromised accounts, malware, unauthorized access, and other security risks. Their goal is to protect systems and information by identifying attacks quickly and coordinating an appropriate response when suspicious behavior is confirmed.
A Network Operations Center, or NOC, focuses more on network performance, availability, and reliability. NOC teams monitor outages, bandwidth, servers, connectivity, and infrastructure health. Their primary responsibility is keeping technology operational rather than investigating attackers or malicious activity across the environment.
The two teams can still work closely together because technical failures and security incidents sometimes look similar at first. A sudden network slowdown could result from equipment failure, but it might also involve malicious activity. Sharing information between SOC and NOC teams can help organizations diagnose problems faster and choose the correct response.
What Are the Benefits of Having a SOC?
One major benefit of a SOC is improved threat visibility. Instead of depending on isolated security tools that may not be reviewed consistently, organizations gain a centralized function responsible for monitoring suspicious activity. This makes it easier to connect events across endpoints, accounts, networks, and cloud systems.
Another benefit is faster incident response. When analysts already monitor security events and follow established procedures, they can begin investigating quickly instead of waiting for someone to notice a visible problem. Reducing detection and response time can limit data exposure, operational disruption, and the number of systems affected.
A SOC also supports continuous security improvement. Analysts learn from false positives, successful detections, incidents, and attacker techniques. These lessons can be used to strengthen security controls, improve monitoring rules, prioritize investments, and help other teams understand where the organization’s most important security weaknesses exist.
What Challenges Do SOC Teams Face?
Alert fatigue is one of the biggest challenges in security operations. Modern security tools can generate huge numbers of notifications, many of which may not represent real threats. Analysts need effective prioritization, automation, and tuned detection rules so important alerts do not disappear among large numbers of low-value events.
Another challenge is maintaining enough skilled security professionals. SOC work requires people who understand networks, operating systems, logs, malware, identity systems, and incident response. Organizations also need schedules that support continuous monitoring without creating unreasonable workloads that reduce analyst effectiveness or increase employee turnover.
The threat landscape changes constantly as attackers develop new techniques and exploit newly discovered weaknesses. SOC teams must therefore continue learning, updating detection logic, reviewing security tools, and improving response procedures. A Security Operations Center cannot remain effective if its processes and monitoring rules stay unchanged while the organization’s technology environment evolves.
Conclusion
SOC stands for Security Operations Center, a centralized cyber security function responsible for monitoring, detecting, investigating, and responding to threats. It combines trained analysts, security technologies, threat intelligence, and structured procedures to give organizations better visibility into suspicious activity across their digital environments.
SOC teams use tools such as SIEM, EDR, firewalls, network monitoring, identity security, and threat intelligence platforms to investigate potential attacks. When a real incident is confirmed, they help contain the threat, support recovery, document what happened, and improve protections against similar attacks in the future.
An effective Security Operations Center can strengthen threat detection, reduce response times, and improve overall security awareness. However, success depends on more than technology alone. Skilled people, clear processes, useful monitoring data, and continuous improvement are all necessary for a SOC to protect an organization effectively.
FAQs
What does SOC stand for in cyber security?
SOC stands for Security Operations Center. It is a centralized cyber security function that monitors systems, investigates suspicious activity, detects threats, and helps organizations respond to security incidents.
What is the main purpose of a SOC?
The main purpose of a SOC is to continuously detect, investigate, and respond to cyber threats. It helps organizations identify malicious activity early and reduce the potential impact of security incidents.
What does a SOC analyst do?
A SOC analyst reviews security alerts, analyzes logs, investigates suspicious events, identifies possible threats, documents findings, and escalates serious incidents. More experienced analysts may also perform threat hunting and incident response.
What tools are commonly used in a SOC?
SOC teams commonly use SIEM platforms, EDR tools, firewalls, threat intelligence systems, vulnerability scanners, network monitoring technologies, identity security solutions, and security automation platforms.
Is a SOC necessary for every organization?
Not every organization needs a large internal SOC. Smaller businesses may use managed security services, while larger organizations may operate dedicated teams. The right approach depends on risk, resources, technology, and monitoring requirements.