Cyber security is a broad field focused on protecting computers, networks, applications, accounts, and sensitive information from digital threats. People working in cyber security may investigate suspicious activity, strengthen security controls, fix vulnerabilities, manage user access, or help organisations respond to attacks. The exact work depends on the role, company, and type of systems being protected.
If you are wondering what do you do in cyber security, the answer is much wider than simply stopping hackers. Cyber security professionals work across technical, analytical, operational, and business areas. Some spend their days monitoring security alerts, while others test systems, secure cloud environments, investigate incidents, or develop policies that reduce digital risk.
What Do You Do in Cyber Security?
Cyber security professionals protect digital systems and information from unauthorised access, disruption, theft, and damage. Their work may involve identifying security weaknesses, monitoring systems for suspicious behaviour, or responding when an incident occurs. The goal is to reduce risk while helping organisations continue using technology safely and reliably.
Daily responsibilities vary depending on the position. A security analyst may spend time reviewing alerts and logs, while a security engineer may configure defensive technologies. Someone working in governance or compliance may focus more on risk assessments, policies, security standards, and making sure business processes meet required security expectations.
The field includes many different cyber security jobs, so professionals do not all perform the same tasks. Security operations, penetration testing, cloud security, identity management, incident response, vulnerability management, and compliance are separate career paths. Understanding these areas helps beginners decide which type of work matches their interests.
Monitor Networks and Security Systems
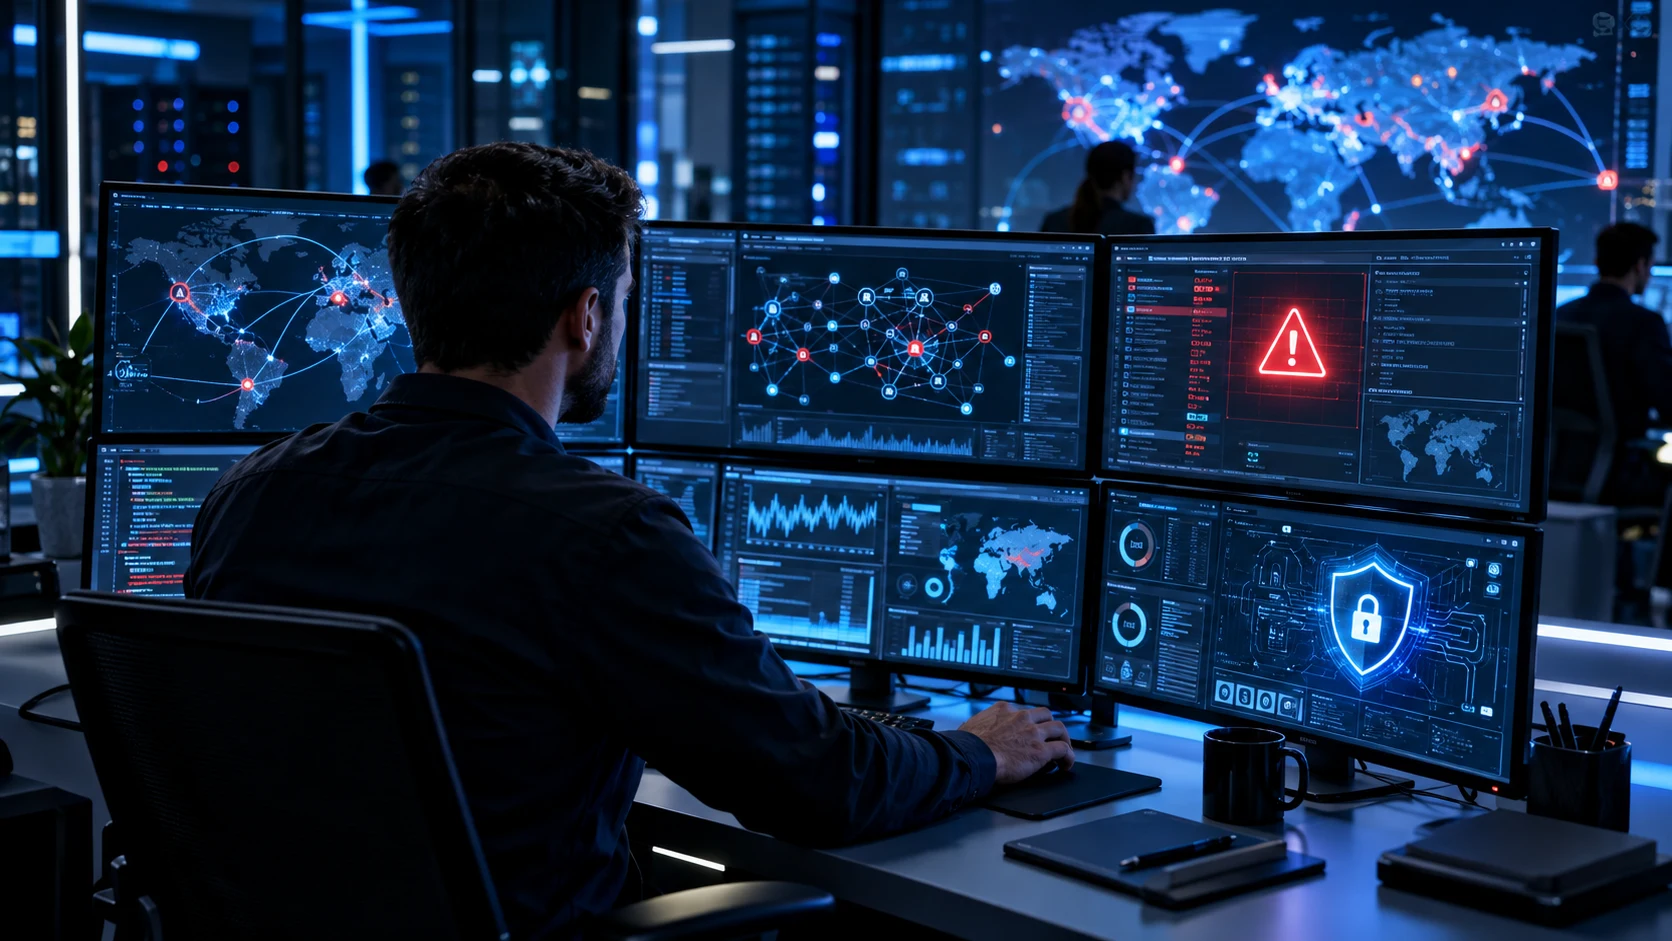
One of the most common cyber security responsibilities is monitoring systems for unusual activity. Security professionals may review information generated by firewalls, servers, cloud platforms, endpoint protection tools, and authentication systems. They look for signs that an account, device, application, or network connection may have been compromised or misused.
Security monitoring often involves examining logs that record what happened inside a system. Analysts may look for repeated failed logins, unusual administrator activity, unexpected software execution, or connections from suspicious locations. These events do not always indicate an attack, so professionals must investigate the surrounding context before deciding whether action is needed.
Monitoring is important because early detection can limit the damage caused by a cyberattack. If suspicious activity is identified quickly, a security team may isolate an affected device or block a compromised account. Continuous monitoring therefore gives organisations greater visibility into their technology and helps them respond before a small security problem becomes more serious.
Investigate Cyber Security Alerts
Security tools generate alerts when they detect activity that matches suspicious patterns or security rules. Cyber security analysts review these alerts to determine whether they represent genuine threats or harmless activity. This process requires careful analysis because security systems can produce many notifications, and not every alert deserves the same level of attention.
During an investigation, an analyst may check account activity, network connections, system logs, files, processes, and recent changes. The goal is to understand what happened, which systems may be affected, and whether an attacker gained access. Analysts often follow a structured process so important evidence is not missed during the investigation.
If the alert is confirmed as a real threat, the security team may take immediate action. This can include disabling accounts, blocking connections, isolating endpoints, or removing malicious files. The analyst may also document the incident so the organisation understands what happened and can improve its defenses against similar attacks in the future.
Protect User Accounts and Access
Identity security is another major part of cyber security because user accounts are common targets for attackers. Professionals help organisations control who can access systems, applications, and sensitive information. They may manage authentication methods, user permissions, administrator accounts, and access policies to reduce the risk of unauthorised activity.
The principle of least privilege is frequently used when managing access. It means users should receive only the permissions necessary to perform their work rather than automatically getting broad access. Limiting permissions reduces the amount of damage that can occur if a user account is accidentally misused or compromised by an attacker.
Cyber security teams may also implement multi-factor authentication, single sign-on, role-based access controls, and privileged access management. They regularly review accounts and remove unnecessary permissions when employees change roles or leave the organisation. Strong identity management makes it harder for stolen passwords to provide attackers with unrestricted access to important systems.
Find and Manage Security Vulnerabilities
Cyber security professionals regularly identify weaknesses in software, devices, and configurations before attackers can take advantage of them. Vulnerability scanners may be used to detect outdated software, missing patches, exposed services, or known security flaws. Teams then review the findings and decide which issues create the greatest risk.
Not every vulnerability requires the same response. Security professionals consider factors such as technical severity, system importance, internet exposure, available fixes, and whether attackers are actively exploiting the weakness. This risk-based approach helps organisations focus first on vulnerabilities that could have the most serious impact.
Once a vulnerability is prioritised, teams work with IT administrators, developers, or system owners to fix it. The solution may involve installing a software update, changing a configuration, disabling an unnecessary service, or applying another security control. The system can then be tested or scanned again to confirm that the weakness has been properly addressed.
Respond to Cyber Security Incidents
Incident response involves managing security events that may threaten an organisation’s systems or information. Examples include malware infections, compromised accounts, phishing attacks, ransomware, data exposure, and suspicious network activity. Security professionals need to act quickly while still collecting enough information to understand what happened and how serious the incident is.
The response may begin by containing the threat so it cannot spread further. A security team might disconnect an infected computer, reset stolen credentials, block malicious traffic, or temporarily restrict access to a system. Once the situation is controlled, investigators can study the incident and determine its cause and impact.
Recovery is another important stage because affected systems need to return to normal operation safely. Teams may restore data from backups, reinstall software, apply security updates, or strengthen access controls. Afterward, they usually review the incident and identify lessons that can improve procedures, monitoring, training, or technical defenses in the future.
Protect Networks, Devices, and Cloud Systems
Cyber security professionals help secure the infrastructure that organisations rely on every day. Network security may involve configuring firewalls, reviewing traffic, segmenting systems, and controlling remote connections. The goal is to prevent attackers from entering the network easily or moving freely between systems after gaining initial access.
Endpoint security focuses on devices such as laptops, desktops, servers, and mobile devices. Security teams may deploy anti-malware tools, endpoint detection systems, encryption, and device-management controls. Keeping these devices updated and properly configured reduces the number of weaknesses attackers can use to compromise employees or business systems.
Cloud security has also become increasingly important as organisations use online services for storage, applications, collaboration, and computing. Professionals review cloud permissions, security configurations, logging, encryption, and exposed resources. They help ensure that sensitive data and services remain protected even when employees access them from different locations and devices.
Test Security Controls and Systems
Some cyber security professionals test systems to determine whether existing protections are working as intended. This can include vulnerability assessments, penetration testing, configuration reviews, and security control testing. The purpose is to identify weaknesses before criminals discover them and to give organisations time to correct problems.
Penetration testers use authorised methods to simulate how an attacker might approach a system. They may examine web applications, networks, cloud services, or other approved targets for exploitable weaknesses. Testing must always be performed with clear permission and within agreed boundaries because accessing systems without authorisation can create serious legal and security problems.
After testing, security professionals document what they discovered and recommend improvements. A useful report explains the weakness, potential impact, affected systems, and suggested remediation steps. Clear reporting matters because technical findings only improve security when system owners understand what needs to be fixed and why the issue deserves attention.
Train Employees About Cyber Threats
Cyber security is not only about technology because attackers frequently target people through social engineering. Security teams help employees recognise phishing emails, suspicious links, fake login pages, unusual requests, and other common scams. Awareness training reduces the chance that employees unknowingly provide attackers with passwords, information, or access.
Professionals may create training sessions, simulated phishing exercises, security guides, and reporting procedures. The purpose should be to help employees make better decisions rather than simply frighten them with technical threats. Clear examples can show workers how to recognise warning signs and what steps to take when something appears suspicious.
Employees also need to know how to report possible incidents quickly. Someone who clicks a malicious link or receives a suspicious authentication request should understand who to contact. Fast reporting gives security teams more time to investigate and contain potential threats, making employee awareness an important part of the organisation’s overall defense strategy.
Document Security Policies and Risks
Many cyber security roles involve documentation because organisations need clear rules for protecting systems and information. Security professionals may write policies covering passwords, acceptable technology use, remote access, data handling, backups, incident response, and employee access. These policies help create consistent expectations across different teams and departments.
Risk assessments are another common responsibility. Security professionals identify valuable systems, potential threats, weaknesses, and possible business impacts. They then help organisations decide which security improvements should receive priority based on the level of risk rather than treating every technology problem as equally important.
Documentation also supports audits, compliance activities, incident investigations, and future security planning. Accurate records make it easier to show what controls exist and how decisions were made. Professionals therefore need good writing skills alongside technical knowledge, especially when explaining complex security risks to managers and other non-technical stakeholders.
What Skills Do You Need to Work in Cyber Security?
Technical fundamentals are important for many cyber security careers. Networking, Windows, Linux, authentication, vulnerabilities, malware, encryption, firewalls, and incident response provide a strong starting point. Different roles then require more specialised skills such as cloud security, scripting, penetration testing, threat analysis, or identity management.
Problem solving is equally important because cyber security professionals rarely receive perfect information. They may need to study several logs, alerts, and system events before understanding what happened. Attention to detail helps them notice small clues that could reveal malicious activity, while logical thinking helps separate genuine threats from normal system behaviour.
Communication also matters because security professionals regularly work with managers, employees, developers, IT teams, and customers. They need to explain technical risks in simple language and document their findings clearly. Someone with strong technical skills but poor communication may struggle to convince others to take the actions necessary to improve security.
Conclusion
Understanding what do you do in cyber security means recognising that the field includes many different responsibilities. Professionals may monitor threats, investigate alerts, manage vulnerabilities, protect user accounts, secure networks, respond to incidents, or test systems. The exact work depends heavily on the cyber security role and the organisation’s technology environment.
Cyber security combines technology with investigation, communication, and risk management. Professionals need to understand how systems normally work before they can recognise suspicious behaviour or security weaknesses. Strong fundamentals in networking, operating systems, authentication, and common cyber threats can therefore provide a useful foundation for many different career paths.
People interested in cyber security do not need to master every part of the field before starting. Explore different roles, build practical skills, and identify the type of security work that interests you most. With consistent learning and hands-on practice, you can develop the knowledge needed to move toward a suitable cyber security career.
FAQs
What do cyber security professionals do every day?
Daily tasks may include reviewing security alerts, analysing logs, managing vulnerabilities, protecting accounts, responding to incidents, configuring security controls, and documenting risks. Responsibilities vary significantly depending on the specific role.
Is cyber security mostly about hacking?
No. Ethical hacking is only one area of cyber security. Many professionals work in monitoring, incident response, identity management, cloud security, engineering, vulnerability management, compliance, risk, and employee security awareness.
Do you need coding skills for cyber security?
Not every role requires advanced coding. Programming and scripting can be useful for technical positions, but many jobs focus more on security monitoring, risk management, identity, compliance, investigation, or system administration.
Is cyber security difficult to learn?
Cyber security involves many topics, but beginners can learn gradually by starting with networking, Windows, Linux, and basic security concepts. Practical labs can then help turn theoretical knowledge into useful skills.
What is a good first job in cyber security?
Common entry-level roles include SOC Analyst, Junior Security Analyst, IAM Analyst, Cyber Security Technician, and Security Operations Analyst. The best starting position depends on your skills, interests, and previous technical experience.