Baiting is a social engineering technique that cybercriminals use to trick people into taking unsafe actions by offering something attractive or useful. The attacker creates a tempting situation, such as a free download, reward, gift, movie, software tool, or physical device. When the victim takes the bait, they may unknowingly install malware, reveal sensitive information, or give attackers access to a system.
Understanding what is baiting in cyber security is important because these attacks rely more on human curiosity and behavior than technical weaknesses. Even strong security software may not stop every attack if a user voluntarily opens a malicious file or enters information into a fake website. Recognizing how baiting works can help individuals and organizations avoid these social engineering traps.
What Is Baiting in Cyber Security?
Baiting in cyber security is a type of social engineering attack in which an attacker offers something appealing to persuade a person to perform a risky action. The reward may appear valuable, convenient, entertaining, or exclusive. The attacker depends on curiosity, greed, urgency, or excitement to make the victim act before carefully checking whether the offer is legitimate.
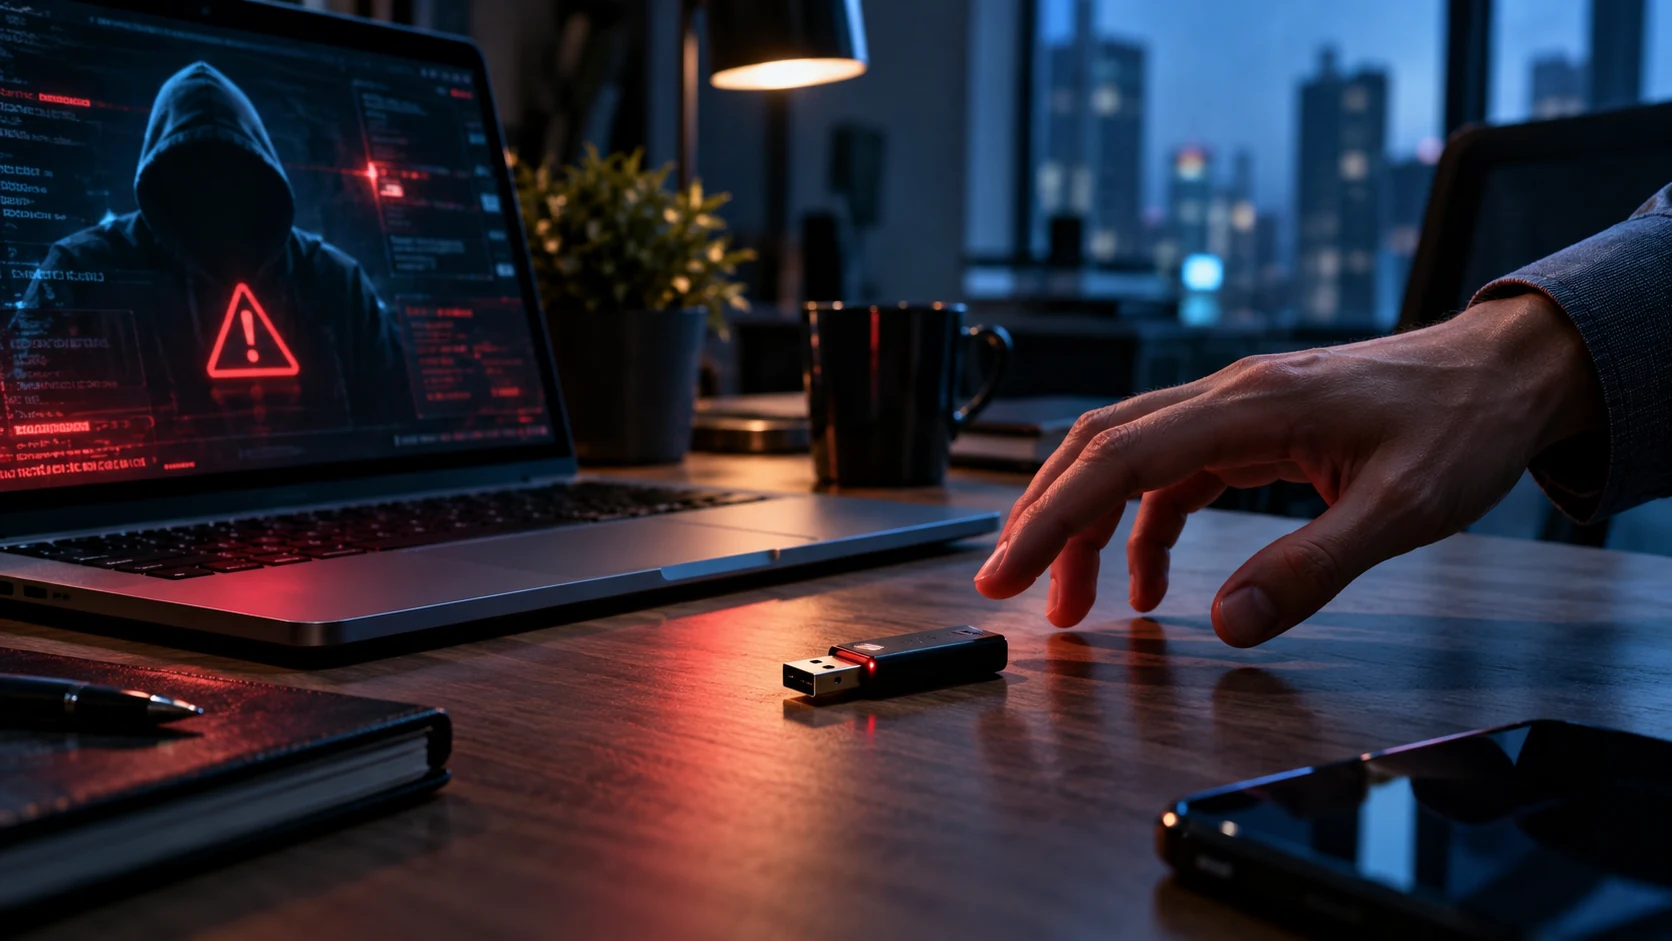
A baiting attack can happen online or through a physical object. Online bait may include free software, downloadable entertainment, gift cards, or fake promotional offers. Physical baiting may involve leaving infected USB drives or other devices in locations where employees or members of the public are likely to find and use them.
The goal of baiting is usually to compromise a device, steal credentials, collect confidential information, or gain unauthorized access to a network. Unlike direct technical hacking, baiting convinces the victim to participate in the attack. This human element makes social engineering awareness an important part of modern cyber security.
How Does a Baiting Attack Work?
A baiting attack usually begins when the attacker creates something attractive enough to capture the target’s attention. The offer may promise free access to premium software, exclusive media, discounts, rewards, or valuable information. Attackers often design the bait to match the interests or needs of the people they hope to target.
Once the victim interacts with the bait, the attacker attempts to trigger the harmful action. A downloaded file may contain malware, a fake website may request login credentials, or an infected USB drive may introduce malicious software. The victim may believe they are receiving the promised reward while the attacker secretly gains access or collects information.
After successful compromise, attackers may steal files, capture passwords, monitor activity, spread malware, or move deeper into a business network. Some baiting attacks create immediate damage, while others remain hidden for longer periods. The exact result depends on the malware, stolen information, and level of access the attacker obtains.
What Are Common Examples of Baiting Attacks?
A common online example is a website offering free downloads of expensive software, games, movies, or digital tools. The victim downloads what appears to be the promised content, but the file contains malicious code. Once opened, the malware may collect credentials, monitor activity, encrypt files, or give the attacker remote control of the device.
Fake giveaways and rewards can also be used as bait. A message may claim that someone has won a gift card, smartphone, cash prize, or special promotion and must provide personal information to receive it. Victims may then enter contact details, passwords, payment information, or other sensitive data into a fraudulent form controlled by the attacker.
Physical baiting often involves removable storage devices such as USB drives. An attacker may leave an infected drive in a parking lot, office lobby, conference area, or workplace. If someone finds the device and connects it to a computer out of curiosity, malicious software may execute or attempt to trick the user into opening a dangerous file.
Why Do Baiting Attacks Work?
Baiting attacks work because they take advantage of normal human emotions and habits. People are naturally curious about unexpected opportunities, free items, unknown devices, or exclusive content. Attackers design their bait to make the reward appear more interesting than the possible risk, encouraging victims to act without carefully considering the consequences.
The promise of receiving something valuable can also lower a person’s suspicion. A free software license, gift voucher, or premium download may seem harmless when presented professionally. Cybercriminals may copy trusted branding, create convincing websites, or use familiar language to make the offer appear legitimate and reduce warning signs.
Another reason baiting works is that many people underestimate the risks associated with downloads and removable devices. They may assume that antivirus software will automatically block anything dangerous. However, attackers constantly adapt their techniques, and no security control can completely replace cautious user behavior and awareness.
What Is the Difference Between Baiting and Phishing?
Baiting and phishing are both social engineering techniques, but they use different methods to influence victims. Baiting typically offers something attractive in exchange for an action, while phishing usually impersonates a trusted person or organization to obtain information. Both attacks depend heavily on deception rather than directly breaking through security systems.
A phishing message may claim that a bank account needs verification or that a password must be reset immediately. Baiting, by comparison, may offer free software, a reward, or valuable content that encourages the person to click or download something. Phishing often relies on fear or urgency, while baiting commonly relies on curiosity or desire.
The two techniques can also overlap during real-world attacks. A cybercriminal might send a phishing email that contains a fake reward as bait, making the attack both attractive and deceptive. Security awareness training should therefore focus on recognizing suspicious behavior rather than assuming every social engineering attack fits into only one category.
What Is the Difference Between Baiting and Pretexting?
Pretexting is a social engineering technique in which the attacker creates a believable story or false identity to obtain information or access. For example, the attacker may pretend to be an IT technician, bank employee, manager, or customer support representative. The false situation is designed to make the target trust the attacker and cooperate.
Baiting focuses more strongly on offering something desirable to influence the victim’s behavior. Instead of building a detailed story, the attacker may simply provide a tempting download, reward, or physical item. The target becomes interested in obtaining the promised benefit and may overlook warning signs or normal security procedures.
Both techniques manipulate human decision-making and can be combined. An attacker could pretend to be an employee from a trusted company while offering a free digital resource. Understanding these differences helps users recognize that social engineering attacks can take many forms and may use several psychological techniques at the same time.
What Information Can Be Stolen Through Baiting?
Baiting attacks can expose many types of personal and business information depending on how the attack is designed. Malware installed through a fake download may collect usernames, passwords, browser data, documents, or stored account information. Fake reward forms may directly ask users to provide personal details that attackers can later misuse.
Sensitive personal information can be especially valuable to criminals because it can support identity theft, account takeover, and targeted fraud. Organizations should understand how PII in cyber security is identified and protected because baiting attacks may specifically target names, addresses, account details, financial records, or other personally identifiable data.
Business information can also become exposed after a successful attack. An infected employee device may provide access to internal files, customer records, email accounts, or company systems. Attackers may use stolen information to launch additional phishing campaigns, commit fraud, or move through connected systems to search for more valuable targets.
What Are the Risks of USB Baiting?
USB baiting is particularly dangerous because removable devices can appear harmless and familiar. An attacker may deliberately label a drive with names such as “Payroll,” “Confidential,” or “Employee Records” to increase curiosity. Someone who finds the device may connect it to a computer simply to discover what information is stored on it.
The USB drive may contain malicious files designed to trick the user into opening them. In some cases, specially prepared hardware may behave differently from an ordinary storage device and attempt to interact with the computer automatically. The exact threat depends on the device and system configuration, but unknown removable media should always be treated cautiously.
Organizations can reduce USB baiting risks through technical controls and employee education. Policies may restrict unknown removable devices, disable unnecessary USB access, or require security teams to inspect found equipment. Employees should be instructed to hand suspicious devices to IT or security personnel rather than connecting them to workplace computers.
How Can You Recognize a Baiting Attack?
One warning sign is an offer that appears unusually valuable or too good to be true. Free premium software, expensive gifts, exclusive downloads, or unexpected prizes should be treated carefully. Attackers often create offers that encourage quick action so the victim focuses on the reward rather than checking whether the source is trustworthy.
Unexpected downloads and attachments can also indicate baiting. Users should question why a file is being offered, where it came from, and whether the website or sender can be verified. File names and attractive descriptions are not evidence of safety because malicious content can be disguised as documents, software installers, images, or other familiar formats.
Physical devices found in public or workplace locations should also raise suspicion. A USB drive, memory card, or unknown electronic device should not be connected simply because it appears interesting. Reporting the item to appropriate security personnel is safer than trying to investigate its contents on a personal or company computer.
How Can Individuals Prevent Baiting Attacks?
Individuals should avoid downloading software, entertainment, or files from unfamiliar websites and unexpected messages. Legitimate applications should come from trusted developers, official stores, or verified company websites. Free versions of expensive products from unknown sources can carry significant security risks, particularly when the offer requires disabling security protections during installation.
Users should also be cautious about online giveaways and reward forms requesting unnecessary information. A legitimate promotion should not normally require sensitive passwords or account credentials. Before entering personal data, check the website address, company identity, privacy information, and reason the information is being requested.
Keeping operating systems, browsers, and security software updated provides another layer of protection. Updates can fix vulnerabilities that malware may attempt to exploit after a malicious download is opened. However, technical protection works best when combined with careful decisions because preventing interaction with suspicious bait is usually safer than trying to stop an attack afterward.
How Can Businesses Prevent Baiting Attacks?
Businesses should provide regular security awareness training that explains baiting through realistic examples. Employees need to understand the risks of unknown USB drives, suspicious downloads, free software, and unexpected promotional offers. Training should focus on practical decisions employees can make when they encounter something unusual rather than only teaching technical definitions.
Technical controls can reduce the damage if someone makes a mistake. Endpoint protection, application controls, restricted user permissions, email security, network monitoring, and removable media policies can create several defensive layers. Organizations may also block unauthorized software installations or restrict access to websites known for distributing unsafe downloads.
Clear reporting procedures are equally important. Employees should know exactly what to do when they find an unknown device, receive a suspicious offer, or accidentally interact with questionable content. Fast reporting allows security teams to investigate the event, isolate affected devices, and limit the damage before an attacker can gain wider access.
What Should You Do If You Fall for a Baiting Attack?
If you suspect that you downloaded malicious content or connected a suspicious device, stop interacting with it immediately. In a workplace, report the event to the IT or security team as soon as possible. Quick reporting can help professionals investigate the device and prevent a possible compromise from spreading to other systems.
If account credentials were entered into a suspicious website, change the password through the legitimate service. Use a different trusted device if the original computer may be infected, and enable multi-factor authentication where available. You should also review recent account activity for unfamiliar logins, password changes, or other signs of unauthorized access.
Avoid trying to hide the mistake because delayed reporting can increase the damage. Security teams are better able to respond when they know what happened, what was downloaded, and which accounts may be affected. Organizations should encourage a reporting culture where employees feel comfortable sharing mistakes quickly instead of waiting until obvious damage appears.
Best Practices for Defending Against Baiting
The strongest defense against baiting combines user awareness with technical security controls. Employees and individuals should learn to question unexpected rewards, suspicious downloads, unknown devices, and requests for personal information. Developing a habit of verifying before clicking, downloading, or connecting hardware can prevent many social engineering attacks at the earliest stage.
Organizations should also apply least-privilege access so compromised user accounts or devices cannot automatically reach every system. Endpoint monitoring, malware protection, secure authentication, software restrictions, and network segmentation can help contain attacks. These controls reduce the potential impact if a user accidentally interacts with malicious bait.
Security teams should regularly review social engineering risks and update training as attack methods change. Testing response procedures, reviewing incidents, and discussing new tactics can make employees better prepared. Baiting succeeds when temptation overrides caution, so effective security should make careful verification a normal part of everyday digital behavior.
Conclusion
Understanding what is baiting in cyber security helps people recognize attacks that use tempting offers instead of obvious threats. Cybercriminals may use free downloads, rewards, giveaways, or infected physical devices to convince victims to take unsafe actions. Once the bait is accepted, attackers may steal information, install malware, or gain unauthorized access.
Baiting is dangerous because it targets human curiosity and decision-making. Technical tools can provide important protection, but they cannot prevent every user from downloading suspicious files or connecting unknown hardware. Security awareness, careful verification, and strong organizational policies therefore play a major role in reducing baiting risks.
Individuals and businesses should treat unexpected rewards, unknown devices, and unusually attractive offers with caution. Using trusted sources, limiting permissions, maintaining updated security tools, and reporting suspicious activity quickly can significantly reduce exposure. Recognizing the bait before interacting with it is often the most effective defense against this type of social engineering.
FAQs
What is baiting in cyber security in simple words?
Baiting is a social engineering attack that offers something attractive, such as free software or a reward, to trick someone into downloading malware, revealing information, or performing another unsafe action.
What is an example of a baiting attack?
A common example is an infected USB drive intentionally left where someone will find it. If the person connects the device out of curiosity, malicious software may attempt to compromise the computer.
Is baiting the same as phishing?
No. Baiting usually attracts victims with a reward or desirable item, while phishing often impersonates a trusted source to steal information. However, attackers can combine both techniques in one campaign.
Why do hackers use baiting attacks?
Hackers use baiting because curiosity, rewards, and free offers can influence people to ignore normal security precautions. Successful attacks may provide access to credentials, personal information, devices, or business networks.
How can baiting attacks be prevented?
Avoid suspicious downloads, unknown USB devices, and unexpected rewards. Use trusted software sources, keep security tools updated, verify unusual offers, follow workplace policies, and report suspicious activity to security teams quickly.