Data in Motion: Meaning, Risks & How to Protect It
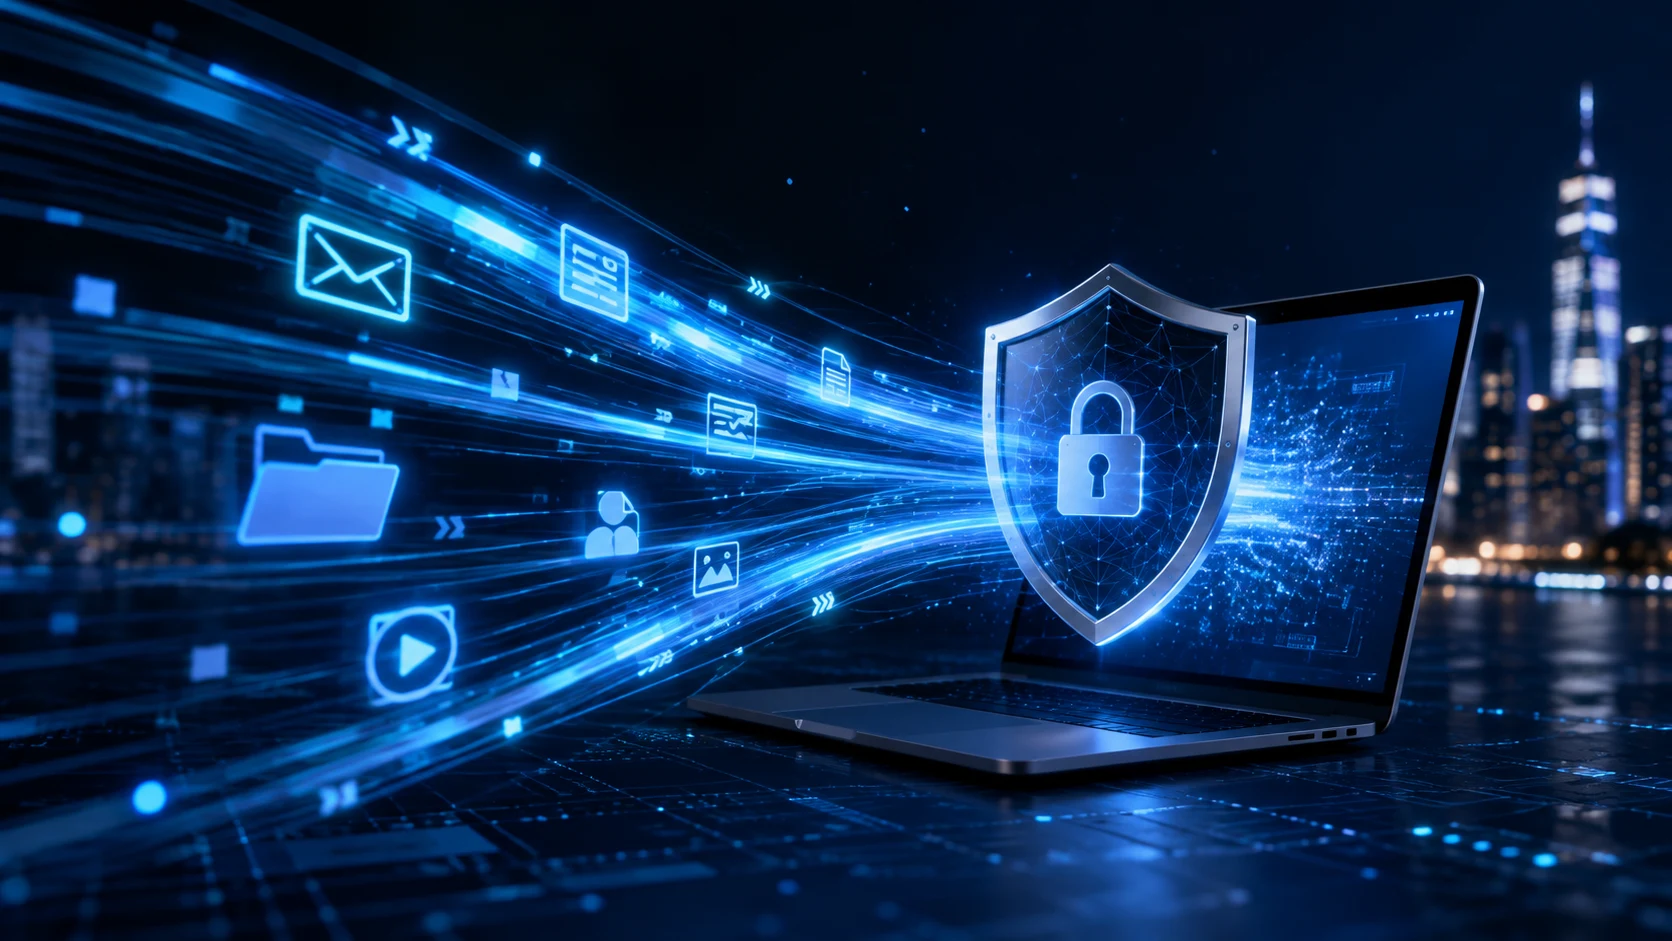
Modern organizations rarely keep information in one place. Customer details move from websites to databases, employees share documents through cloud applications, mobile devices connect to business systems, and APIs exchange information between software platforms every second. Whenever information travels through a network, application, device, cloud service, or communication channel, it becomes data in motion. This active movement makes digital services faster and more connected, but it also creates opportunities for interception, manipulation, leakage, and unauthorized access. Understanding how data in transit works is therefore an important part of modern cybersecurity and data protection. Businesses that know where their information moves can apply encryption, authentication, monitoring, and secure communication protocols to reduce risk without interrupting legitimate workflows.
What Is Data in Motion?
Data in motion refers to digital information that is actively moving from one location, device, system, application, or network to another. It is also commonly called data in transit because the information is traveling rather than remaining stored in a fixed location. An email moving from a sender’s device to a mail server is a simple example of data in motion. Other examples include information transmitted between cloud applications, website requests sent to servers, files uploaded to online storage, and payment details moving through a payment gateway. The movement may occur over the public internet, a private corporate network, wireless connections, or dedicated infrastructure. Protecting this information requires organizations to secure both the communication channel and the systems participating in the exchange.
Understanding data in motion becomes easier when compared with other states of digital information. Data at rest refers to information stored on devices, databases, hard drives, servers, backups, or cloud storage systems. Data in use describes information currently being processed by software or accessed by a user or computing system. Data in motion sits between these states because information regularly moves from storage into applications and then travels to other locations. A customer record might begin as data at rest inside a database before becoming data in use when an application processes it. When that application sends the information to another service, it becomes data in transit. These states can change rapidly during ordinary business operations.
The concept applies to far more than traditional file transfers between computers. Modern applications continuously exchange small pieces of information through APIs, microservices, mobile apps, cloud platforms, and Internet of Things devices. A smartphone checking an account balance, for example, sends a request across a network and receives account information in response. Collaboration platforms also transmit messages, files, video streams, authentication details, and notifications between users and cloud infrastructure. Even automated software systems may exchange large volumes of data without direct human involvement. Because these transfers happen constantly, organizations may underestimate how much information is moving across their environment. Mapping these digital pathways is an important first step toward protecting sensitive data.
The importance of data in motion has increased as businesses have adopted cloud computing, remote work, software-as-a-service platforms, and distributed digital infrastructure. Employees may access business applications from homes, hotels, offices, airports, and mobile devices rather than from one controlled corporate network. Organizations also depend on external vendors that receive or process information through APIs and shared platforms. These connections expand the number of locations through which sensitive information can travel. Cybersecurity therefore cannot focus only on protecting databases or local servers. Security controls must follow information while it moves across internal networks, cloud environments, third-party systems, and internet connections. This approach helps reduce exposure across increasingly complex digital ecosystems.
Not all data in transit requires exactly the same level of security. Public information such as a general website page may create relatively little confidentiality risk if intercepted, while financial information or authentication credentials can require much stronger safeguards. Healthcare information, intellectual property, customer records, employee details, and confidential business communications may also deserve stricter protection. Organizations should therefore identify what information is moving and determine its sensitivity before choosing security controls. Data classification policies can help teams distinguish public, internal, confidential, and highly restricted information. The more sensitive the information, the stronger the encryption, access controls, monitoring, and authentication should generally become. Risk-based protection allows organizations to secure important information without creating unnecessary complexity.
How Data in Motion Travels Across Networks
Data rarely moves as one continuous piece from its original location to its final destination. Most network communication divides information into smaller units that can travel through routers, switches, wireless access points, gateways, servers, and other infrastructure. These components help determine where information should go and how it should reach its destination efficiently. Depending on the network architecture, a transfer may cross multiple systems before reaching the intended application or user. Each point along that journey can potentially become part of the security boundary. Secure network design therefore considers the entire communication path rather than protecting only the sending and receiving devices. Visibility into these pathways also helps security teams identify unexpected or unauthorized data transfers.
The internet is one of the most common environments through which data in motion travels. When someone opens a website, their browser sends requests to servers and receives information needed to display the page. Secure websites generally use encrypted connections so that intermediaries cannot easily read the information being exchanged. Similar communication occurs when people sign into online banking services, use cloud applications, stream content, or submit online forms. Without appropriate encryption, information traveling across public networks may be vulnerable to interception. Secure communication protocols create protected channels between systems so transmitted information is much harder for unauthorized parties to understand. This makes encryption in transit one of the foundations of modern internet security.
Private business networks also carry enormous amounts of data in motion. Employees regularly access internal databases, shared folders, enterprise applications, printers, communication systems, and other network resources. Organizations sometimes assume internal traffic is automatically trustworthy because it remains inside corporate infrastructure. However, compromised devices, malicious insiders, configuration mistakes, or unauthorized network access can expose internal communications as well. Modern security strategies increasingly treat internal network traffic as something that should be authenticated, monitored, and appropriately encrypted. Network segmentation can further restrict how freely devices communicate with one another. These controls help prevent attackers who compromise one system from easily observing or accessing information moving elsewhere across the organization.
Cloud computing has made data movement more complicated because information may constantly travel between different providers, regions, applications, and services. A company might store customer information in one cloud database while processing it through an application hosted somewhere else. The application could then send certain records to analytics software, payment processors, customer relationship management platforms, or backup services. Every integration creates another transmission path that requires appropriate protection. Organizations should understand whether encryption is enabled during each connection rather than assuming cloud providers automatically secure every possible transfer. Secure APIs, identity controls, certificate management, and encrypted network connections can help protect these workflows. Cloud security therefore requires visibility into how services communicate as well as where information is stored.
Mobile devices and wireless networks create another major source of data in transit. Smartphones, tablets, laptops, smart sensors, and connected equipment frequently exchange information through Wi-Fi, cellular networks, Bluetooth, or other wireless technologies. Wireless communication can increase exposure because signals travel through the surrounding environment rather than remaining inside physical cables. Strong wireless encryption and secure application connections help reduce this risk. Organizations may also use virtual private networks or secure access technologies when employees connect from untrusted locations. Device security remains important because an encrypted network connection cannot compensate for a compromised endpoint. Effective protection therefore combines secure transmission methods with authentication, endpoint security, access controls, and continuous monitoring.
Common Examples of Data in Motion
Email provides one of the most familiar examples of data in motion. When someone sends a message, the email travels from the user’s device through mail infrastructure before reaching the recipient’s mailbox. Attachments, message content, sender information, and other metadata may all move across different servers during this process. Depending on the configuration, different portions of the journey may use encrypted communication channels. Businesses frequently exchange confidential contracts, financial documents, customer information, and internal discussions through email, making transmission security particularly important. Phishing attacks can also compromise accounts and allow attackers to access information legitimately transmitted through the system. Strong authentication and secure mail infrastructure therefore complement encryption when protecting email communications.
Online shopping creates several simultaneous examples of data in transit. A customer’s browser communicates with an ecommerce server while displaying products, creating an account, submitting shipping information, or completing an order. Payment information may then travel to a separate payment processor for authorization. Order details might also move into inventory, shipping, analytics, or customer relationship management systems. Each transfer represents another opportunity where sensitive information must remain protected. Secure HTTPS connections, carefully designed APIs, limited data exposure, and appropriate authentication help reduce these risks. Ecommerce security is therefore not limited to protecting the website itself. Businesses must consider the entire chain of systems handling customer information during and after a transaction.
Cloud collaboration tools generate data in motion throughout the working day. Employees may upload documents, edit shared files, participate in video calls, send instant messages, or synchronize folders across multiple devices. Every action involves information traveling between endpoints and cloud infrastructure. Remote and hybrid work have increased the importance of these communication paths because employees frequently operate outside traditional corporate networks. Secure cloud applications typically encrypt network connections, but organizations must still manage user accounts, permissions, sharing settings, and device security. An encrypted transfer sent to an unauthorized account remains a security problem even when interception is prevented. Data protection therefore requires both secure transportation and control over who can legitimately receive the information.
APIs are another major source of data in motion in modern digital environments. Applications use application programming interfaces to automatically request, send, and update information between different services. A travel application might request pricing information from external providers, while a business platform might send customer records into accounting or marketing systems. These exchanges can happen thousands or millions of times without users seeing the underlying communication. Poorly protected APIs may reveal sensitive data, expose authentication credentials, or allow unauthorized requests. Organizations should use encrypted connections, strong authentication, appropriate authorization, rate controls, and careful data validation when building APIs. Monitoring API activity can also reveal unusual behavior that might indicate abuse or compromised credentials.
Real-time technologies such as video conferencing, voice calls, online gaming, connected vehicles, and Internet of Things devices continuously produce data in motion. Unlike a single document upload, these technologies may maintain ongoing streams of information between multiple endpoints. Smart devices can transmit location details, sensor measurements, operational data, diagnostic information, or user activity. Business equipment may similarly report performance information to remote management platforms. Continuous communication increases the importance of secure device identities and encrypted network protocols. Organizations should also consider whether every transmitted piece of information is genuinely necessary. Reducing unnecessary data collection and transmission can decrease both privacy risk and the amount of information attackers could potentially obtain.
What Security Risks Affect Data in Motion?
Interception is one of the most recognizable threats to information traveling across a network. If attackers can observe an inadequately protected communication channel, they may capture transmitted information before it reaches its intended destination. Sensitive information such as usernames, passwords, payment details, business documents, or private messages can create serious consequences if transmitted without strong encryption. Public or poorly secured wireless networks can increase concern because organizations have less control over the surrounding infrastructure. Encryption makes intercepted information significantly harder to interpret because the attacker does not possess the necessary cryptographic keys. However, encryption must be correctly configured and maintained to provide meaningful protection. Outdated protocols or weak configurations can undermine otherwise strong security efforts.
Man-in-the-middle attacks represent another important threat to data in motion. In this type of attack, a malicious actor attempts to position themselves between communicating parties without being detected. The attacker may observe information, redirect communications, steal credentials, or potentially modify transmitted data. Users might believe they are communicating directly with a legitimate website or service even though another system is interfering with the connection. Certificate validation and encrypted communication protocols help establish whether a destination is genuine. Secure DNS technologies, network monitoring, and strong endpoint security can provide additional protection. Organizations should also train employees to recognize certificate warnings and suspicious login pages rather than bypassing security alerts simply to continue working.
Data leakage does not always require a sophisticated attacker. Employees may accidentally transfer sensitive information through personal email accounts, unauthorized cloud platforms, messaging apps, or improperly configured file-sharing services. Applications can also transmit more information than necessary because of weak privacy settings or poor software design. These situations may expose confidential information even when the network connection itself is encrypted. Data loss prevention technologies can help identify sensitive information leaving approved environments. Clear policies and user training are equally important because employees need convenient approved methods for completing legitimate work. Security controls that create excessive friction may encourage people to find unofficial alternatives, unintentionally increasing shadow IT and data exposure.
Compromised endpoints can threaten transmitted data before encryption even becomes relevant. Malware operating on a laptop, smartphone, server, or other device may capture information while a user types it or after an application decrypts incoming communication. This demonstrates why encryption in transit cannot function as a complete cybersecurity strategy on its own. Endpoint detection, operating system updates, application patching, anti-malware protections, and device management remain necessary. Strong authentication can further reduce the damage caused by stolen credentials. Organizations should also monitor devices for abnormal behavior that might indicate compromise. Data security works best as a layered system where network protection, endpoint security, identity controls, application security, and monitoring reinforce one another.
Misconfiguration is another major risk because modern technology environments contain many settings controlling network communication. Administrators may accidentally enable outdated protocols, expose unnecessary services, assign overly broad permissions, or incorrectly configure certificates. Cloud environments can increase configuration complexity because applications often communicate through numerous services and APIs. A single overlooked integration may create an unexpected pathway for sensitive information to leave a protected environment. Regular security assessments can help teams identify these weaknesses before attackers exploit them. Automated configuration monitoring may also detect changes that violate established security standards. Maintaining accurate documentation of data flows makes this work easier because teams can understand which systems communicate, what information they exchange, and what controls should protect each connection.
How Encryption Protects Data in Motion
Encryption transforms readable information into a form that cannot easily be understood without an appropriate cryptographic key. When applied to data in motion, encryption helps protect information as it travels between devices, servers, applications, and networks. Even if an unauthorized party captures encrypted traffic, the content should remain unreadable when modern cryptographic protections are properly implemented. This reduces the likelihood that intercepted passwords, customer information, financial records, or confidential business data can immediately be exploited. Encryption does not prevent every type of cyberattack, but it significantly strengthens confidentiality during transmission. Organizations should treat encrypted communication as a normal security requirement rather than an optional feature. This is particularly important when data crosses public or third-party infrastructure.
TLS, or Transport Layer Security, is one of the most widely used technologies for securing internet communications. It helps create encrypted connections between applications and services, including web browsers and websites. When users visit a properly configured HTTPS website, TLS helps protect information transmitted between the browser and web server. Authentication mechanisms involving digital certificates also help users verify that they are communicating with the expected destination. Modern businesses use TLS for many connections beyond ordinary websites, including APIs, email services, internal applications, and cloud platforms. Keeping implementations current matters because older cryptographic protocols may contain security weaknesses. Organizations should routinely review supported versions, certificate configurations, encryption settings, and expiration dates as part of security maintenance.
Virtual private networks can also protect information moving across untrusted networks. A VPN creates an encrypted communication tunnel between a device and another trusted network or service. Businesses have traditionally used VPNs to give remote employees secure access to internal applications. When someone works from a hotel, home connection, or public network, the encrypted tunnel can reduce exposure to local network interception. However, VPN access should still require strong identity verification because a stolen account could provide an attacker with legitimate network access. Many organizations are also adopting more granular secure access approaches rather than giving remote users broad network connectivity. The underlying principle remains similar: protect communication while limiting access to the resources each user actually needs.
End-to-end encryption provides another security model for certain types of communication. With true end-to-end encryption, information is encrypted on the sending device and designed to remain encrypted until it reaches the intended recipient. Intermediate infrastructure may transport the data without being able to read its content. This model can provide strong confidentiality for messaging, file exchange, or other communication scenarios when correctly implemented. However, organizations must consider operational requirements such as compliance monitoring, data retention, legal obligations, and administrative visibility. End-to-end encryption is therefore not automatically the ideal solution for every business application. Security teams should choose encryption approaches based on the sensitivity of information, communication architecture, regulatory requirements, and legitimate organizational needs.
Encryption keys themselves require careful protection because strong algorithms cannot compensate for exposed cryptographic keys. Key management systems help organizations create, store, rotate, revoke, and control access to encryption keys. Separating key access from ordinary application permissions can reduce the likelihood that one compromised account exposes both encrypted data and the means to decrypt it. Automated certificate management can similarly reduce problems caused by expired or incorrectly configured certificates. Organizations should define ownership for cryptographic infrastructure rather than treating encryption as a configuration that can be forgotten after deployment. Regular reviews help identify outdated algorithms and unnecessary certificates. Strong encryption therefore depends not only on mathematics but also on disciplined operational security practices.
Best Ways to Protect Data in Motion
A strong data protection strategy begins with understanding what information the organization has and where that information travels. Security teams cannot reliably protect communication paths they do not know exist. Data flow mapping can identify connections between employee devices, business applications, databases, cloud services, APIs, vendors, and external users. Organizations should document what information moves through each connection and determine its sensitivity. This visibility also makes it easier to identify outdated integrations or unnecessary data transfers. When possible, businesses should reduce the amount of sensitive information transmitted between systems. Data minimization lowers exposure because information that is never transmitted cannot be intercepted during transmission.
Encryption should be enabled for sensitive information traveling through both external and internal networks. HTTPS and modern TLS configurations can protect web traffic, while secure protocols should replace outdated methods for file transfers, administration, and system communication. Organizations should avoid assuming that internal networks are automatically safe from observation. Malware, unauthorized devices, compromised employee accounts, and lateral movement can make internal encryption valuable as well. Encryption policies should clearly define which communication methods are approved. Centralized configuration standards can prevent individual teams from choosing weaker security settings for convenience. Regular testing is also useful because organizations need to confirm that intended encryption controls actually remain active after infrastructure changes or software updates.
Identity and access management should work alongside encrypted communication. Encryption can protect information from network interception, but it does not prevent an authorized connection from being established using stolen credentials. Multi-factor authentication makes account compromise more difficult by requiring additional proof beyond a password. Role-based access controls can restrict employees and applications to the information needed for their responsibilities. Privileged accounts deserve especially strong protection because they may access sensitive systems or change security configurations. Organizations should regularly review access rights and remove permissions that are no longer required. Combining strong identity verification with encrypted connections creates a stronger security model than relying on either technology alone.
Network segmentation can limit how freely data and devices move across an organization. Instead of placing every system inside one broadly accessible network, segmentation separates resources according to function, sensitivity, or risk. Security controls can then restrict which systems are allowed to communicate between segments. If attackers compromise one endpoint, these boundaries may prevent them from immediately reaching sensitive databases or administrative systems. Zero trust approaches build on a similar principle by continuously evaluating access rather than automatically trusting activity simply because it originates inside a corporate network. Authentication, device health, user identity, and application context can all influence access decisions. Limiting communication pathways reduces the number of opportunities through which sensitive data can move unnecessarily.
Monitoring provides the visibility needed to detect suspicious information transfers. Network security tools can identify unusual destinations, unexpected traffic volumes, abnormal protocols, or other activity that differs from normal business behavior. Data loss prevention systems can look for sensitive information being transmitted through unauthorized channels. Security information and event management platforms may combine events from networks, applications, endpoints, and identity systems to help analysts investigate incidents. Effective monitoring should focus on meaningful risk rather than collecting endless alerts that teams cannot review. Organizations also need clear incident response procedures describing what happens when suspicious data movement is detected. Fast detection and containment can significantly reduce the impact of a successful security breach.
Data in Motion Security in Cloud and Remote Work
Cloud adoption has changed how businesses think about network boundaries. In traditional environments, organizations could concentrate security controls around corporate offices and privately managed data centers. Modern employees may connect directly to cloud applications without their traffic ever passing through an office network. Business information can also travel between multiple software-as-a-service platforms through automated integrations. Security teams therefore need visibility that extends beyond physical locations. Cloud access controls, secure web gateways, identity systems, and application monitoring can help organizations manage these decentralized connections. The goal is to protect information wherever users and services interact with it. Security policies should follow the identity, application, device, and sensitivity of the data rather than depending entirely on physical network location.
Remote work introduces additional challenges because employees connect through networks that businesses do not control. Home routers may have outdated software, public Wi-Fi can expose devices to unfamiliar network environments, and personal equipment may not meet corporate security standards. Organizations can reduce these risks by managing company devices, enabling disk and network encryption, enforcing strong authentication, and maintaining software updates. Secure access technologies can provide protected connections to business applications without unnecessarily exposing entire internal networks. Employee education remains important because remote workers frequently encounter phishing attempts designed to steal login credentials. A secure remote-work program combines technology, policies, and practical user guidance rather than expecting employees to solve complex cybersecurity problems themselves.
Software-as-a-service platforms also require careful configuration because secure transmission alone does not guarantee secure information sharing. Employees can unintentionally make cloud documents publicly accessible or share confidential information with external accounts. Administrators should configure sensible default sharing restrictions and monitor unusual file activity. Single sign-on can simplify identity management by giving organizations centralized control over employee authentication. When someone leaves the company, centralized account management can help revoke access across connected applications more quickly. Organizations should also evaluate which third-party services employees are permitted to use. Unapproved cloud applications may create hidden data flows that security teams cannot effectively monitor, making shadow IT a significant data governance concern.
API security becomes particularly important in cloud environments because services increasingly communicate without direct human interaction. Organizations should authenticate every sensitive API request and verify that the requesting identity is authorized to perform the specific action. Tokens and credentials used by software services require careful storage because exposed secrets can allow attackers to impersonate legitimate applications. API gateways can help centralize authentication, traffic controls, logging, and security policies. Developers should also avoid returning unnecessary information in API responses. Limiting responses to required fields reduces the amount of sensitive data transmitted between systems. Secure software development practices can therefore reduce data-in-motion risks before applications ever reach production.
Third-party risk management completes the cloud security picture because organizations frequently send information to external vendors. Payment processors, marketing platforms, analytics providers, payroll systems, customer support tools, and numerous other services may receive business information. Companies should understand what data each provider receives, why it is needed, how it is transmitted, and how long it is retained. Contracts and security assessments can establish expectations for protecting sensitive information. Access to integrations should also be reviewed periodically because old connections may remain active after employees stop using a service. Removing unnecessary integrations reduces attack surface and simplifies governance. Protecting data in motion therefore involves managing the entire digital supply chain, not only infrastructure directly owned by the organization.
Building a Long-Term Data-in-Motion Security Strategy
Effective security starts with classification because organizations cannot protect every piece of information equally. Teams should identify categories such as public, internal, confidential, and highly restricted information according to business impact and legal obligations. Once data is classified, organizations can determine which communication channels are appropriate for each category. Highly sensitive information may require stronger encryption, more limited sharing permissions, enhanced logging, or additional authentication. Classification should remain understandable enough that employees can apply it during everyday work. Complicated policies that nobody remembers rarely improve security. Clear guidance makes it easier for users to determine whether information can be emailed, uploaded, shared externally, or transmitted through particular business applications.
Organizations should also maintain an inventory of communication technologies and network protocols. Older systems can remain operational for years even after more secure alternatives become available. Legacy applications may rely on outdated encryption or insecure transmission methods because changing them appears inconvenient. Periodic technology reviews can identify these weaknesses and prioritize modernization according to risk. Security teams should work with business owners rather than simply disabling systems without understanding operational impact. Migration plans can replace outdated technologies gradually while preserving essential business processes. Establishing minimum encryption and protocol standards gives technical teams a clear baseline for new systems. Over time, this reduces inconsistencies and prevents outdated security practices from repeatedly appearing across the environment.
Automation can improve data-in-motion security when organizations operate large or rapidly changing technology environments. Automated certificate management can reduce outages and security gaps caused by expired certificates. Configuration monitoring tools can identify systems that accidentally stop enforcing encryption. Cloud security technologies can discover newly created services and evaluate them against established policies. Automated alerts can also flag unusual data transfers or unexpected communication with external destinations. However, automation should support rather than replace human judgment. Security teams still need to investigate context, determine business impact, and decide how to respond to unusual events. Combining automated detection with experienced analysts can create faster and more consistent security operations.
Employee awareness remains essential because people interact with sensitive information every day. Staff members should understand why approved communication channels matter and recognize the risks of sending confidential information through personal accounts or unauthorized applications. Training should focus on realistic scenarios rather than overwhelming employees with technical cybersecurity terminology. For example, employees can learn how to verify unusual file-sharing requests, recognize phishing attempts, and report accidental disclosures quickly. Managers should reinforce these practices by choosing secure tools that are practical for everyday work. When approved systems are difficult to use, employees may search for easier alternatives. Good security design therefore combines strong controls with a user experience that supports legitimate productivity.
Finally, data-in-motion security should be treated as an ongoing program rather than a one-time project. Technology environments change continuously as organizations adopt new applications, cloud services, vendors, devices, and business processes. Security policies that accurately reflected information flows two years ago may no longer describe the current environment. Regular reviews can identify new transmission paths and determine whether existing protections remain appropriate. Incident investigations should also feed lessons back into security improvements. Metrics such as encryption coverage, insecure protocol usage, unauthorized transfers, and access-control violations can help teams measure progress. Organizations that continually improve visibility, encryption, identity security, monitoring, and governance are better positioned to protect information throughout its digital journey.
Frequently Asked Questions About Data in Motion
What is data in motion in simple terms?
Data in motion is information that is actively traveling between devices, applications, servers, networks, or cloud services. Examples include sending an email, uploading a document, entering payment information online, or an application transferring information through an API.
What is the difference between data in motion and data at rest?
Data in motion is information traveling from one location or system to another, while data at rest is information stored on a device, server, database, backup, or cloud storage platform. The same information may switch between these states repeatedly during normal use.
What is the biggest risk to data in motion?
Unauthorized interception is a major risk because attackers may attempt to capture sensitive information while it travels across a network. Other important risks include man-in-the-middle attacks, stolen credentials, compromised endpoints, insecure APIs, misconfiguration, and accidental data leakage.
How can businesses protect data in transit?
Businesses can protect transmitted information by using modern encryption, secure network protocols, strong authentication, access controls, network segmentation, secure APIs, and continuous monitoring. Protecting endpoints and managing encryption keys are also important because network encryption alone cannot prevent every form of compromise.
Is encrypted data in motion completely secure?
Encryption greatly reduces the risk of information being read during interception, but it does not make a system completely immune to attack. Stolen credentials, compromised devices, vulnerable applications, weak key management, configuration errors, and authorized misuse can still expose sensitive information even when network traffic is encrypted.