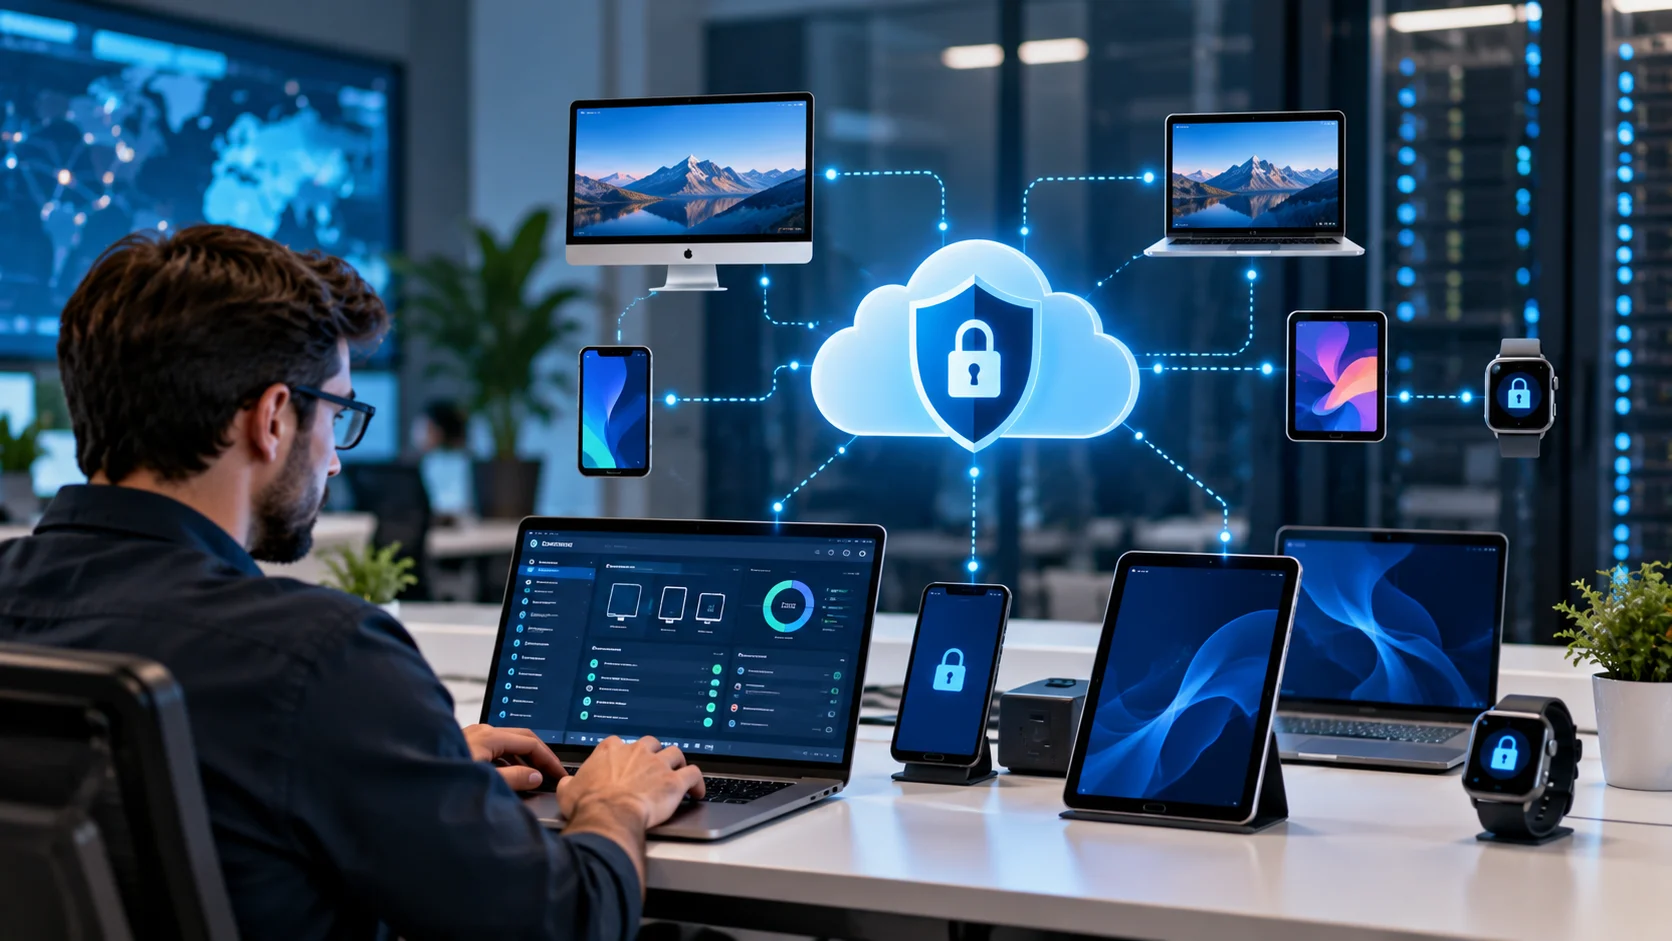
Mobile devices have become essential tools for communication, remote work, and everyday business operations. Employees regularly use smartphones, tablets, and laptops to access company emails, files, and applications. However, these devices can introduce security risks when they are lost, stolen, outdated, or improperly configured. This is where Mobile Device Management (MDM) plays an important role in cybersecurity.
Understanding what MDM is in cyber security helps organizations protect sensitive information while allowing employees to work across different locations and devices. MDM technology enables IT teams to manage devices, enforce security policies, and monitor compliance from a centralized platform. This guide explains how MDM works, its main features, benefits, limitations, and role in modern cybersecurity.
What Is MDM in Cyber Security?
MDM stands for Mobile Device Management, a cybersecurity and IT administration technology used to manage and secure mobile devices within an organization. It allows administrators to configure device settings, enforce security requirements, and monitor compliance through a centralized management platform. MDM solutions commonly support smartphones, tablets, and, depending on the platform, laptops and other endpoints.
The primary purpose of mobile device management is to protect organizational information accessed through managed devices. IT teams can establish security policies that require screen locks, device encryption, and approved operating system versions. These controls help reduce risks associated with unauthorized access, lost equipment, and devices that do not meet company security standards.
MDM is especially important for businesses supporting remote work and employees using multiple devices. It helps organizations maintain consistent security settings without manually configuring every device. However, MDM is not a complete cybersecurity solution and should work alongside identity management, endpoint protection, network security, and employee security awareness programs.
How Does Mobile Device Management Work?
Mobile device management works through a centralized administration system that communicates with enrolled devices using supported operating system management frameworks. Organizations use an MDM platform to establish configuration requirements and distribute security policies. Once a device is enrolled, administrators can manage permitted settings and review information about its compliance status.
The management platform sends authorized commands and configurations to devices through supported communication services and operating system interfaces. These instructions may involve applying passcode requirements, installing approved applications, or configuring network access. The precise capabilities depend on the device platform, ownership model, enrollment method, and permissions granted to the organization.
After enrollment, the MDM system can check whether managed devices meet established security requirements. For example, a device running an unsupported operating system might be marked noncompliant. When integrated with identity and access management tools, this information can help organizations restrict access to company resources until the device meets relevant security standards.
Key Features of Mobile Device Management
One important MDM feature is centralized device configuration, which allows IT administrators to apply consistent settings across supported devices. Instead of manually configuring each smartphone or tablet, administrators can distribute approved policies from one management console. This approach helps organizations maintain standard security settings while reducing repetitive administrative tasks.
Device compliance monitoring is another essential capability of mobile device management software. Administrators can check whether enrolled devices meet requirements involving encryption, screen locks, operating system versions, and other security conditions. These checks provide useful visibility into device security and help identify equipment that requires attention before accessing sensitive company resources.
MDM platforms may also support application deployment, remote locking, and selective or complete device wiping, depending on the platform and enrollment type. Some systems provide inventory information and configuration reporting. These capabilities help IT teams manage the device lifecycle, although privacy restrictions and technical limitations determine which actions administrators can perform.
How Devices Are Enrolled in an MDM System
Device enrollment is the process of registering a supported device with an organization’s mobile device management platform. Enrollment establishes the management relationship needed to apply security settings and collect permitted device information. Organizations may use different enrollment approaches depending on whether the device belongs to the business or an individual employee.
Company-owned devices can often be enrolled during initial setup through supported automated provisioning services. This allows businesses to configure security requirements and applications before employees begin using their devices. Automated enrollment can reduce setup time and make it easier to maintain consistent configurations across larger groups of business equipment.
Personally owned devices may use different enrollment methods that limit organizational control and protect private information. In some cases, employees register a work profile or managed environment rather than granting full-device administration. The enrollment process should clearly explain what the organization can manage, which information administrators can access, and what happens when enrollment ends.
MDM Security Policies and Data Protection
Security policies are central to mobile device management because they define the requirements devices must follow. Common examples include requiring strong passcodes, enabling supported encryption, and maintaining approved operating system versions. Consistent policy enforcement can reduce preventable weaknesses that might otherwise expose company information to unauthorized access.
MDM may also help organizations configure secure connections and manage access to business applications. Depending on the system, administrators can distribute Wi-Fi settings, certificates, and VPN configurations to enrolled devices. These features simplify device setup while supporting more consistent access controls for employees working in offices or remote locations.
Some organizations connect MDM compliance information with conditional access policies. These policies can consider device security status before allowing access to certain company services. However, MDM alone cannot prevent every form of data theft, phishing, or account compromise, making identity protection and ongoing security monitoring equally important.
MDM and Bring Your Own Device (BYOD) Security
Bring Your Own Device, commonly called BYOD, is a workplace arrangement that allows employees to use personally owned devices for business activities. These may include accessing company email, communicating with colleagues, or using approved work applications. Although convenient, BYOD creates additional challenges because personal and organizational information may share the same device.
MDM can help manage these challenges through supported enrollment options and security policies. For example, an organization may require certain device protections before permitting access to sensitive business resources. Some mobile operating systems also support separate work environments that help distinguish managed business information from personal applications and content.
Privacy is particularly important when introducing MDM into a BYOD environment. Employees should understand what information their employer can see and which actions the system permits. Clear policies, appropriate enrollment methods, and limited management permissions can help organizations protect business information without requesting unnecessary control over employees’ personal devices.
How MDM Protects Lost or Stolen Devices
Lost or stolen devices can create security concerns when they contain business emails, documents, or access credentials. Mobile device management helps organizations prepare for these situations by enforcing protective settings before a device disappears. Passcodes, encryption, and appropriate authentication requirements can reduce the risk of unauthorized access to stored information.
Certain MDM platforms allow authorized administrators to remotely lock or wipe enrolled devices. A remote wipe may remove organizational information or erase a device more extensively, depending on its ownership and management configuration. These actions generally require supported device capabilities and communication with the management service, so immediate execution is not always possible.
Organizations should establish clear procedures for reporting missing devices and responding to potential information exposure. MDM actions may be combined with account access reviews and other security measures. Preparing these procedures in advance can help security teams respond more effectively while avoiding unnecessary removal of personal information from employee-owned equipment.
MDM vs MAM vs UEM: What’s the Difference?
Mobile Device Management focuses primarily on configuring, securing, and monitoring enrolled devices. Mobile Application Management, commonly called MAM, focuses on managing specific applications and protecting organizational data within them. Although these technologies overlap, their management scope differs, particularly when employees use personal devices for work.
For example, MAM may allow an organization to apply security restrictions to approved business applications without fully enrolling the underlying device. This can be useful for BYOD environments where employees want to maintain control over personal information. MDM provides broader device-level capabilities, while MAM concentrates on application behavior and data protection.
Unified Endpoint Management, or UEM, extends centralized administration across multiple categories of endpoints. Depending on the platform, these may include smartphones, tablets, laptops, and desktop computers. Modern UEM products often combine MDM and MAM features, giving organizations a broader approach to managing different device types through a coordinated security environment.
Benefits of MDM for Businesses and Organizations
One major benefit of MDM is improved consistency in device security management. Organizations can apply approved configuration requirements across supported devices rather than relying entirely on individual employees. This helps reduce differences in security settings and provides administrators with better visibility into equipment that connects to company resources.
MDM can also improve operational efficiency by simplifying device setup, configuration, and routine administration. IT departments may remotely distribute applications and settings, reducing the need to handle every device physically. These features are particularly valuable for organizations managing remote employees, multiple office locations, or frequently changing device inventories.
Another advantage is improved support for organizational security and compliance processes. Device inventory information, compliance reports, and documented security policies can contribute to internal oversight. However, using MDM does not automatically guarantee compliance with legal requirements or industry standards, which may demand additional technical, administrative, and organizational controls.
Common MDM Security Risks and Limitations
Although mobile device management strengthens security administration, it introduces challenges that organizations must address. One concern is the risk of misconfigured policies that unintentionally restrict legitimate applications or disrupt employee productivity. Poorly planned configurations can create frustration, particularly when different device platforms require different management settings or permissions.
Privacy and trust are also important considerations, especially in BYOD environments. Employees may be concerned about what their employer can monitor or control on personal devices. Organizations should explain management capabilities accurately and use enrollment approaches that match the intended purpose rather than requesting unnecessary administrative privileges.
MDM systems also have technical limitations because they depend on supported operating system features, device connectivity, and administrative permissions. A compromised account or improperly secured management platform can create additional security risks. Strong administrator authentication, access restrictions, system updates, and regular configuration reviews are necessary for responsible MDM operation.
How to Choose the Right MDM Solution
Choosing a suitable MDM solution begins with understanding the devices and operating systems used within an organization. Businesses should identify whether they primarily manage Android devices, Apple products, Windows computers, or a combination of platforms. Compatibility is important because management features and security capabilities can vary considerably between operating systems.
Organizations should evaluate practical requirements such as enrollment options, security policies, device inventory, application management, and reporting capabilities. Integration with existing identity systems and business applications may also influence the decision. A solution that fits established workflows can be easier to maintain than one that introduces unnecessary complexity.
Cost, scalability, vendor support, and privacy controls deserve attention during evaluation. Organizations should consider whether the platform can support future device growth and changing security requirements. Testing an MDM solution with a small group of representative devices can help identify limitations before deploying it across the entire organization.
Best Practices for Implementing MDM Security
Successful MDM implementation begins with a clear understanding of organizational security objectives. IT teams should identify the information and services requiring protection, the devices that access them, and the management controls that are appropriate. Establishing these requirements early helps prevent overly restrictive policies and reduces confusion during device enrollment.
Organizations should apply appropriate device security settings, keep supported software updated, and limit administrative privileges. Employees need clear guidance about enrollment, privacy expectations, and procedures for reporting lost devices. Regular policy reviews can help ensure that security requirements remain practical as operating systems, device capabilities, and workplace needs change.
MDM should also be integrated with broader cybersecurity practices, including strong authentication, access management, endpoint security, and employee awareness training. Administrators should monitor compliance information and investigate meaningful security events when necessary. A balanced approach protects organizational information while supporting employee productivity and respecting appropriate privacy boundaries.
Conclusion
Mobile Device Management is an important technology for protecting and administering devices that access organizational information. It allows IT teams to enforce security policies, manage approved configurations, and review device compliance from centralized platforms. Understanding what MDM is in cyber security helps explain how organizations manage security risks associated with smartphones, tablets, and other connected endpoints.
MDM solutions offer benefits such as consistent device configuration, improved administrative efficiency, and support for protecting lost or stolen equipment. They also help organizations manage company-owned devices and certain BYOD arrangements. However, privacy considerations, technical limitations, and configuration risks mean that MDM must be implemented carefully rather than treated as a complete security solution.
A successful mobile device security strategy combines appropriate MDM capabilities with identity protection, employee education, access controls, and regular security reviews. Organizations should select management features based on their actual devices, operational needs, and data protection requirements. With thoughtful implementation, MDM can support a more secure and manageable digital workplace.
Frequently Asked Questions
What does MDM stand for in cyber security?
MDM stands for Mobile Device Management. It is a technology that allows organizations to configure, monitor, and secure enrolled smartphones, tablets, and other supported devices through a centralized administration platform.
What is the main purpose of MDM?
The main purpose of MDM is to manage device configurations and enforce organizational security requirements. It helps protect business information, maintain device compliance, and support centralized administration across multiple devices.
Can MDM access personal information on a phone?
MDM visibility depends on the operating system, enrollment method, ownership, and configured permissions. Some enrollment types provide limited management access, while others allow broader administrative control. Organizations should clearly explain these capabilities.
What is the difference between MDM and MAM?
MDM focuses on managing and securing enrolled devices, while MAM focuses on controlling specific applications and organizational information within them. Both approaches can be combined to support business security requirements.
Is MDM necessary for every business?
Not every business requires the same level of mobile device management. However, organizations with employees accessing sensitive information through multiple devices may benefit from MDM or other suitable endpoint security controls.