What Does CIA Stand for in Cyber Security?
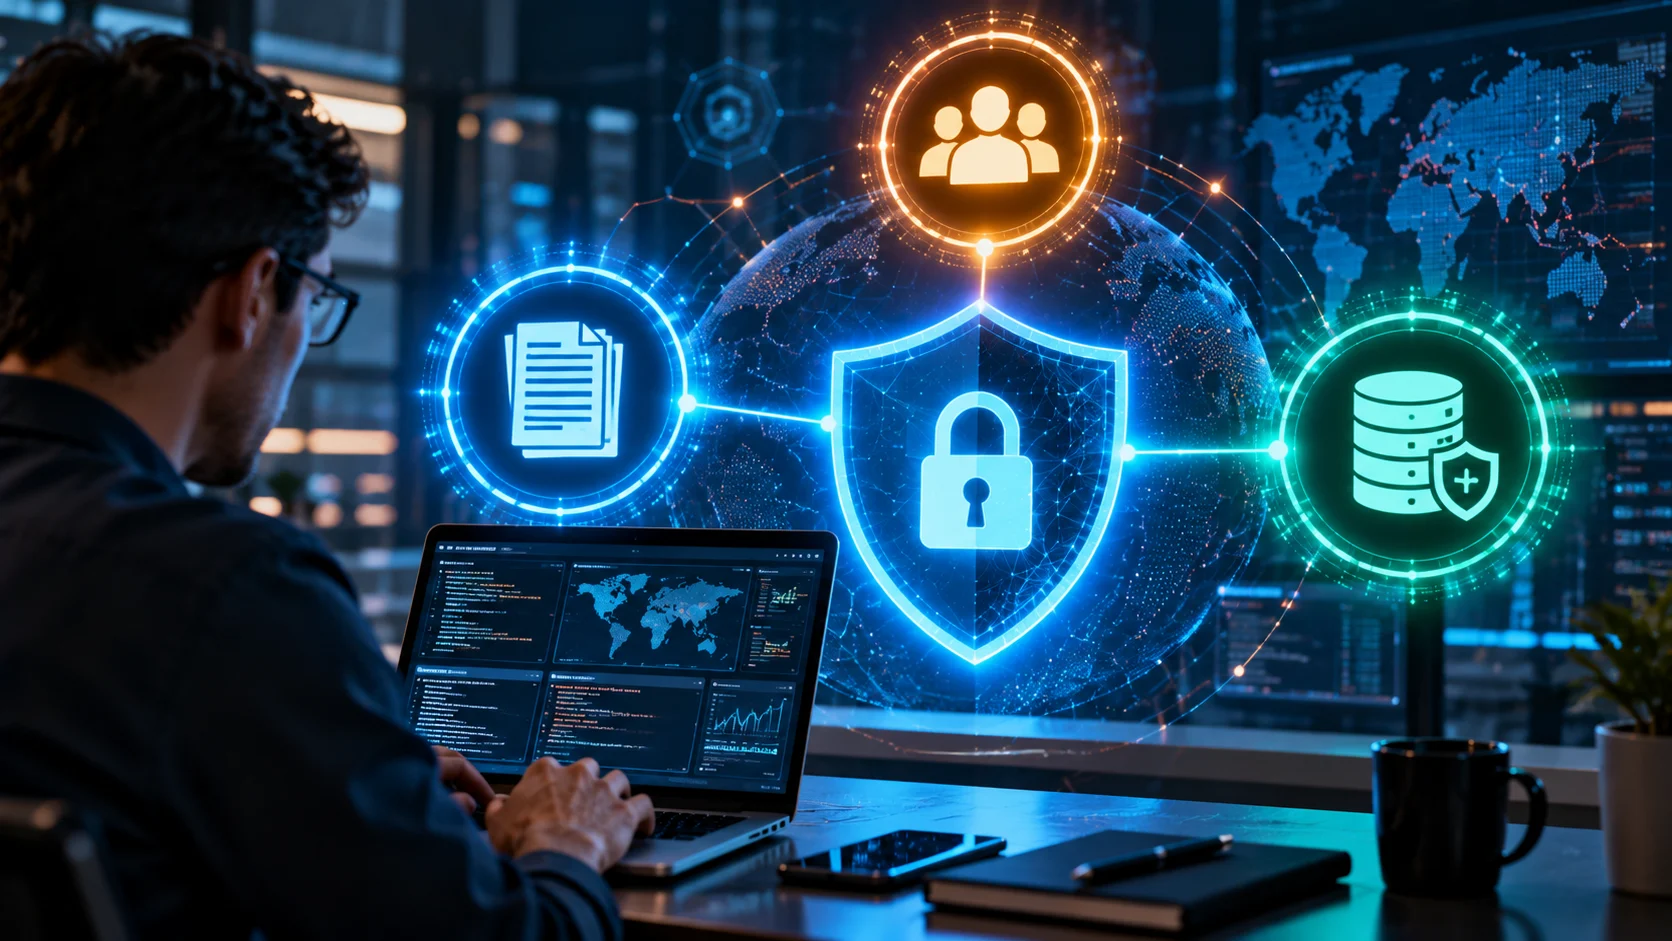
CIA in cyber security stands for Confidentiality, Integrity, and Availability, the three fundamental principles of information security. Together, these principles form the CIA triad, a widely used framework for protecting sensitive information, computer systems, and digital resources. Organizations use this model to understand security requirements, identify potential risks, and develop effective strategies for safeguarding valuable business information.
Each component of the CIA triad addresses a different aspect of information protection. Confidentiality prevents unauthorized access, integrity ensures that information remains accurate and trustworthy, and availability ensures that authorized users can access resources when needed. These principles work together to create a balanced cybersecurity strategy that protects information against different threats and operational disruptions.
Understanding what CIA stands for in cyber security is essential for students, IT professionals, business owners, and anyone interested in digital safety. The framework provides a foundation for evaluating security controls and making informed protection decisions. Whether an organization manages customer records, financial transactions, or cloud applications, the CIA triad helps establish clear information security priorities.
Understanding the CIA Triad in Information Security
The CIA triad is a foundational information security model used to evaluate how organizations protect their digital and physical information assets. It consists of three interconnected objectives that guide cybersecurity policies, technical controls, and risk management decisions. By applying these principles, organizations can identify weaknesses and determine which protective measures are appropriate for their systems.
Although the CIA triad appears simple, its principles apply to complex technology environments, including cloud computing, enterprise networks, and mobile applications. Security professionals use the model to assess potential threats and their consequences. For example, stolen customer information affects confidentiality, unauthorized database changes threaten integrity, and unavailable servers disrupt availability.
The framework also helps organizations recognize that cybersecurity involves more than preventing hackers from accessing systems. Information must remain accurate, accessible, and protected throughout its lifecycle. A system with strong encryption but unreliable uptime may still fail to meet business requirements, demonstrating why all three CIA principles deserve attention.
Confidentiality: Protecting Sensitive Information
Confidentiality is the first principle of the CIA triad and focuses on preventing unauthorized access to sensitive information. It ensures that personal details, business records, passwords, and confidential documents are available only to approved individuals. Organizations maintain confidentiality through policies and security technologies that restrict who can view or disclose protected information.
Common confidentiality controls include encryption, access permissions, authentication, and data classification. Encryption transforms readable information into protected data that requires the appropriate key for access. Meanwhile, role-based access control helps employees view only the information necessary for their responsibilities, reducing unnecessary exposure and limiting the potential impact of compromised accounts.
Confidentiality becomes especially important when organizations handle financial records, healthcare information, customer identities, or proprietary business materials. Unauthorized disclosure can damage customer trust and create legal or financial consequences. By combining technical safeguards with employee awareness and clear security procedures, businesses can reduce the likelihood of accidental exposure and unauthorized information access.
Integrity: Keeping Data Accurate and Trustworthy
Integrity is the second component of the CIA triad and ensures that information remains accurate, complete, and protected against unauthorized modification. Organizations depend on trustworthy data to make decisions, process transactions, and maintain reliable records. When information changes unexpectedly or becomes corrupted, the consequences may affect business operations and customer confidence.
Security professionals protect data integrity through mechanisms such as cryptographic hashes, digital signatures, database controls, and audit logs. These technologies can help detect unexpected changes or verify that information originates from a trusted source. However, each control addresses specific risks, and successful integrity protection generally requires several complementary safeguards.
Consider an online banking system that processes account balances and financial transactions. Even when customer information remains confidential, unauthorized changes to transaction records could create serious problems. Integrity controls help detect manipulation and support reliable processing, ensuring that information remains dependable during storage, transmission, and everyday business operations.
Availability: Ensuring Reliable Access to Systems
Availability is the third principle of the CIA triad and focuses on ensuring that authorized users can access information and technology resources when required. Systems must remain operational and responsive to support normal business activities. Availability includes maintaining reliable networks, functioning applications, accessible databases, and appropriate recovery capabilities during unexpected disruptions.
Organizations improve availability through redundancy, system monitoring, backups, disaster recovery planning, and regular maintenance. Redundant infrastructure can reduce dependence on a single component, while monitoring tools help identify developing problems. Properly tested recovery procedures allow organizations to restore essential services when equipment failures, cyberattacks, or environmental incidents interrupt operations.
For example, an online retail website must remain accessible so customers can browse products and complete purchases. If a server outage prevents access, the business may lose revenue even when customer data remains confidential and accurate. Availability planning helps reduce downtime and maintain dependable services during normal conditions and unexpected incidents.
Why the CIA Triad Is Important in Cyber Security
The CIA triad provides a practical foundation for building comprehensive cybersecurity programs. Instead of focusing exclusively on blocking unauthorized access, it encourages organizations to consider data accuracy and service reliability. This balanced approach helps security teams identify multiple types of risks and choose controls that address the organization’s actual information protection needs.
Businesses also use the framework to prioritize security investments and evaluate potential consequences. A healthcare provider may emphasize patient record confidentiality while also requiring accurate information and dependable system access. Similarly, an online payment platform must protect financial details, prevent unauthorized transaction changes, and maintain reliable processing capabilities.
Another advantage is the framework’s simplicity, which makes complex security requirements easier to explain to employees and decision-makers. The CIA triad creates a shared vocabulary for discussing digital protection goals. When combined with risk assessments and established security practices, it helps organizations develop policies that support both operational needs and information security objectives.
Real-World Examples of the CIA Triad
A hospital management system offers a useful example of how confidentiality, integrity, and availability work together. Patient records contain private information that should be accessible only to authorized personnel. Those records must also remain accurate, while healthcare professionals need reliable access to essential information during patient care and routine medical operations.
Online banking provides another example because financial platforms depend on all three information security principles. Confidentiality protects account credentials and personal information, integrity safeguards transaction records, and availability ensures customers can access banking services. A failure in any one area can create operational disruption, financial consequences, or reduced trust.
Educational institutions also rely on the CIA triad to protect student records, examinations, and online learning systems. Unauthorized disclosure can compromise privacy, incorrect grades threaten data integrity, and unavailable learning platforms interrupt educational activities. Applying the three principles helps institutions recognize different security responsibilities and develop controls suited to each requirement.
Common Cybersecurity Threats to the CIA Triad
Confidentiality threats include phishing, stolen credentials, unauthorized access, and accidental information disclosure. Attackers may attempt to obtain sensitive information by exploiting technical weaknesses or manipulating users into revealing credentials. Poor access management and misconfigured cloud storage can also expose confidential records, even when no sophisticated cyberattack takes place.
Integrity threats involve unauthorized data modification, malicious software, compromised accounts, and accidental corruption. An attacker who changes financial records or alters application data can undermine trust in business systems. Human errors and faulty software updates may also affect integrity, demonstrating that information protection must address both malicious and unintentional changes.
Availability threats include distributed denial-of-service attacks, hardware failures, natural disasters, and infrastructure outages. Ransomware may also interrupt access to essential systems, affecting both availability and potentially confidentiality or integrity. Identifying these different threats allows security teams to plan appropriate defenses without assuming that one security tool can prevent every problem.
Security Controls That Support Confidentiality
Organizations protect confidentiality by controlling access to sensitive data and limiting unnecessary exposure. Multi-factor authentication adds an additional verification requirement beyond a password, reducing certain risks associated with stolen credentials. Strong identity management policies also help ensure that access permissions reflect individual responsibilities rather than providing excessive privileges.
Encryption is another essential confidentiality control, particularly when protecting stored information and data transmitted across networks. Proper key management is equally important because compromised encryption keys can undermine protection. Secure communication protocols, encrypted storage, and appropriate device security measures help reduce exposure across different technology environments.
Employee education complements technical controls by addressing everyday information handling risks. Training can help staff recognize phishing attempts, manage sensitive documents, and report suspicious activity. Confidentiality protection becomes more effective when organizations combine clear policies, suitable technology, and consistent employee awareness rather than depending entirely on software solutions.
Security Controls That Maintain Data Integrity
Data integrity controls help organizations detect unauthorized changes and maintain confidence in information accuracy. Cryptographic hashing can identify whether data differs from an expected value, while digital signatures can support authenticity and integrity verification. These mechanisms are particularly valuable when information moves between systems or must remain trustworthy over time.
Database permissions and transaction controls also help protect critical business information from inappropriate modification. By restricting editing privileges and maintaining detailed audit records, organizations can reduce unnecessary changes and investigate suspicious activity. Input validation provides another layer of protection by checking whether submitted data meets expected requirements before processing.
Reliable backups and version histories can support recovery when information becomes damaged or incorrectly modified. However, backups do not automatically prevent integrity failures, making monitoring and preventive controls equally important. Testing restoration procedures and reviewing system changes can help organizations identify problems early and maintain more dependable information management practices.
Security Controls That Improve System Availability
Maintaining availability requires organizations to prepare for technical failures, unexpected demand, and security incidents. Redundant servers, network connections, and power systems can reduce the consequences of individual component failures. Load balancing helps distribute application traffic, supporting performance and resilience when multiple systems are available to handle incoming requests.
Regular data backups and disaster recovery planning are also important for restoring disrupted services. Recovery objectives help organizations determine acceptable downtime and potential data loss during major incidents. These requirements guide decisions about backup frequency, infrastructure investment, and the procedures needed to resume operations after unexpected interruptions.
System monitoring and preventive maintenance provide additional availability protection by identifying potential problems before they become severe. Security updates, capacity planning, and incident response procedures help maintain dependable infrastructure. Although complete elimination of downtime is unrealistic, well-designed availability controls can substantially reduce the duration and impact of service disruptions.
CIA Triad vs. Other Cybersecurity Frameworks
The CIA triad differs from broader cybersecurity frameworks because it describes fundamental security objectives rather than a complete implementation process. It identifies what organizations should protect but does not prescribe every action required to achieve protection. Security teams therefore use the model alongside more detailed frameworks, standards, and organizational policies.
For example, the NIST Cybersecurity Framework provides guidance for managing cybersecurity risk through interconnected functions and outcomes. ISO/IEC 27001 establishes requirements for an information security management system. The CIA triad complements these approaches by helping organizations understand the confidentiality, integrity, and availability objectives that many security controls support.
Other security concepts, including authenticity, accountability, and nonrepudiation, extend beyond the three traditional CIA principles. These concepts help verify identities, establish responsibility for actions, and provide evidence of particular activities. Understanding these additional objectives allows security professionals to develop more complete protection strategies without treating the CIA triad as the only consideration.
How the CIA Triad Applies to Cloud Security
Cloud computing introduces important considerations for confidentiality, integrity, and availability because organizations rely on remotely hosted infrastructure and services. Sensitive information may be stored across multiple systems, accessed through network connections, and managed by different parties. Effective cloud security requires understanding how responsibilities are divided between the cloud provider and customer.
Confidentiality controls in cloud environments include identity management, encryption, and carefully configured access permissions. Integrity protection may involve logging, change monitoring, and appropriate data validation. Availability depends on factors such as provider infrastructure, regional redundancy, network connectivity, and the organization’s own backup and recovery arrangements.
A common mistake is assuming that cloud providers automatically handle every cybersecurity responsibility. In practice, customer obligations depend on the service model and contractual arrangements. Applying the CIA triad helps organizations evaluate cloud configurations, identify potential weaknesses, and implement safeguards appropriate for the applications and data they manage.
CIA Triad in Network Security and Risk Management
Network security relies on the CIA triad to protect communication systems, connected devices, and information moving between locations. Confidentiality helps prevent unauthorized interception, integrity supports trustworthy data transmission, and availability maintains dependable network connectivity. These objectives influence the design of firewalls, secure communication protocols, monitoring systems, and network access policies.
During cybersecurity risk assessments, organizations consider threats, vulnerabilities, and the potential consequences of incidents. The CIA triad helps classify those consequences according to information exposure, unauthorized changes, or service disruption. This classification can improve discussions about business impact and guide decisions about which risks require immediate attention.
For example, a company operating an online customer portal may identify credential theft, database manipulation, and server outages as different risks. Each affects particular security objectives and may require different controls. By evaluating all three principles, the organization can avoid concentrating its resources on one threat category while overlooking equally important operational weaknesses.
Challenges of Implementing the CIA Triad
One challenge of applying the CIA triad is balancing security requirements against usability, cost, and operational performance. Strict access controls can improve confidentiality but may create inconvenience when poorly implemented. Likewise, extensive verification procedures can support integrity while increasing processing requirements or administrative workload in certain environments.
Organizations must also recognize that the three principles sometimes involve competing priorities. During a major system incident, restoring availability quickly may introduce risks if systems are brought online before integrity checks are completed. Security teams need clearly defined procedures for making informed decisions when different protection objectives compete.
Another difficulty involves adapting controls to changing technologies and emerging threats. Cloud environments, remote work, connected devices, and evolving attack methods introduce new security considerations. Regular risk assessments, employee education, and control reviews help organizations maintain an appropriate balance between confidentiality, integrity, and availability as business requirements develop.
Best Practices for Applying the CIA Triad
The first step in applying the CIA triad is identifying important information assets and understanding their security requirements. Organizations should classify sensitive data, review access permissions, and determine which systems are essential for business operations. This assessment provides a foundation for selecting controls that reflect actual risks rather than adopting unnecessary technologies.
Next, organizations should implement layered safeguards that address different security objectives. Strong authentication and encryption support confidentiality, while validation and change monitoring help protect integrity. Backups, redundancy, and recovery planning support availability, creating a more complete approach when these measures are implemented and tested together.
Finally, cybersecurity programs should be reviewed regularly as threats, systems, and organizational needs change. Security testing, incident response exercises, and employee awareness programs can help identify weaknesses before serious incidents occur. Consistent monitoring and improvement make the CIA triad a practical decision-making framework rather than simply a theoretical information security concept.
Conclusion
CIA in cyber security stands for confidentiality, integrity, and availability, three essential principles that form the foundation of information security. Confidentiality protects sensitive information from unauthorized access, integrity ensures that data remains accurate and trustworthy, and availability supports reliable access to systems. Together, these objectives help organizations understand what effective cybersecurity protection requires.
The CIA triad applies across many environments, including banking systems, healthcare platforms, enterprise networks, and cloud services. Organizations use the framework to evaluate security risks, select appropriate controls, and improve operational resilience. Although the model does not provide every implementation detail, it offers a clear foundation for broader cybersecurity strategies.
Understanding the CIA triad is valuable for cybersecurity beginners, IT professionals, and business decision-makers alike. By combining access management, integrity verification, system resilience, and regular risk assessments, organizations can address all three objectives effectively. A balanced approach helps protect information while supporting dependable digital operations and long-term business confidence.
Frequently Asked Questions (FAQs)
1. What does CIA stand for in cyber security?
CIA stands for Confidentiality, Integrity, and Availability. These three principles form the CIA triad, a foundational information security model used to protect sensitive data, maintain information accuracy, and ensure reliable access to systems.
2. Why is the CIA triad important in cybersecurity?
The CIA triad helps organizations identify security priorities and evaluate potential risks. It ensures that cybersecurity strategies address unauthorized information access, improper data modification, and disruptions that prevent legitimate users from accessing services.
3. What is an example of the CIA triad?
Online banking demonstrates the CIA triad through protected account information, accurate financial transactions, and reliable service access. These requirements represent confidentiality, integrity, and availability within a familiar digital environment.
4. What is the difference between confidentiality and integrity?
Confidentiality prevents unauthorized individuals from accessing sensitive information. Integrity focuses on ensuring that information remains accurate, complete, and protected from unauthorized or improper changes during storage, processing, and transmission.
5. Does CIA in cybersecurity refer to the Central Intelligence Agency?
No, CIA in cybersecurity usually refers to Confidentiality, Integrity, and Availability when discussing the CIA triad. The Central Intelligence Agency is a separate United States government organization associated with intelligence activities.