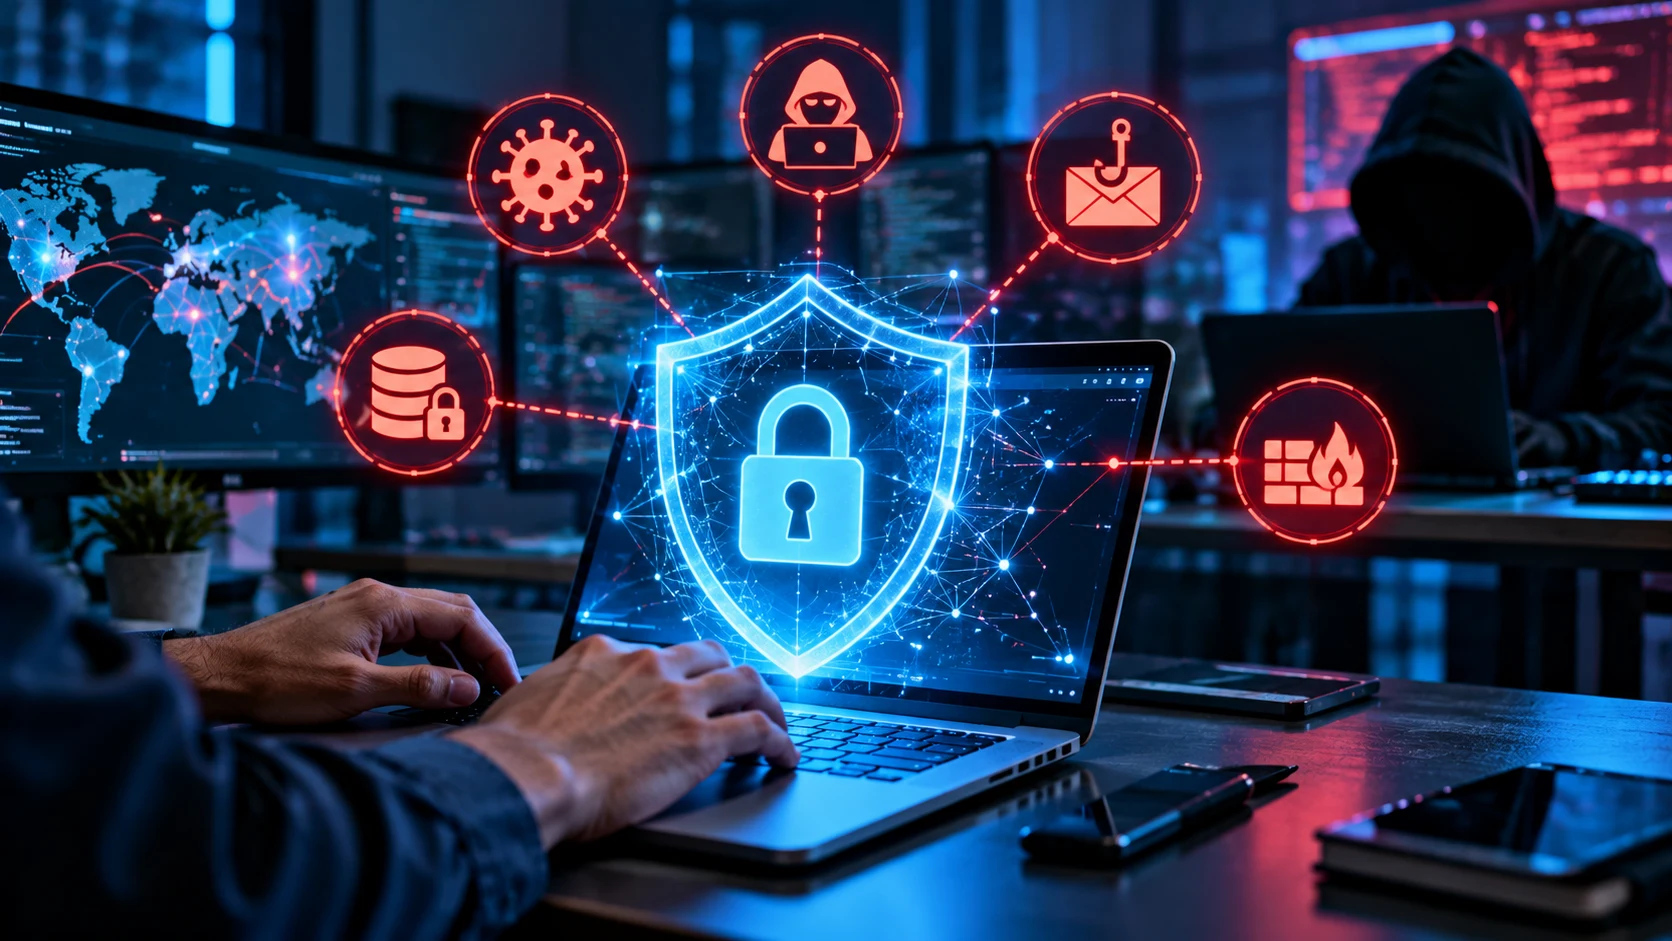
Cybersecurity threats are becoming a major concern as individuals, businesses, and governments increasingly rely on digital technologies. From online banking and social media to cloud computing and business applications, nearly every digital system contains information that needs protection. Cybercriminals often target these systems to steal sensitive data, disrupt operations, or gain unauthorized access to valuable resources.
Understanding what cybersecurity threats are is an important step toward protecting personal information, business networks, and digital assets. These threats can take different forms, including malware, phishing, ransomware, and network attacks. This guide explains the most common cybersecurity threats, how they work, their potential consequences, and the best practices for reducing security risks.
What Are Cyber Security Threats?
Cybersecurity threats are potential dangers that can compromise computer systems, networks, applications, devices, or digital information. These threats may originate from cybercriminals, malicious insiders, automated software, or other sources capable of exploiting security weaknesses. Their purpose or effect may involve stealing confidential information, disrupting digital services, damaging systems, or gaining unauthorized access to protected resources.
A cybersecurity threat is different from a vulnerability, although the two concepts are closely connected. A vulnerability is a weakness in software, hardware, security configuration, or organizational processes that could be exploited. A threat represents a possible source of harm, while a cyberattack occurs when someone actively attempts to exploit weaknesses or compromise a digital system.
Cybersecurity threats can affect organizations of every size, from small businesses to multinational companies and government institutions. Individuals may also encounter threats through emails, mobile applications, websites, and connected devices. Understanding these risks helps users recognize suspicious activities, improve security awareness, and take appropriate measures to protect information from potential attacks.
How Do Cyber Security Threats Work?
Cybersecurity threats often involve identifying weaknesses in digital systems and attempting to exploit them for unauthorized purposes. Attackers may search for outdated software, poorly protected accounts, exposed services, or employees who can be deceived into revealing confidential information. The specific approach depends on the attacker’s objectives, technical capabilities, and available opportunities.
Some attacks rely on malicious software designed to interfere with normal device operations or access sensitive information. Others use social engineering techniques to manipulate people into performing actions that compromise security. Attackers may also abuse stolen credentials or insecure application functions, allowing them to access resources without directly exploiting a software vulnerability.
The consequences of a successful attack depend on the affected system and the information involved. An attacker might gain access to confidential records, interrupt business services, or compromise additional connected resources. Security monitoring, access controls, regular updates, and employee awareness can help organizations detect suspicious activity and reduce the likelihood of serious damage.
1. Malware Attacks and Malicious Software
Malware refers to malicious software designed to harm devices, access information without authorization, or interfere with normal computer operations. Common forms include viruses, worms, Trojans, spyware, and other programs created for harmful purposes. Malware may reach devices through deceptive downloads, malicious attachments, compromised websites, or software installed from untrusted sources.
Different malware categories operate in different ways depending on their intended purpose. Spyware may collect sensitive information, while certain viruses can spread by infecting files or programs. Trojan software disguises itself as something legitimate to encourage installation, whereas worms can sometimes spread between vulnerable systems without requiring the same level of user interaction.
Protecting devices from malware requires a combination of technical security measures and careful online behavior. Updated operating systems, reputable security software, and controlled application installation can reduce common infection risks. Users should also avoid unexpected attachments, verify software sources, and maintain secure backups to limit potential disruption if malicious software affects their systems.
2. Phishing and Social Engineering Threats
Phishing is a common cybersecurity threat in which attackers use deceptive messages to trick people into revealing information or taking unsafe actions. These messages may imitate trusted businesses, banks, employers, or familiar online services. Attackers often create a sense of urgency to encourage recipients to share passwords, disclose financial details, or visit fraudulent websites.
Social engineering extends beyond email phishing and includes other forms of psychological manipulation. Attackers may use phone calls, text messages, social media conversations, or impersonation to gain someone’s trust. Spear phishing targets particular individuals or organizations, while business email compromise often involves deceptive communication designed to manipulate financial or administrative decisions.
Recognizing suspicious communication is an important defense against phishing and social engineering. Users should verify unexpected requests through trusted contact channels rather than relying on information contained within suspicious messages. Multifactor authentication, email filtering, security awareness training, and careful verification of sensitive transactions can help reduce the impact of these threats.
3. Ransomware Attacks and Data Extortion
Ransomware is a type of malicious software commonly associated with restricting access to data or systems and demanding payment. Some ransomware incidents also involve the theft of sensitive information and threats to disclose it. These attacks can interrupt business operations, affect essential services, and create significant financial and reputational consequences for affected organizations.
Ransomware attacks may begin through compromised credentials, malicious attachments, vulnerable software, or other security weaknesses. Once an attacker gains access, the incident may spread beyond a single device if connected systems are not adequately protected. The potential consequences include inaccessible files, interrupted workflows, costly recovery efforts, and exposure of confidential information.
Organizations can reduce ransomware risks by maintaining reliable backups, applying security updates, and limiting unnecessary account privileges. Network segmentation and effective monitoring can also help contain incidents and identify suspicious behavior. A documented incident response plan is particularly important because paying a ransom does not guarantee data recovery or prevent stolen information from being disclosed.
4. Password Attacks and Credential Theft
Password-related attacks occur when unauthorized individuals attempt to obtain or misuse login credentials for online accounts and digital systems. Weak passwords, reused credentials, and compromised authentication information can increase the risk of account access. Attackers may obtain credentials through phishing, previous data breaches, malicious software, or other unauthorized methods.
Credential stuffing involves attempts to reuse previously exposed usernames and passwords across different online services. Password spraying targets accounts using commonly chosen passwords, while other attacks may exploit weak authentication protections. These threats are particularly concerning when compromised accounts provide access to business applications, confidential records, or administrative privileges.
Using long, unique passwords for every important account helps reduce credential-related risks. Password managers can make it easier to generate and store strong credentials without relying on memorization. Multifactor authentication, login monitoring, and timely account recovery procedures provide additional protection when passwords are exposed or suspicious account activity occurs.
5. Denial-of-Service and DDoS Attacks
A denial-of-service attack attempts to make a system, website, or online service unavailable to legitimate users. Distributed denial-of-service attacks, commonly called DDoS attacks, involve traffic or requests originating from multiple sources. These incidents may overwhelm available resources and prevent customers, employees, or other users from accessing essential digital services.
DDoS attacks can target different parts of a digital environment, including network capacity, communication protocols, and application resources. The resulting disruption may cause websites to become slow, applications to stop responding, or services to become temporarily inaccessible. Businesses that depend heavily on online operations can experience substantial interruptions during prolonged incidents.
Reducing DDoS risks often involves specialized traffic management, network monitoring, and services designed to absorb or filter excessive requests. Content delivery networks and suitable rate-limiting controls can provide additional protection in certain situations. Organizations should also maintain response procedures and coordinate with hosting or network providers when service availability becomes threatened.
6. Web Application and API Security Threats
Web applications and application programming interfaces are common targets because they frequently process sensitive information and provide access to important services. Security weaknesses may appear when applications improperly validate inputs, enforce permissions, or handle user sessions. Attackers can attempt to exploit these problems to access restricted information or interfere with application functionality.
Common application security threats include SQL injection, cross-site scripting, broken access control, and insecure authentication practices. API security risks may involve excessive data exposure, inadequate authorization, or weak protection against automated requests. These vulnerabilities can be especially damaging when affected applications connect to customer databases, payment services, or internal business systems.
Secure application development is essential for reducing these risks throughout the software lifecycle. Organizations should perform security testing, validate user inputs, enforce appropriate permissions, and maintain supported software components. Web Application Firewalls, API gateways, and monitoring tools can provide additional protection, but they cannot replace the need to fix weaknesses in application code.
7. Insider Threats and Human Error
Insider threats involve security risks associated with people who have legitimate access to organizational systems or information. These individuals may include employees, contractors, business partners, or other authorized users. Insider incidents can result from deliberate misuse of privileges, accidental disclosure, or compromised accounts that allow outsiders to misuse existing access.
Not every insider threat involves malicious intentions, because ordinary mistakes can also expose sensitive information. Examples include sending confidential files to the wrong recipient, misconfiguring cloud storage, or sharing information through unauthorized applications. These incidents demonstrate why cybersecurity depends on responsible processes and clear communication as well as technical controls.
Organizations can reduce insider risks by limiting access according to job responsibilities and reviewing permissions regularly. Employee training, secure file-sharing procedures, and appropriate activity monitoring can help identify unusual behavior while respecting privacy. Clear reporting channels also encourage staff members to raise potential security concerns before minor errors become serious incidents.
8. Cloud Security and Supply Chain Threats
Cloud computing allows organizations to store information, run applications, and manage resources through remote infrastructure. Although cloud services offer important operational advantages, security problems can arise from incorrect configurations, exposed credentials, and inadequate access controls. Organizations remain responsible for understanding their security obligations under the shared responsibility arrangements of their chosen providers.
Supply chain threats involve weaknesses or compromises affecting external software, service providers, vendors, or other business dependencies. Organizations may be exposed when trusted third-party systems are compromised or insecure components are introduced into their environments. These incidents demonstrate how security problems can extend beyond an organization’s directly managed applications and infrastructure.
Reducing these risks requires careful vendor evaluation, secure cloud configuration, and ongoing monitoring of external dependencies. Organizations should maintain accurate software inventories, review access permissions, and apply available security updates. Strong contractual expectations, incident communication procedures, and regular risk assessments can also improve preparedness for incidents involving third-party services.
9. Impact of Cyber Security Threats on Businesses
Cybersecurity incidents can create financial losses through interrupted operations, recovery expenses, fraud, and compromised business information. Organizations may need to restore systems, investigate suspicious activity, notify affected parties, or obtain specialist assistance. The overall financial impact depends on incident severity, business size, operational dependencies, and the effectiveness of existing security preparations.
Data breaches can also affect customer confidence when personal information or confidential business records become exposed. Customers may question whether their information is adequately protected, particularly when an organization experiences repeated incidents. Depending on applicable laws and circumstances, businesses may also face regulatory investigations, contractual obligations, or legal consequences following certain security failures.
Operational disruption is another major consequence because modern businesses rely on digital systems for communication, sales, and daily administration. An attack affecting essential applications may prevent employees from completing normal responsibilities or customers from accessing services. Developing effective cybersecurity policies and recovery plans helps organizations manage these risks while supporting long-term operational resilience.
10. Best Practices to Prevent Cyber Security Threats
One of the most effective cybersecurity practices is keeping operating systems, applications, and network devices updated. Software updates often address known security weaknesses that attackers may attempt to exploit. Organizations should also remove unsupported software, disable unnecessary services, and review security configurations to reduce the number of potential entry points.
Strong authentication and access management provide another important layer of protection. Unique passwords, phishing-resistant multifactor authentication where available, and carefully assigned user permissions can reduce unauthorized access risks. Sensitive information should also be protected through suitable encryption, secure storage, and access policies that reflect organizational requirements.
Cybersecurity awareness and preparedness are essential because technical controls cannot eliminate every threat. Employees should understand how to recognize suspicious messages, report potential incidents, and handle confidential information responsibly. Regular backups, security monitoring, vulnerability assessments, and documented response procedures help organizations detect problems earlier and recover more effectively when incidents occur.
11. How to Respond to a Cyber Security Incident
An effective incident response process begins with recognizing and reporting unusual activity as soon as possible. Warning signs may include unexpected account access, suspicious security alerts, inaccessible systems, or unexplained changes to important files. Employees should use established reporting channels so qualified personnel can assess the situation and determine whether a security incident has occurred.
Once an incident is confirmed, responsible security teams work to contain the problem and protect unaffected resources. Appropriate actions depend on the nature of the incident and may involve restricting compromised accounts, isolating affected systems, or coordinating with service providers. Maintaining relevant evidence and documenting decisions can support investigation, recovery, and any required reporting obligations.
Recovery involves restoring trusted systems, verifying that identified weaknesses have been addressed, and carefully resuming normal operations. Organizations should also review what happened and identify improvements to security controls, employee procedures, and response plans. Learning from incidents supports stronger preparedness and helps reduce the likelihood of similar security problems occurring again.
Conclusion
Cybersecurity threats represent potential dangers to digital systems, networks, applications, and sensitive information. Common examples include malware, phishing, ransomware, password attacks, DDoS incidents, and application security vulnerabilities. Understanding how these threats affect individuals and organizations is essential for recognizing security risks and developing appropriate protection strategies.
Preventing cyberattacks requires a combination of technical safeguards, responsible user behavior, and effective organizational policies. Regular updates, strong authentication, secure backups, employee awareness, and continuous security monitoring can reduce exposure to many common threats. However, no single cybersecurity solution can guarantee complete protection against every possible attack.
As digital technologies continue to evolve, maintaining good cybersecurity practices remains important for businesses and individuals. Organizations should regularly evaluate their security controls, prepare for potential incidents, and adapt protections as new risks emerge. A proactive and well-informed approach helps protect valuable information, maintain digital services, and build greater confidence in everyday technology use.
Frequently Asked Questions
1. What are cybersecurity threats in simple words?
Cybersecurity threats are potential dangers that can harm computers, networks, online accounts, or digital information. They include activities such as hacking, phishing, malware infections, and attempts to access sensitive data without permission.
2. What are the most common types of cybersecurity threats?
Common cybersecurity threats include malware, ransomware, phishing, credential theft, denial-of-service attacks, and web application vulnerabilities. Insider threats and insecure cloud configurations can also create significant security risks for organizations.
3. What is the difference between a cyber threat and a cyberattack?
A cyber threat is a potential source of harm to digital systems or information. A cyberattack is an actual attempt to compromise security, disrupt services, or gain unauthorized access.
4. How can businesses protect themselves from cybersecurity threats?
Businesses can improve protection through regular software updates, multifactor authentication, employee training, secure backups, and network monitoring. Security assessments and incident response planning also help reduce risks and support recovery.
5. Why are cybersecurity threats increasing?
Growing digital connectivity, expanding cloud services, and increased dependence on online systems create more opportunities for attacks. However, reported threat levels also depend on changes in detection, reporting practices, and attacker behavior.