What Is Microsegmentation and Why Does It Matter?
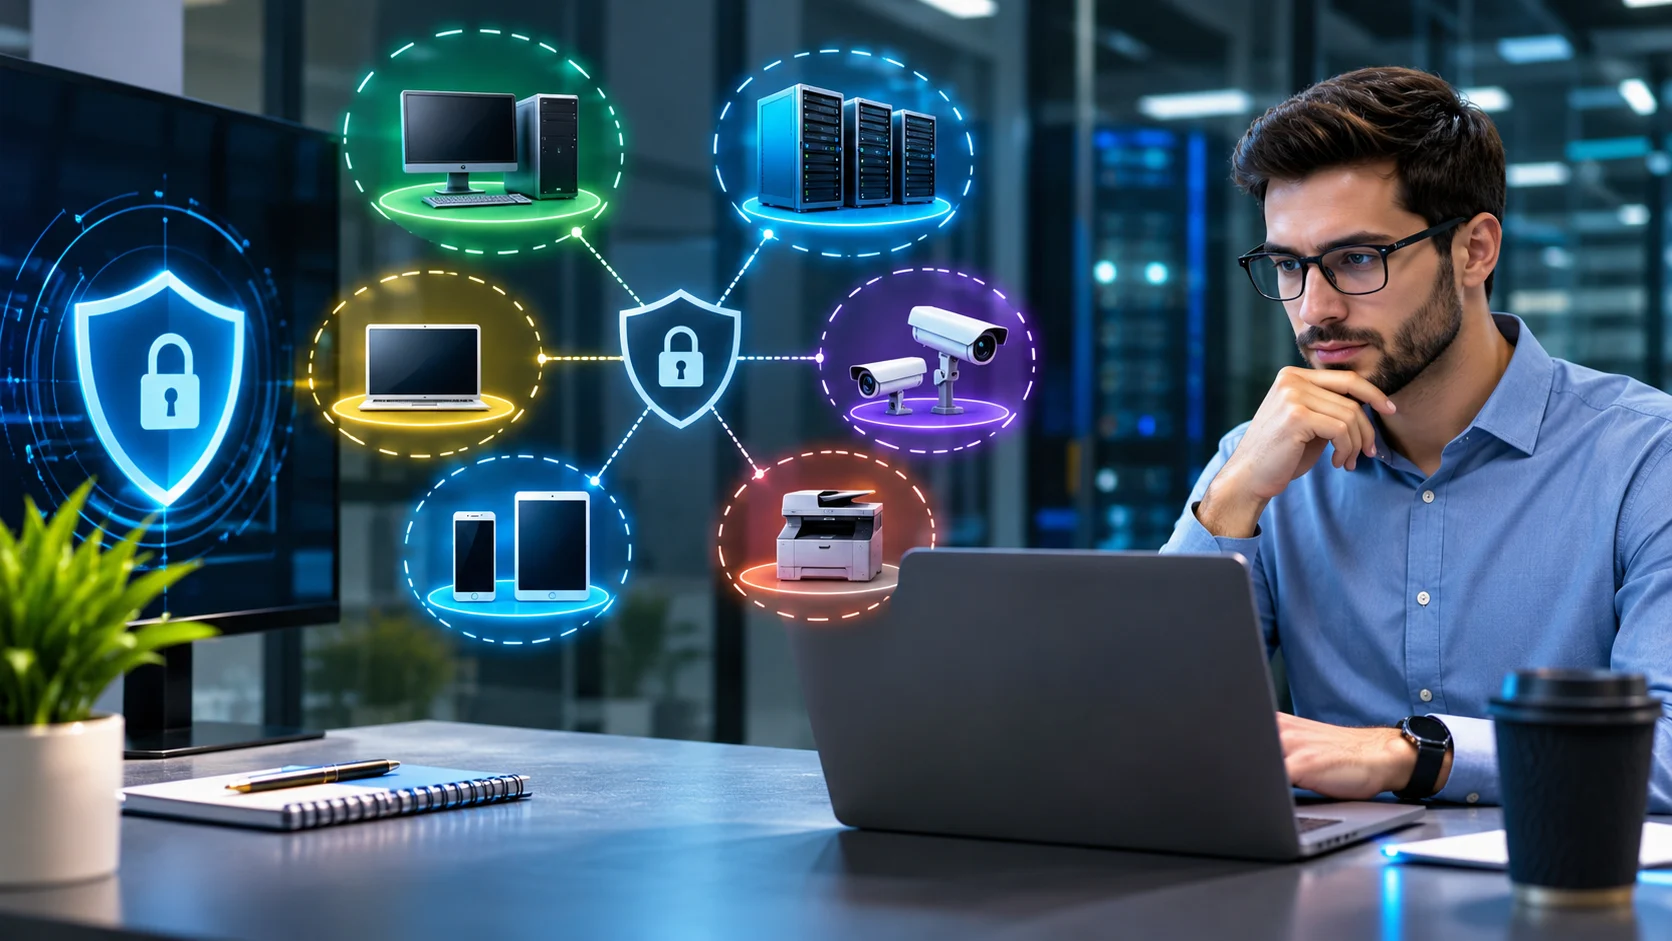
Microsegmentation is a network security approach that divides systems and workloads into small, protected groups. Instead of trusting everything inside a corporate network, it controls which applications, devices, and services can communicate. These controls help businesses contain threats before they spread. They are especially valuable when employees, applications, and data operate across several environments.
Traditional security often focuses on stopping attackers at the network edge, where firewalls inspect incoming and outgoing connections. However, a compromised account or device may already have access to internal resources. Microsegmentation adds security boundaries inside the network itself. Each permitted connection serves a defined business purpose rather than receiving automatic approval.
Why Flat Networks Increase Security Risks
A flat network allows many connected systems to communicate with limited internal restrictions. That arrangement can make initial deployment simple, but it also creates opportunities for unauthorized movement. Once an attacker gains a foothold, poorly protected connections may expose additional servers or sensitive records. A single incident can therefore affect more services than expected.
Remote work, cloud platforms, and third-party applications make these risks harder to manage. Employees may connect through different devices, while applications exchange information across multiple locations. Security teams cannot assume that every internal connection is safe simply because it originates inside the organization. They need visibility into actual communication patterns and controls based on necessity.
Excessive access also increases the consequences of routine mistakes. A misconfigured service, outdated device, or stolen credential may provide a path toward systems that were never meant to interact. Segmenting these connections limits the available paths. The goal is not to eliminate every vulnerability, but to prevent one weakness from becoming an organization-wide problem.
How Microsegmentation Works Behind the Scenes
Microsegmentation begins by identifying workloads and understanding the connections they need to perform their tasks. Security teams observe traffic between servers, applications, databases, and other components. They then develop rules that permit required communication and restrict unnecessary requests. Policies can be based on workload identity, application labels, network attributes, or other trusted signals.
Enforcement may happen through host-based firewalls, virtualization platforms, software agents, or cloud-native security controls. Depending on the technology, decisions can be applied near individual workloads rather than only at central network gateways. This gives teams more precise control over internal traffic. It also allows protections to follow applications as infrastructure changes.
For example, a web application may need to contact an application service, which then accesses a database. Microsegmentation can allow those specific paths while rejecting unrelated connections to the database. Teams usually test policies before enforcing them, because missing an essential dependency can interrupt service. Accurate traffic discovery is therefore a critical part of deployment.
Microsegmentation vs. Traditional Network Segmentation
Traditional network segmentation separates a network into larger zones, often using virtual LANs, subnets, and firewalls. Businesses might create different zones for guests, employees, and production servers. These boundaries improve security, but each zone can still contain many systems with broad permissions. Attackers may move between workloads that share the same trusted zone.
Microsegmentation creates smaller boundaries around applications, workloads, or even individual services. Its rules can control traffic between two machines located on the same subnet. This is particularly useful when sensitive workloads share infrastructure with ordinary business systems. Finer controls reduce reliance on location as proof that communication should be allowed.
Neither approach needs to replace the other completely. Network segmentation establishes useful high-level boundaries, while microsegmentation provides detailed rules within and across those boundaries. Organizations often combine both approaches with identity management and endpoint protection. The right design depends on application dependencies, operational complexity, and the risks attached to critical information.
Understanding East-West Traffic and Lateral Movement
North-south traffic generally moves into or out of a network, while east-west traffic travels between internal systems and workloads. Many traditional security tools concentrate on the external boundary. However, modern applications constantly exchange internal requests, including database queries and service-to-service calls. Those legitimate connections can also become routes for attackers if permissions are too broad.
Lateral movement describes an attacker attempting to reach additional systems after gaining initial access. They may look for accessible services, weak permissions, or credentials that open new pathways. Microsegmentation limits these possibilities by restricting communication between workloads that have no reason to interact. A compromised device does not automatically gain a direct path to every reachable server.
This protection depends on understanding normal application behavior rather than blocking traffic indiscriminately. Security teams need to know which connections support daily operations and which ones are unnecessary. Traffic logs and dependency maps help reveal those relationships. With carefully tested policies, organizations can reduce lateral movement while keeping essential business processes available.
Key Benefits of Microsegmentation for Businesses
The most important benefit is stronger containment when a security incident occurs. By limiting unnecessary connections, microsegmentation can reduce the number of systems an attacker can reach. It may also help protect sensitive databases and business-critical applications from unrelated workloads. Containment is not guaranteed, but smaller access boundaries can make an intrusion harder to expand.
Another benefit is improved visibility into application communication. Before creating policies, teams often discover connections they did not know existed. That information helps identify outdated services, excessive access, and unexpected dependencies. Better visibility supports more informed decisions about firewall rules, access reviews, infrastructure changes, and security priorities across different business departments.
Microsegmentation can also support regulatory and internal security requirements by isolating environments that handle sensitive information. For example, a business might limit which services can reach payment-related systems. Clear policies and logs may assist audits by showing how access is controlled. Actual compliance still depends on the relevant standards and the organization’s wider security practices.
Common Approaches to Microsegmentation
Host-based microsegmentation applies controls directly to a server or workload, often through an agent or operating system firewall. This approach can be useful across physical, virtual, and some cloud environments. It can protect workloads even when they share a network segment. However, deployment requires compatibility checks, reliable management, and appropriate attention to system performance.
Network-based approaches use infrastructure controls, such as switches, firewalls, and software-defined networking technologies. These solutions can suit organizations that already manage traffic through centralized networking tools. Cloud-native controls may use security groups, network policies, or provider-specific features. Their exact capabilities vary, so teams should verify how precisely each option can enforce application-level rules.
Identity-aware or application-centric approaches organize permissions around workload roles, labels, and verified identities instead of fixed addresses alone. This can make policies easier to maintain when applications move or scale. Many organizations use a combination of techniques rather than one universal solution. The best choice balances security coverage, operational effort, existing tools, and infrastructure limitations.
Microsegmentation in Cloud and Hybrid Environments
Cloud applications frequently use dynamic resources that start, stop, or change addresses automatically. Static rules based only on IP addresses may become difficult to manage in such environments. Microsegmentation helps by attaching policies to meaningful workload characteristics wherever supported. Teams can protect communication among virtual machines, containers, application services, and databases without depending entirely on fixed locations.
Hybrid networks add another layer of complexity because workloads operate both on-premises and in cloud platforms. A single application might rely on a local identity service and a cloud-hosted database. Security teams must understand those dependencies before limiting access. Consistent policy design matters, even when different platforms require different technical methods for enforcement.
Containerized applications create additional challenges because services may scale quickly and communicate through changing endpoints. Orchestration systems can provide network policies that limit permitted connections between workloads. However, policies must account for service discovery, monitoring, and required platform traffic. Testing changes in a staging environment helps avoid disruptions to applications with many moving parts.
How Microsegmentation Supports Zero Trust Security
Zero trust security is based on the principle that access should not be granted merely because a request comes from a trusted network location. Every connection should be evaluated using appropriate identity, device, application, and contextual information. Microsegmentation supports that goal by reducing broad internal access. It turns the principle of least privilege into enforceable communication boundaries.
In a zero trust architecture, authentication and authorization remain essential even when network access is restricted. Microsegmentation does not verify every user identity or replace multifactor authentication. Instead, it adds a separate layer that controls which systems can exchange traffic. Combining these protections makes it harder for a stolen credential to unlock unrelated infrastructure.
Consider a support application that needs access to a customer database through a specific service. Zero trust controls can verify the requesting user and application, while microsegmentation limits reachable network paths. Each layer answers a different security question. Together, they help organizations protect valuable resources without assuming that everything inside the perimeter is trustworthy.
Practical Microsegmentation Use Cases
Healthcare organizations can use microsegmentation to reduce unnecessary communication between clinical applications, administrative systems, and connected medical technology. These environments often include devices with different support and update requirements. Restricting avoidable connections can reduce exposure while protecting essential services. Because availability is critical, teams must involve clinical and technical stakeholders when testing security changes.
Financial institutions and retailers may separate payment-processing workloads from general business applications. A customer-facing website, for instance, should not automatically gain broad access to internal finance systems. Narrow communication rules can help protect valuable records and limit incident impact. Organizations should still use encryption, strong authentication, monitoring, and other safeguards for sensitive transactions.
Microsegmentation is equally relevant to smaller companies with a few important servers and cloud applications. A business could isolate backups, management interfaces, and core databases from everyday employee devices. Starting with these critical assets creates a manageable first project. The strategy can expand gradually as the team gains visibility and learns which rules work reliably.
How to Implement Microsegmentation Step by Step
Start by identifying business-critical applications, sensitive data, and the systems that support them. Create an inventory of workloads and map their required communication patterns. Include application owners because network logs alone may not explain every dependency. This preparation helps teams define practical security goals and avoid creating rules that interfere with essential operations.
Next, choose a limited pilot environment and establish a baseline of normal traffic. Draft least-privilege policies that allow necessary connections and deny avoidable ones. Where available, use monitoring or simulation modes before turning on enforcement. Review unexpected traffic with application owners, then adjust rules carefully instead of assuming that every unfamiliar connection is malicious.
After the pilot succeeds, expand protection in phases based on business risk and operational readiness. Document policy ownership, approval steps, rollback procedures, and exception handling. Track blocked connections, application health, and incident findings so the team can evaluate results. A staged rollout is generally safer and easier to troubleshoot than changing the entire network at once.
Challenges and Best Practices for Long-Term Success
The biggest challenge is often understanding complex application dependencies. Older systems may use undocumented ports, shared services, or unpredictable communication patterns. Restrictive rules introduced too quickly can interrupt workflows and create resistance to the project. Begin with discovery, involve system owners, and validate policies through controlled testing before enforcing them in production environments.
Policy sprawl is another concern as applications change and teams add exceptions. Without clear ownership, temporary permissions may remain active long after they are needed. Use consistent naming, documented business reasons, and scheduled access reviews to keep rules understandable. Automation can help apply approved changes, but every automated process still needs safeguards and accountability.
Finally, measure whether microsegmentation actually reduces risk instead of counting policies alone. Useful indicators include unnecessary communication paths removed, critical workloads covered, and unexpected access attempts investigated. Review the design after major application changes, migrations, or security incidents. Microsegmentation works best as an ongoing security practice, not a one-time configuration exercise.
Conclusion
Microsegmentation helps limit network risks by controlling how applications, devices, and workloads communicate. Instead of assuming internal traffic is trustworthy, it creates smaller access boundaries around important systems. Those boundaries can restrict lateral movement and reduce the impact of compromised accounts or devices. This makes the approach valuable in traditional, cloud, and hybrid environments.
Successful deployment depends on careful planning rather than simply installing another security product. Teams need clear asset inventories, reliable traffic visibility, and policies built around real application requirements. Starting with a focused pilot makes it easier to find missing dependencies and correct mistakes. Gradual expansion can improve protection without creating unnecessary disruption.
Microsegmentation is most effective alongside identity security, endpoint protection, monitoring, and incident response. Each safeguard addresses a different part of the threat landscape. Together, they support more resilient operations and better control over sensitive resources. Organizations that maintain and review their policies are better positioned to adapt as networks and business needs evolve.
FAQs
What is microsegmentation in simple terms?
Microsegmentation divides a network into small protected areas and controls communication between them. It helps prevent a problem in one application or device from spreading easily to others.
Is microsegmentation the same as a firewall?
No. Firewalls are one technology used to enforce microsegmentation policies. Microsegmentation is the broader strategy of applying detailed access controls around individual workloads, applications, and services.
Does microsegmentation prevent every cyberattack?
No security method prevents every attack. Microsegmentation mainly reduces unnecessary network access and limits potential movement between systems, so it works best when combined with other security controls.
Can small businesses use microsegmentation?
Yes. Small businesses can begin by isolating critical applications, backup systems, or sensitive databases. A limited rollout can provide useful protection without requiring a large-scale network redesign.
How long does microsegmentation take to implement?
The timeline depends on network size, application complexity, and available tools. A small pilot may be quicker than an organization-wide deployment, which requires discovery, testing, and ongoing adjustments.