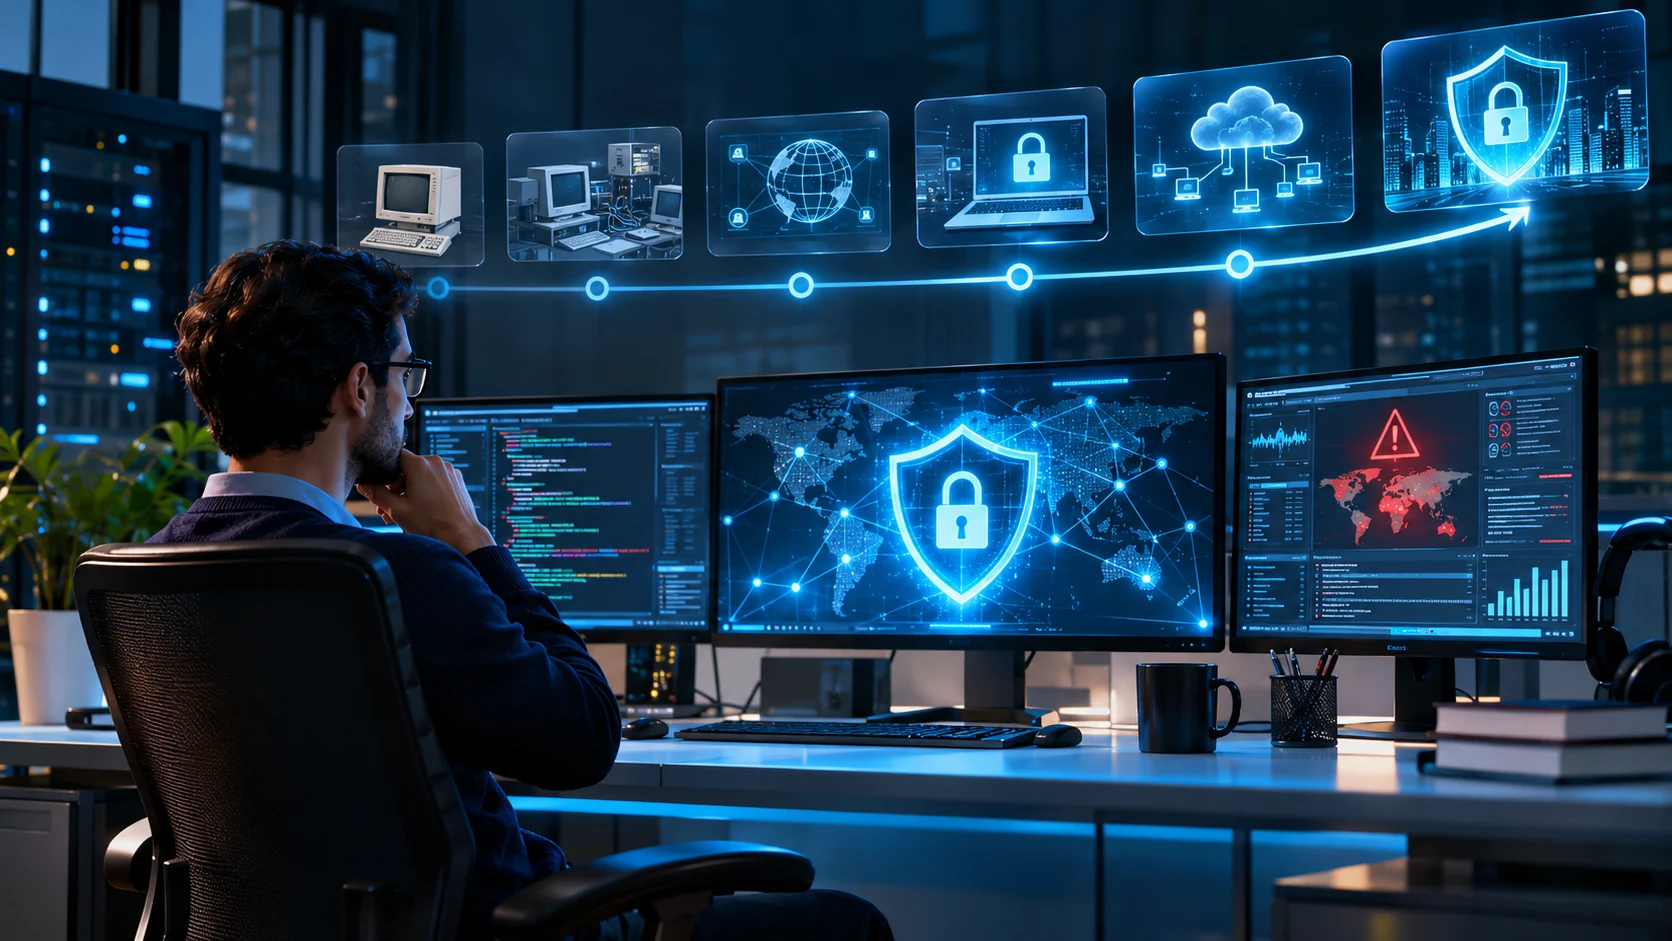
Cybersecurity is one of the most important areas of modern technology, protecting individuals, businesses, and governments from digital threats. Today, organizations invest heavily in protecting sensitive information, computer networks, and online services. However, cybersecurity did not become popular overnight. Its development began decades before the internet became part of everyday life, evolving alongside computers, communication networks, and increasingly sophisticated cyber threats.
Many people wonder when cybersecurity became popular and what events made digital security a global priority. Although computer security concepts appeared in the 1960s and 1970s, cybersecurity gained wider attention during the 1990s as internet adoption increased. Its importance expanded further during the 2000s and 2010s when major data breaches, ransomware attacks, and online fraud became serious concerns.
When Did Cybersecurity Become Popular?
Cybersecurity began gaining broader recognition during the 1990s when the internet became increasingly available to businesses and households. Before this period, computer security mainly concerned researchers, government agencies, and organizations operating large computing systems. As internet connectivity expanded, more people started exchanging information online. This increased the need for secure networks, reliable authentication, and protection against malicious software.
The early 2000s marked another important period in cybersecurity awareness. Businesses increasingly depended on websites, email communication, and digital financial transactions. Computer viruses, internet worms, and online fraud demonstrated how security problems could disrupt everyday operations. Organizations responded by adopting antivirus software, firewalls, and specialized information security practices to protect their growing digital infrastructure.
Cybersecurity became a major global business priority during the 2010s. High-profile data breaches, sophisticated attacks, and ransomware incidents showed that digital threats could affect millions of people. Governments introduced stronger security requirements, while companies expanded their cybersecurity teams. By this period, cybersecurity had developed into a widely recognized profession and an essential part of modern business management.
The Early Origins of Cybersecurity in the 1960s
The foundations of cybersecurity can be traced to the 1960s when computers were primarily used by universities, government organizations, and research institutions. These systems were expensive and often shared by multiple users. As computing environments became more complex, administrators recognized the importance of controlling access to sensitive information. Early security efforts focused on permissions, user identification, and protecting computer resources.
During this period, researchers explored how different users could safely operate within shared computing systems. Security concerns included unauthorized access, information confidentiality, and the reliability of computer operations. Although modern cyberattacks were not yet widespread, these problems introduced important principles of computer security. Many concepts developed during this era later influenced authentication systems and access control technologies.
Computer networks were also beginning to develop, creating new possibilities for communication between machines. ARPANET, an early network that helped shape the internet, began operating in 1969. Connecting computers introduced questions about how information could move securely between systems. These early developments established the technical foundation for the network security practices that became increasingly important in later decades.
How Cybersecurity Developed During the 1970s
The 1970s represented an important stage in the development of computer and network security. Researchers began examining how programs could move between connected systems and what risks they might create. One notable experiment involved Creeper, an early self-replicating program associated with ARPANET-connected computers. Although it was experimental rather than a modern malicious virus, it demonstrated new possibilities for software behavior.
Another important development involved Reaper, a program designed to locate and remove Creeper. This experiment is often discussed as an early example of software designed to counter another program. It reflected an emerging understanding that computer systems might require automated protection. These developments were limited compared with modern security software, but they contributed to the history of malware detection.
The decade also brought greater attention to formal computer security research. Governments and academic institutions studied access control, system vulnerabilities, and methods for protecting sensitive information. As organizations began relying more heavily on computing systems, security became an important technical concern. The principles established during this period helped support later advances in commercial cybersecurity tools and professional practices.
Why Computer Viruses Increased Security Awareness in the 1980s
The 1980s introduced new cybersecurity challenges as personal computers became more accessible. Businesses, schools, and households increasingly used computers for everyday tasks. This growth created opportunities for malicious or disruptive software to spread beyond specialized research environments. Computer viruses attracted attention because they could interfere with normal operations and damage or modify stored information.
One important example was Brain, a computer virus discovered in 1986 that affected IBM PC-compatible systems. It spread through infected floppy disks, reflecting how software and information were commonly exchanged before widespread internet access. The virus demonstrated that personal computers could face security threats even without modern online connections. Such incidents increased interest in detecting and preventing infections.
The growing threat encouraged the development of commercial antivirus technologies. Software companies began creating tools to identify suspicious programs and remove known viruses. Organizations also introduced safer procedures for sharing files and using removable storage devices. Although cybersecurity was still a developing field, the 1980s helped establish computer protection as a practical concern for ordinary users.
The Morris Worm and the Cybersecurity Turning Point of 1988
The Morris worm became one of the most significant events in early internet security history. Released in November 1988, it spread across connected Unix computer systems and disrupted many machines. The worm exploited technical weaknesses and multiplied in ways that consumed system resources. Its impact demonstrated how a single program could create widespread problems across interconnected networks.
The incident attracted attention because it revealed vulnerabilities in the growing internet infrastructure. Researchers, universities, and organizations experienced disruptions that highlighted weaknesses in network protection. The worm also showed how quickly security problems could spread between connected computers. This experience encouraged greater interest in vulnerability management, incident response, and communication between technical teams.
Following the incident, the Computer Emergency Response Team Coordination Center, commonly known as CERT/CC, was established. Its creation marked an important development in organized cybersecurity response. Security professionals increasingly recognized the importance of sharing information about vulnerabilities and coordinating responses to incidents. The Morris worm therefore became a major historical milestone in the development of modern cybersecurity practices.
How the Internet Made Cybersecurity Popular in the 1990s
The 1990s played a central role in making cybersecurity more relevant to everyday computer users. Internet access expanded, and the World Wide Web introduced new opportunities for communication, research, and business. Companies began developing websites and connecting internal systems to external networks. These changes increased the number of potential security weaknesses that attackers could attempt to exploit.
As online services developed, organizations needed stronger methods for protecting information transmitted across networks. Firewalls became important tools for controlling network traffic, while encryption technologies supported safer communication. Web security also gained attention as businesses started handling customer information online. These developments helped establish cybersecurity as a growing commercial industry rather than only a specialized research field.
Computer viruses and unauthorized network access remained important concerns throughout the decade. Security professionals developed improved antivirus tools, intrusion detection systems, and network monitoring techniques. Businesses increasingly understood that security problems could interrupt operations and damage customer trust. By the late 1990s, cybersecurity had become a recognizable part of managing connected computer systems and online services.
Why Cybersecurity Became Essential in the 2000s
The 2000s brought rapid growth in internet-based business activities and digital communication. Online banking, electronic commerce, and email became increasingly important for individuals and organizations. As more sensitive information moved through digital systems, security became essential for protecting financial transactions and personal records. Businesses needed stronger defenses to reduce the risks associated with expanding online services.
Several major malware incidents demonstrated the scale of emerging threats. The ILOVEYOU outbreak in 2000 spread through email attachments and affected computer systems worldwide. Other incidents, including Code Red and SQL Slammer, disrupted network services during the early decade. These events showed that malicious software could spread rapidly and create serious operational and financial consequences.
Organizations responded by investing more in network protection, employee awareness, and security management. Governments also developed laws and regulatory requirements addressing digital information and privacy. Security teams became responsible for monitoring systems, investigating incidents, and improving defensive controls. During this period, cybersecurity evolved from a technical concern into a broader business responsibility involving management and organizational planning.
How Major Cyberattacks Changed Cybersecurity in the 2010s
The 2010s transformed cybersecurity into a major global priority as increasingly serious digital attacks affected large organizations. High-profile incidents exposed weaknesses in corporate networks, payment systems, and customer databases. The consequences extended beyond technical disruption and included financial losses, reputational damage, and regulatory investigations. These incidents encouraged business leaders to consider cybersecurity an important organizational risk.
Major breaches involving companies such as Target and Equifax demonstrated the possible impact of stolen customer information. Millions of individuals were affected by incidents involving payment details or sensitive personal records. These events attracted extensive public attention and raised questions about how organizations protected their systems. Consumers became more aware of privacy risks and the importance of securing personal information.
Governments and businesses increased investment in cybersecurity strategies during this period. Security frameworks, incident response planning, and professional training became more widely adopted. Organizations also paid greater attention to third-party risks, employee access, and continuous monitoring. By the end of the decade, cybersecurity was firmly established as a critical business function across many industries.
The Rise of Ransomware and Advanced Cyber Threats
Ransomware became one of the most widely discussed cybersecurity threats during the 2010s. This type of malicious software can encrypt files or disrupt access to computer systems while attackers demand payment. Businesses, hospitals, government agencies, and individual users experienced ransomware incidents. These attacks demonstrated how cybercrime could interfere with essential operations and create serious financial pressure.
The WannaCry ransomware outbreak in May 2017 became a particularly important event in cybersecurity history. It affected organizations across numerous countries and caused widespread disruption. The incident exposed the dangers of unpatched software and inadequate security preparation. It also encouraged organizations to improve system updates, backups, vulnerability management, and emergency response procedures.
Cyber threats also became more sophisticated as attackers developed new techniques for targeting organizations. Phishing, credential theft, software supply chain compromises, and attacks against cloud environments created additional challenges. Defending against these risks required more than traditional antivirus software. Organizations increasingly adopted layered security controls, identity protection, monitoring systems, and employee education to reduce their exposure.
Why the COVID-19 Pandemic Increased Cybersecurity Demand
The COVID-19 pandemic created major changes in how people worked, studied, and communicated. Beginning in 2020, many organizations rapidly expanded remote working arrangements and digital services. Employees accessed business systems from home networks, personal devices, and cloud-based platforms. These changes created additional security challenges because organizations needed to protect information across more distributed environments.
Cybercriminals also used pandemic-related concerns in phishing messages and online scams. Attackers attempted to exploit confusion, urgency, and increased dependence on digital communication. Organizations needed to strengthen account security, remote access protections, and employee awareness. The widespread use of video meetings and collaboration platforms also increased attention to secure configuration and access management.
The pandemic reinforced the importance of cybersecurity in maintaining business continuity. Organizations recognized that remote productivity depended on reliable digital infrastructure and appropriate security controls. Demand increased for professionals who could manage cloud environments, secure networks, and respond to emerging threats. This period helped establish cybersecurity as an essential requirement for flexible and increasingly digital workplaces.
Cybersecurity in the 2020s: AI, Cloud Security, and Digital Privacy
During the 2020s, cybersecurity has continued evolving as organizations adopt cloud computing, connected devices, and artificial intelligence. Businesses increasingly depend on digital platforms to store information and deliver services. This creates opportunities for efficiency but also introduces complex security responsibilities. Protecting identities, applications, and sensitive data has become increasingly important across modern technology environments.
Artificial intelligence has introduced additional opportunities and challenges for cybersecurity professionals. Security teams can use machine learning techniques to identify unusual activity and support threat analysis. At the same time, attackers may use AI tools to create convincing phishing messages or automate certain malicious activities. Responsible organizations must evaluate both the benefits and risks of these technologies.
Digital privacy has also become a major concern for businesses and consumers. Organizations face growing expectations around responsible data collection, secure storage, and appropriate access controls. Cloud security, identity management, and zero-trust approaches have gained attention as important defensive strategies. These developments reflect how cybersecurity now supports business operations, consumer confidence, and the reliability of digital services.
Why Cybersecurity Became a Popular Career Choice
Cybersecurity became an increasingly attractive career field as organizations recognized the need for skilled security professionals. Businesses require specialists who can protect networks, investigate incidents, and evaluate system vulnerabilities. Government agencies and healthcare organizations also depend on qualified security teams. This broad demand has created several career paths for people interested in technology and digital protection.
Common cybersecurity roles include security analyst, penetration tester, security engineer, incident responder, and security consultant. Each position involves different responsibilities and technical requirements. Some professionals focus on monitoring suspicious activity, while others test security weaknesses or develop defensive systems. Understanding these specializations helps beginners identify which skills and learning paths best match their interests.
People entering cybersecurity often begin by learning computer networking, operating systems, and basic security principles. Practical experience, relevant training, and recognized certifications may strengthen their qualifications. However, cybersecurity requires continuous learning because technology and threats change regularly. Career opportunities can be rewarding, but success depends on developing dependable technical skills and understanding real-world security responsibilities.
What Does the Future of Cybersecurity Look Like?
The future of cybersecurity will be influenced by continued growth in artificial intelligence, cloud services, and connected technology. Organizations will need to protect increasingly complex systems while responding to evolving digital threats. As more activities depend on online platforms, cybersecurity will remain important for maintaining reliable services. Effective protection will require ongoing investment in people, processes, and technology.
Security professionals are likely to place greater emphasis on automation, identity protection, and proactive risk management. Automated systems can help analyze large amounts of security information, but human judgment will remain important for complex decisions. Organizations will also need to assess risks associated with third-party technology providers. Strong communication between security teams and business leaders will support better decisions.
Cybersecurity awareness will continue extending beyond technical departments into everyday digital activities. Individuals will benefit from understanding secure passwords, multifactor authentication, and common online scams. Businesses will need to build security into their operations rather than treating it as an afterthought. The industry’s future will depend on adapting to new technology while maintaining practical and reliable protection.
Conclusion
Cybersecurity began developing during the 1960s and 1970s, but it gained broader recognition during the 1990s as internet access expanded. The growth of online services created new security risks that affected businesses and individual users. Major malware incidents and network vulnerabilities encouraged organizations to invest in stronger computer protection and more structured security practices.
The 2000s and 2010s transformed cybersecurity into a major global industry. Increasingly serious cyberattacks, large data breaches, and ransomware incidents highlighted the importance of protecting sensitive information. Governments, businesses, and consumers became more aware of digital risks. These developments helped make cybersecurity an essential part of modern technology, business operations, and information management.
Today, cybersecurity continues evolving alongside artificial intelligence, cloud computing, and digital communication. Its history demonstrates how technological progress creates both opportunities and new security challenges. Understanding when cybersecurity became popular provides valuable context for its continued importance. As digital systems become more connected, protecting them will remain a central responsibility for organizations and individuals.
Frequently Asked Questions
When Did Cybersecurity First Become Popular?
Cybersecurity gained wider attention during the 1990s as internet use increased. However, its foundations developed during the 1960s and 1970s, when researchers began studying computer access controls, network security, and software behavior.
Who Is Considered the Father of Cybersecurity?
There is no universally recognized father of cybersecurity because the field developed through contributions from many researchers. Bob Thomas and Ray Tomlinson are frequently mentioned for their roles in early self-replicating software and its removal.
What Was the First Major Cybersecurity Incident?
The Morris worm outbreak in 1988 is widely recognized as an important early internet security incident. It disrupted numerous connected computers and encouraged the development of more organized cybersecurity incident response practices.
Why Did Cybersecurity Become So Important?
Cybersecurity became essential as businesses and individuals increasingly relied on internet-connected systems. Data breaches, malware, online fraud, and ransomware demonstrated the potential consequences of inadequate protection for sensitive information and critical services.
Is Cybersecurity Still a Growing Field in 2026?
Cybersecurity remains an important field as organizations address cloud security, artificial intelligence risks, ransomware, and digital privacy. Career opportunities and demand vary by location and specialization, but protecting connected systems continues to require skilled professionals.