Cybersecurity threats have become a major concern for businesses of every size. Organizations store sensitive customer information, financial records, and confidential business data across digital systems. Protecting these assets requires more than installing antivirus software or creating strong passwords. Businesses also need clear security strategies, regular risk assessments, and professional guidance to manage potential threats.
Cybersecurity consulting helps organizations identify security weaknesses, improve their defenses, and protect important digital assets. Consultants evaluate existing security systems, recommend practical improvements, and support businesses in managing cyber risks. Their expertise helps organizations make informed decisions about information security and long-term protection.
Understanding cybersecurity consulting is useful for business owners, IT professionals, and anyone interested in digital security. This guide explains how cybersecurity consulting works, the services consultants provide, and why organizations invest in professional cybersecurity support.
What Is Cybersecurity Consulting?
Cybersecurity consulting is a professional service that helps organizations assess, improve, and manage their information security practices. Cybersecurity consultants examine digital infrastructure, identify vulnerabilities, and recommend solutions that reduce potential security risks. Their work focuses on protecting sensitive information, business applications, networks, and computer systems from unauthorized access and cyberattacks.
Unlike general IT support, cybersecurity consulting concentrates specifically on identifying and managing digital security threats. Consultants evaluate how effectively an organization protects its systems against malware, phishing, ransomware, data breaches, and other cybersecurity risks. They also help businesses establish security policies and strengthen existing protection measures according to their operational needs.
Cybersecurity consulting services may involve one-time assessments, ongoing security advisory support, or assistance with specific security projects. Some organizations hire independent security consultants, while others work with specialized cybersecurity consulting firms. The main goal is to create a practical security strategy that supports business operations while reducing exposure to potential cyber threats.
How Does Cybersecurity Consulting Work?
Cybersecurity consulting usually begins with understanding an organization’s technology environment, business objectives, and existing security challenges. Consultants review infrastructure, applications, security policies, and data protection requirements to identify potential weaknesses. This initial assessment helps establish which security risks require attention and how improvements should align with the organization’s priorities.
After identifying risks, consultants develop recommendations based on the organization’s security needs and available resources. These recommendations may include stronger access controls, updated security configurations, employee awareness programs, or improved incident response procedures. Consultants generally prioritize improvements according to their potential impact, implementation difficulty, and importance to business operations.
The consulting process often continues with implementation support, security testing, and performance reviews. Consultants may work alongside internal IT teams to introduce recommended controls and verify whether they function correctly. Regular follow-up assessments help organizations maintain stronger security practices as technology changes, business operations expand, and new cybersecurity threats emerge.
What Does a Cybersecurity Consultant Do?
A cybersecurity consultant analyzes an organization’s security posture and identifies weaknesses that could expose sensitive information or essential systems. This work may involve examining network configurations, reviewing access permissions, and assessing existing cybersecurity controls. Consultants use their technical knowledge and security experience to recommend improvements that address realistic business risks.
Consultants also help organizations develop security policies, establish incident response plans, and prepare for security audits. Depending on their specialization, they may assess cloud environments, conduct authorized penetration testing, or evaluate third-party security risks. Their responsibilities vary according to the client’s industry, technology infrastructure, and specific security requirements.
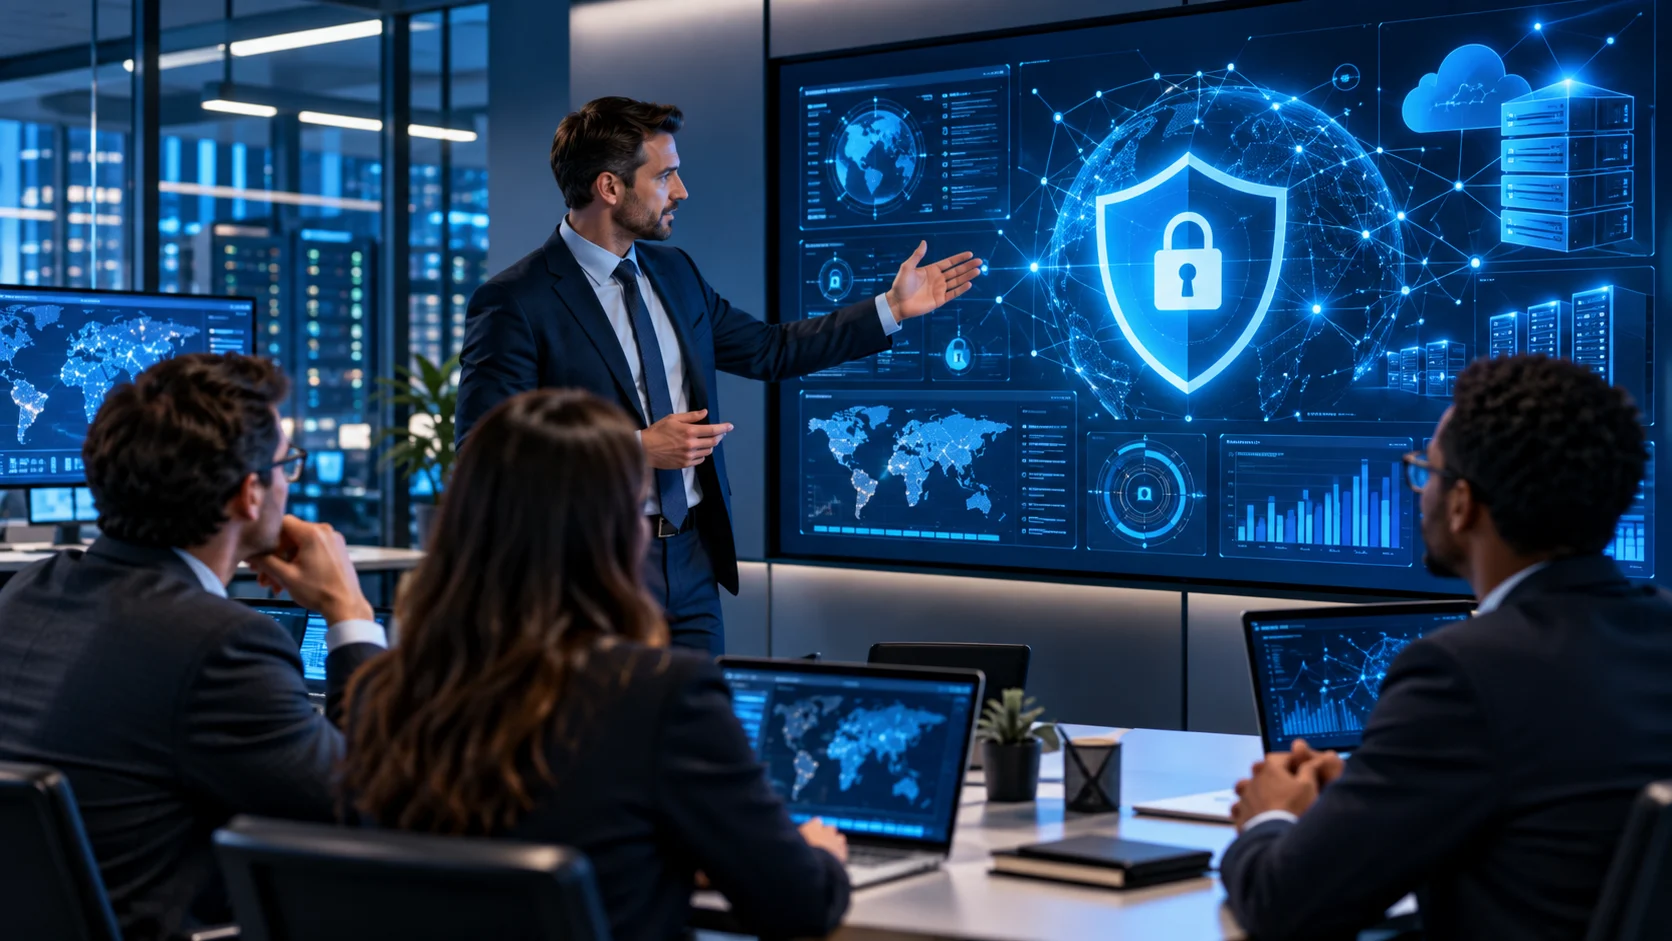
Communication is another important part of a cybersecurity consultant’s role because security recommendations must be understandable and actionable. Consultants often prepare reports explaining identified risks, potential business consequences, and recommended solutions. They may also present findings to business leaders and technical teams, helping stakeholders understand cybersecurity priorities and make informed investment decisions.
Key Types of Cybersecurity Consulting Services
Cybersecurity consulting includes several specialized services designed to address different security challenges. Organizations may need assistance protecting networks, securing cloud applications, managing compliance requirements, or responding to security incidents. Understanding the major consulting services helps businesses identify which type of expertise best matches their security needs and operational priorities.
Common services include cybersecurity risk assessments, vulnerability assessments, penetration testing, network security consulting, cloud security consulting, and security architecture reviews. Consultants may also provide identity and access management guidance, compliance assessments, and incident response planning. These services help organizations identify weaknesses and establish security controls appropriate for their infrastructure and risk exposure.
Some cybersecurity consulting firms offer comprehensive security programs, while others specialize in particular technologies or industries. A small business might require a basic security assessment and employee training, whereas a larger organization may need specialized cloud security and governance support. Choosing suitable services depends on existing vulnerabilities, business objectives, and available resources.
Why Is Cybersecurity Consulting Important for Businesses?
Cybersecurity consulting is important because organizations face security risks that can interrupt operations, expose confidential information, and damage customer trust. Modern businesses depend on interconnected applications, cloud platforms, and digital communication systems. Without appropriate security practices, weaknesses in these technologies can create opportunities for unauthorized access and other security incidents.
Professional cybersecurity consultants provide an independent perspective on existing security controls and potential vulnerabilities. Internal teams may overlook certain risks because they are familiar with established systems and procedures. External assessments can help identify overlooked weaknesses, evaluate current protection methods, and recommend improvements based on recognized security principles.
Cybersecurity consulting also helps businesses take a more proactive approach to managing digital risks. Instead of addressing security problems only after an incident occurs, organizations can identify vulnerabilities earlier and improve their defenses. This approach supports business continuity, protects sensitive information, and encourages stronger security awareness throughout the organization.
Benefits of Hiring a Cybersecurity Consulting Firm
One major benefit of cybersecurity consulting is access to specialized security expertise without necessarily maintaining a large internal security department. Consulting firms employ professionals with experience in different technologies, industries, and cybersecurity challenges. Their knowledge can help businesses assess complex risks and implement security improvements more effectively than relying on limited internal resources.
Another advantage is the ability to prioritize cybersecurity investments according to actual business risks. Consultants evaluate existing weaknesses and recommend practical improvements rather than assuming every organization requires identical security solutions. This risk-based approach can help companies allocate budgets more effectively while strengthening protection for important systems and sensitive information.
Cybersecurity consultants can also support regulatory compliance, employee awareness, and incident preparedness. Their recommendations may help organizations establish clearer responsibilities, improve documentation, and develop more consistent security procedures. Although consulting cannot eliminate every cyber threat, it can help businesses manage risks more systematically and respond more effectively when security problems occur.
Cybersecurity Risk Assessment and Vulnerability Management
A cybersecurity risk assessment identifies potential threats, security weaknesses, and their possible effects on an organization. Consultants examine valuable assets, evaluate existing security controls, and estimate the likelihood and impact of different risks. This process helps businesses understand which vulnerabilities could cause the greatest disruption and where protective investments should be prioritized.
Vulnerability management focuses on identifying, evaluating, prioritizing, and addressing weaknesses in software, networks, and systems. Consultants may review scanning results, assess configuration issues, and recommend appropriate updates or security controls. Not every detected vulnerability presents the same level of danger, so effective prioritization considers exploitability, business exposure, and the importance of affected systems.
Risk assessments and vulnerability management work together to support stronger cybersecurity planning. Assessments provide a broader understanding of organizational security risks, while vulnerability management addresses specific technical weaknesses. When performed regularly, these activities help businesses monitor changes, measure security improvements, and reduce the likelihood of preventable cybersecurity incidents.
Cybersecurity Consulting for Cloud and Network Security
Cloud security consulting helps organizations protect applications, data, and services hosted on cloud computing platforms. Consultants review identity permissions, storage configurations, encryption practices, and other controls that influence cloud security. Their recommendations aim to reduce risks such as unauthorized access, accidental data exposure, and insecure configurations across cloud environments.
Network security consulting focuses on protecting the systems and connections used to exchange information within an organization. Consultants may evaluate firewalls, network segmentation, remote access configurations, and monitoring capabilities. They help businesses identify unnecessary exposure and recommend security improvements that support reliable communication while limiting opportunities for unauthorized network activity.
Cloud and network security are closely connected because many organizations operate hybrid environments containing both local infrastructure and cloud services. Protecting these environments requires consistent security policies, appropriate access controls, and clear visibility into important systems. Consultants help organizations coordinate security measures across their infrastructure while considering operational requirements and potential risks.
Cybersecurity Compliance and Data Protection Consulting
Cybersecurity compliance consulting helps organizations understand and address applicable security laws, regulations, and contractual requirements. Depending on the industry and location, businesses may need to consider frameworks or requirements such as GDPR, HIPAA, or PCI DSS. Consultants help identify relevant obligations and assess whether existing policies and security controls adequately support compliance.
Data protection consulting concentrates on safeguarding sensitive personal, financial, and business information throughout its lifecycle. Consultants may evaluate data classification, access permissions, retention practices, encryption, and secure disposal procedures. These activities help organizations establish appropriate safeguards and reduce the risk of unauthorized disclosure, accidental loss, or improper handling of confidential information.
Although cybersecurity compliance and security management are related, meeting compliance requirements does not automatically guarantee complete protection. Organizations must consider threats that may extend beyond minimum regulatory obligations. Cybersecurity consultants help businesses connect compliance activities with broader risk management strategies, ensuring that security decisions reflect both legal responsibilities and operational realities.
Incident Response and Cybersecurity Recovery Consulting
Incident response consulting helps organizations prepare for, manage, and recover from cybersecurity incidents. Consultants develop procedures that explain how security teams should identify suspicious activity, investigate potential breaches, and coordinate appropriate responses. A clear incident response plan can reduce confusion and support faster decision-making when unexpected security problems occur.
During an incident, authorized consultants may assist with investigation, containment, evidence preservation, and recovery coordination. Their responsibilities depend on the incident’s severity, contractual arrangements, and available internal resources. Organizations may also involve legal advisers, insurers, or forensic specialists when circumstances require additional expertise beyond routine technical security support.
Recovery consulting focuses on restoring business operations while addressing weaknesses that contributed to the incident. Consultants may help review recovery plans, strengthen security controls, and identify lessons that can improve future preparedness. Regular testing and updating of incident response procedures can make organizations better prepared to manage disruptions and protect essential services.
How to Choose the Right Cybersecurity Consulting Company
Choosing a cybersecurity consulting company begins with identifying your organization’s security needs and business priorities. Some firms specialize in cloud security, while others focus on compliance, penetration testing, or comprehensive risk management. Understanding your requirements helps narrow the options and ensures that potential providers offer relevant expertise rather than unnecessary services.
Experience, professional qualifications, and communication practices are important factors when evaluating cybersecurity consultants. Look for providers who can explain their assessment methods, define project deliverables, and describe how recommendations will support your operations. Relevant certifications and proven project experience can provide additional confidence, although credentials alone do not guarantee quality.
Businesses should also review consulting agreements, pricing structures, confidentiality practices, and responsibilities for handling sensitive information. Clear project expectations help prevent misunderstandings about timelines, deliverables, and ongoing support. Selecting a consulting partner that understands your industry and communicates effectively can support a more productive cybersecurity improvement process.
How Much Do Cybersecurity Consulting Services Cost?
Cybersecurity consulting costs vary depending on the project’s complexity, scope, duration, and required expertise. A basic security assessment for a small organization may involve fewer resources than a comprehensive assessment across multiple business locations. Specialized services such as penetration testing, regulatory compliance reviews, and incident response consulting may require additional technical expertise.
Consulting firms commonly use hourly rates, fixed project fees, or ongoing service agreements. A fixed-fee engagement may cover a clearly defined assessment, while recurring advisory services often involve monthly or annual arrangements. Pricing can also depend on infrastructure size, the number of systems assessed, and the depth of reporting required.
Businesses should evaluate consulting proposals based on expected deliverables and the value of addressing identified security risks. The cheapest option may not provide sufficient assessment depth, while an expensive engagement may include services that are unnecessary. Comparing transparent proposals helps organizations select appropriate cybersecurity support within their available budgets.
How to Become a Cybersecurity Consultant
Becoming a cybersecurity consultant generally requires knowledge of computer networks, operating systems, cybersecurity principles, and common digital threats. A foundation in information technology helps aspiring consultants understand how systems operate and where weaknesses may appear. Learning about risk management, access controls, security monitoring, and incident response provides additional preparation for consulting responsibilities.
Practical experience is particularly valuable because consultants must evaluate security challenges in real business environments. Entry-level roles in IT support, network administration, security operations, or governance can help build relevant skills. Professional certifications, authorized practice environments, and structured training programs may also support learning and demonstrate knowledge to potential employers.
Successful cybersecurity consultants need more than technical abilities because their responsibilities involve communicating findings and advising different stakeholders. Strong analytical thinking, report writing, problem-solving, and interpersonal communication are equally important. Building these skills alongside technical experience can prepare professionals for consulting roles across different industries and security specializations.
Cybersecurity Consulting vs. Managed Security Services
Cybersecurity consulting and managed security services both help organizations improve information security, but they serve different purposes. Consulting usually focuses on assessments, strategic guidance, security design, and specific improvement projects. Managed security services generally involve ongoing operational activities such as monitoring security alerts, managing selected controls, and supporting threat detection.
A cybersecurity consultant might evaluate an organization’s security posture and recommend implementing stronger monitoring capabilities. A managed security service provider may then operate monitoring tools and investigate alerts under an ongoing service agreement. Some cybersecurity companies provide both consulting and managed services, allowing organizations to combine strategic advice with continuous security operations.
Choosing between these services depends on whether a business needs expert guidance, ongoing security management, or a combination of both. Consulting helps organizations understand risks and establish improvement plans, while managed services can support daily security responsibilities. Using both approaches may provide broader support when responsibilities, expectations, and reporting procedures are clearly defined.
Conclusion
Cybersecurity consulting helps organizations understand digital risks, identify security weaknesses, and develop practical strategies for protecting important information and systems. Consultants provide expertise across risk assessments, network security, cloud protection, compliance, and incident response. Their recommendations support more informed security decisions and help businesses strengthen their overall cybersecurity practices.
The right cybersecurity consulting services depend on an organization’s technology environment, business objectives, and risk exposure. Small businesses may benefit from foundational assessments, while larger organizations may require specialized guidance across complex infrastructure. Choosing experienced consultants and establishing clear project goals can make cybersecurity improvements more focused and manageable.
As businesses continue relying on digital technologies, cybersecurity consulting remains an important part of responsible risk management. Professional guidance can help organizations improve preparedness, establish stronger security policies, and respond to changing threats. Investing in appropriate cybersecurity expertise supports long-term resilience, customer confidence, and safer business operations.
Frequently Asked Questions (FAQs)
What is cybersecurity consulting in simple terms?
Cybersecurity consulting is a professional service that helps businesses identify digital security risks and improve their protection against cyber threats. Consultants assess systems, recommend security improvements, and support safer technology practices.
What services do cybersecurity consultants provide?
Cybersecurity consultants provide services such as risk assessments, vulnerability management, penetration testing, cloud security reviews, compliance guidance, and incident response planning. Their work helps organizations identify weaknesses and strengthen digital security.
Is cybersecurity consulting a good career?
Cybersecurity consulting can be a rewarding career for people interested in technology, problem-solving, and information security. It offers opportunities to work with different organizations and develop specialized technical and advisory skills.
Do small businesses need cybersecurity consulting?
Small businesses can benefit from cybersecurity consulting because they also face phishing, ransomware, data breaches, and other digital threats. Consultants help identify important risks and recommend affordable, practical security improvements.
What is the difference between cybersecurity and cybersecurity consulting?
Cybersecurity refers to the overall practice of protecting systems, networks, and data against digital threats. Cybersecurity consulting is a specialized service that provides expert assessments, recommendations, and guidance for improving those protections.