What Is Cybersecurity Email?
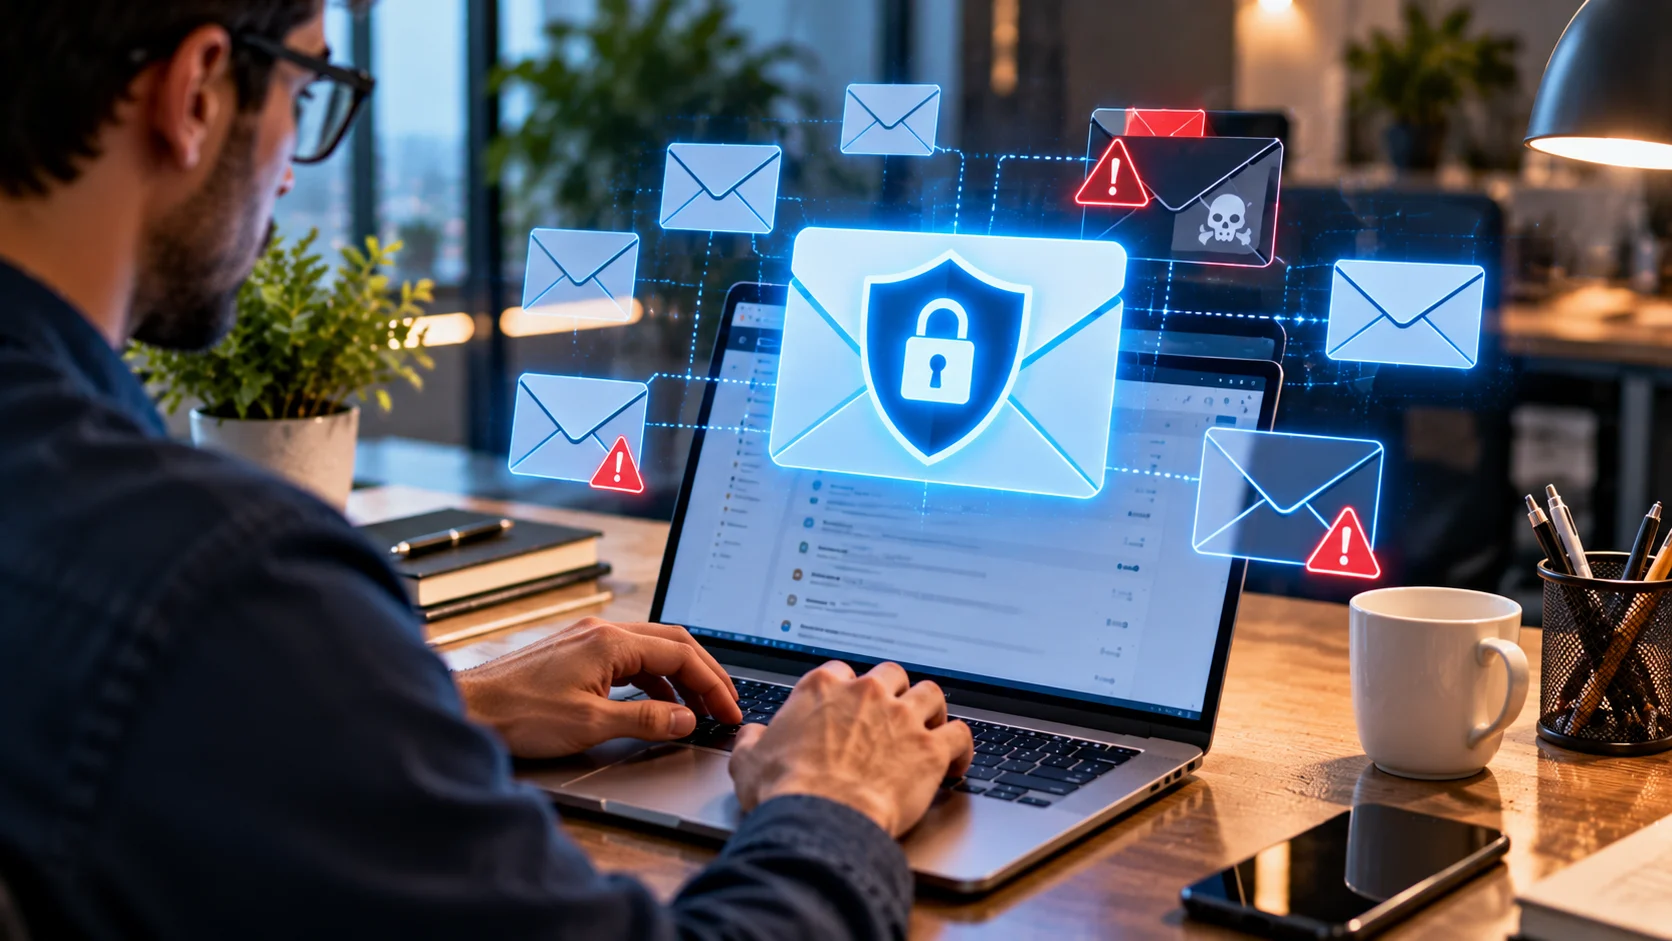
Cybersecurity email, commonly called email security, refers to the technologies, policies, and practices used to protect email accounts and messages from cyber threats. It helps prevent unauthorized access, phishing attacks, malware infections, and sensitive information exposure. Email cybersecurity is important for individuals and businesses because email remains one of the most widely used methods of digital communication.
Email security involves protecting messages throughout their entire lifecycle, including when they are created, transmitted, received, and stored. Organizations use security software, authentication systems, encryption, and employee awareness training to reduce potential risks. These protective measures help ensure that confidential conversations, financial records, customer information, and important business communications remain accessible only to authorized users.
Modern email cybersecurity goes beyond simply blocking unwanted messages or identifying suspicious attachments. It combines several layers of protection to recognize threats, verify senders, and secure account access against unauthorized activity. Understanding how email security works can help businesses establish safer communication practices while reducing the possibility of cyberattacks disrupting their everyday operations.
Why Is Email Cybersecurity Important for Businesses?
Businesses rely on email to communicate with customers, employees, suppliers, and external partners throughout the working day. Important documents, invoices, contracts, and confidential information frequently move through email systems. Without adequate security measures, attackers may attempt to intercept sensitive information, impersonate trusted contacts, or gain unauthorized access to valuable business accounts and digital resources.
A successful email-related cyberattack can create financial losses, operational interruptions, and serious concerns about information privacy. For example, a fraudulent email appearing to come from a trusted supplier might convince an employee to approve an unauthorized payment. Other incidents may involve stolen login credentials, malicious attachments, or the accidental disclosure of confidential customer records.
Strong email cybersecurity helps businesses protect their reputation while maintaining reliable communication with customers and employees. Secure authentication, filtering, monitoring, and staff education reduce the likelihood of common email-based threats succeeding. Although no security system can eliminate every risk, a well-planned approach improves business resilience and helps organizations respond more effectively when suspicious activity occurs.
Common Email Cybersecurity Threats You Should Know
Phishing is one of the most familiar email security threats because it uses deceptive messages to persuade recipients to reveal information or take unsafe actions. Attackers may impersonate legitimate companies, delivery providers, or workplace contacts to make their messages appear trustworthy. These emails sometimes contain misleading links or requests designed to capture passwords and other confidential information.
Malware is another significant threat associated with suspicious email attachments and links. Harmful software may attempt to steal information, disrupt systems, or give unauthorized individuals access to affected devices. Ransomware is a particularly disruptive form of malicious software that can make important files or business systems unavailable, potentially creating serious recovery challenges.
Other common threats include email spoofing, account takeover, spam, and unauthorized sharing of sensitive information. Spoofing involves making messages appear to originate from a different sender, while account takeover occurs when someone gains unauthorized access to a legitimate mailbox. Businesses should also monitor suspicious forwarding activity and unusual login behavior that could indicate compromised email accounts.
How Phishing and Business Email Compromise Attacks Work
Phishing attacks rely on deception rather than directly overcoming every technical security control. Fraudulent messages may claim that an account requires urgent verification or that an important document needs immediate attention. These requests often create pressure to act quickly, encouraging recipients to overlook suspicious details that might otherwise raise concerns about the message’s authenticity.
Business email compromise is a related threat that commonly targets organizations through impersonation or compromised business accounts. An attacker might pretend to be a manager, customer, or supplier and request a payment or sensitive document. Because these messages can resemble normal workplace communication, businesses need reliable verification procedures rather than depending entirely on familiar names.
Modern phishing attempts may also use AI-generated writing to create polished messages with fewer obvious spelling or grammatical mistakes. As a result, unusual wording alone is not a dependable warning sign. Employees should verify unexpected financial requests, examine sender information carefully, and use established communication channels when confirming instructions involving sensitive business activities.
How Does Email Cybersecurity Protection Work?
Email cybersecurity protection typically uses multiple defensive technologies to examine messages and identify suspicious activity. Security systems may evaluate sender information, message content, attached files, and links before allowing emails into a recipient’s inbox. These checks help detect known threats and reduce the chance that harmful messages will reach employees or other users.
Spam filters and secure email gateways provide important protection by separating suspicious messages from legitimate communication. Some advanced security platforms also inspect attachments in isolated environments to determine whether they behave maliciously. However, automated systems can occasionally miss harmful content or incorrectly flag legitimate messages, making regular review and appropriate configuration necessary.
Email security also protects account access and monitors activity after messages have been delivered. Organizations may receive alerts about unusual login attempts, unexpected forwarding rules, or suspicious changes to mailbox settings. Combining automated threat detection with secure account management and employee awareness creates stronger protection than relying on a single security tool.
Email Authentication: Understanding SPF, DKIM, and DMARC
Email authentication helps receiving mail systems evaluate whether messages are authorized to use particular sending domains. Three important technologies are Sender Policy Framework, DomainKeys Identified Mail, and Domain-based Message Authentication, Reporting and Conformance. Commonly known as SPF, DKIM, and DMARC, these mechanisms work together to reduce certain forms of email impersonation and improve domain security.
SPF allows domain owners to identify which mail servers are authorized to send messages on their behalf. DKIM uses cryptographic signatures that receiving systems can verify to check message integrity and signing-domain authorization. These technologies provide different types of evidence about an email’s origin, helping receiving services identify messages that may not come from legitimate sending infrastructure.
DMARC builds on SPF and DKIM by checking domain alignment and allowing domain owners to publish policies for handling authentication failures. It also supports reporting that helps administrators monitor messages using their domains. Proper configuration reduces direct domain spoofing, although authentication alone cannot guarantee that a message is harmless or prevent every phishing technique.
Email Encryption and Protection of Sensitive Information
Email encryption helps protect information from unauthorized reading during transmission or storage, depending on the technology being used. Transport Layer Security, commonly called TLS, can secure connections between email servers and other communication endpoints. This protection reduces the possibility of information being intercepted while moving across appropriately encrypted network connections.
End-to-end email encryption provides a different level of protection by encrypting message content so that only intended participants with appropriate keys can read it. Technologies such as S/MIME and OpenPGP support this type of protection when correctly implemented. However, ordinary TLS-protected email does not automatically provide end-to-end confidentiality throughout the entire communication process.
Businesses handling financial records, confidential contracts, or sensitive personal information should consider whether additional message protection is necessary. Secure document-sharing platforms and encrypted messaging options may be suitable for particular communication requirements. Organizations should also manage access permissions carefully, because encryption cannot prevent information exposure when an authorized account has already been compromised.
Protecting Email Accounts With Strong Authentication
Email account security begins with preventing unauthorized individuals from accessing legitimate user accounts. Strong, unique passwords help reduce the risks associated with password reuse and credential theft. Using a reputable password manager can make it easier to maintain different credentials for business applications without relying on simple or predictable password combinations.
Multifactor authentication adds another layer of protection by requiring additional verification during account access. This may involve an authenticator application, security key, or another supported authentication method. Phishing-resistant methods, such as properly configured passkeys or hardware security keys, can provide stronger protection against certain credential theft attacks than traditional passwords alone.
Organizations should also review email account permissions and remove access that employees no longer require. Former employee accounts, unnecessary administrative privileges, and outdated application connections can introduce avoidable security risks. Regular access reviews and account monitoring help businesses maintain better control over sensitive communication systems while limiting the potential impact of compromised credentials.
Best Email Cybersecurity Practices for Employees
Employees play an important role in protecting organizational email accounts because they regularly interact with messages from different people and services. Awareness training should explain how to recognize suspicious requests, unexpected attachments, and messages that create unnecessary urgency. Staff members should also understand how to report potential threats without feeling pressured to investigate suspicious content themselves.
Before responding to unusual financial or confidential information requests, employees should verify the sender through an independently established communication channel. A message appearing to come from a familiar person does not automatically confirm its authenticity. Checking unexpected instructions with a trusted contact can help prevent payment fraud and accidental disclosure of sensitive business information.
Employees should also avoid sharing passwords, downloading unverified attachments, or using unknown sign-in pages reached through suspicious messages. Keeping devices updated and following approved company security procedures further reduces common risks. Regular refresher training and clear reporting instructions help establish practical email safety habits that remain useful as cyber threats evolve.
How Businesses Can Build an Effective Email Security Strategy
An effective business email security strategy starts with understanding existing communication systems and the information they handle. Organizations should identify critical email accounts, sensitive records, authorized users, and common communication risks. This assessment helps managers prioritize suitable protective measures instead of purchasing expensive security products without understanding their actual business requirements.
Important controls include multifactor authentication, secure email filtering, domain authentication, software updates, and reliable account monitoring. Businesses should configure SPF, DKIM, and DMARC correctly while reviewing how legitimate email services send messages on their behalf. Data loss prevention features may also help identify inappropriate sharing of sensitive information when configured to match organizational needs.
A strong strategy also includes employee training, incident response procedures, and regular security reviews. Smaller businesses can begin with the security features already available through reputable email providers before considering specialized protection services. As the organization grows, security responsibilities and monitoring requirements can expand to address more complex communication systems and operational risks.
What to Do When an Email Account Is Compromised
A potentially compromised email account requires prompt attention because unauthorized access may expose confidential messages and connected services. Warning signs can include unfamiliar login alerts, unexpected password changes, or messages sent without the account owner’s knowledge. If these symptoms appear, users should contact their organization’s security administrator or follow the email provider’s official account recovery procedures.
Where access remains available, changing the account password through a trusted device and reviewing active sessions may help regain control. Users should also examine recovery details, connected applications, and mailbox forwarding settings for unauthorized changes. If financial information or sensitive business records may have been exposed, the organization should follow its established incident response and reporting procedures.
After resolving the immediate issue, businesses should investigate the cause and review whether additional systems were affected. Security teams may need to preserve relevant logs, notify appropriate stakeholders, and strengthen access controls to prevent similar incidents. Clear communication and documented recovery steps help reduce confusion while supporting safer email operations after a security event.
Conclusion
Email cybersecurity is an essential part of protecting digital communication for individuals, employees, and businesses. It helps defend against phishing, malware, account compromise, and unauthorized information exposure through multiple security layers. Technologies such as SPF, DKIM, DMARC, encryption, and email filtering contribute to safer communication when configured and maintained appropriately.
However, technology alone cannot prevent every email-related security incident. Employees need practical awareness training, reliable verification procedures, and clear instructions for reporting suspicious activity. Businesses should combine these everyday practices with strong authentication, secure account management, and regular monitoring to reduce risks across their communication systems.
As cyber threats continue to develop, maintaining effective email security requires ongoing attention rather than a one-time setup. Organizations should review their protections, address new vulnerabilities, and update employee guidance when necessary. By making email cybersecurity part of normal business operations, companies can better protect sensitive information and maintain confidence in their digital communication.
Frequently Asked Questions
What is email cybersecurity in simple terms?
Email cybersecurity means protecting email accounts and messages from online threats such as phishing, malware, and unauthorized access. It involves security software, encryption, account authentication, and safe communication practices.
Why is email security important for businesses?
Email security helps businesses protect confidential information, financial records, and customer communications. It also reduces the risks of account compromise, fraudulent payment requests, and operational disruption caused by email-based cyberattacks.
What are SPF, DKIM, and DMARC in email security?
SPF, DKIM, and DMARC are email authentication technologies that help receiving systems evaluate sender authorization and domain legitimacy. Together, they reduce certain types of email spoofing and improve domain protection.
How can I protect my email account from hackers?
Use a strong, unique password and enable multifactor authentication, preferably a phishing-resistant option when available. Avoid suspicious links, keep your devices updated, and review unusual account activity regularly.
What is the difference between email security and email encryption?
Email security includes all protective measures used to secure email communication, including authentication, filtering, and account protection. Email encryption specifically protects message information from unauthorized reading under defined security conditions.