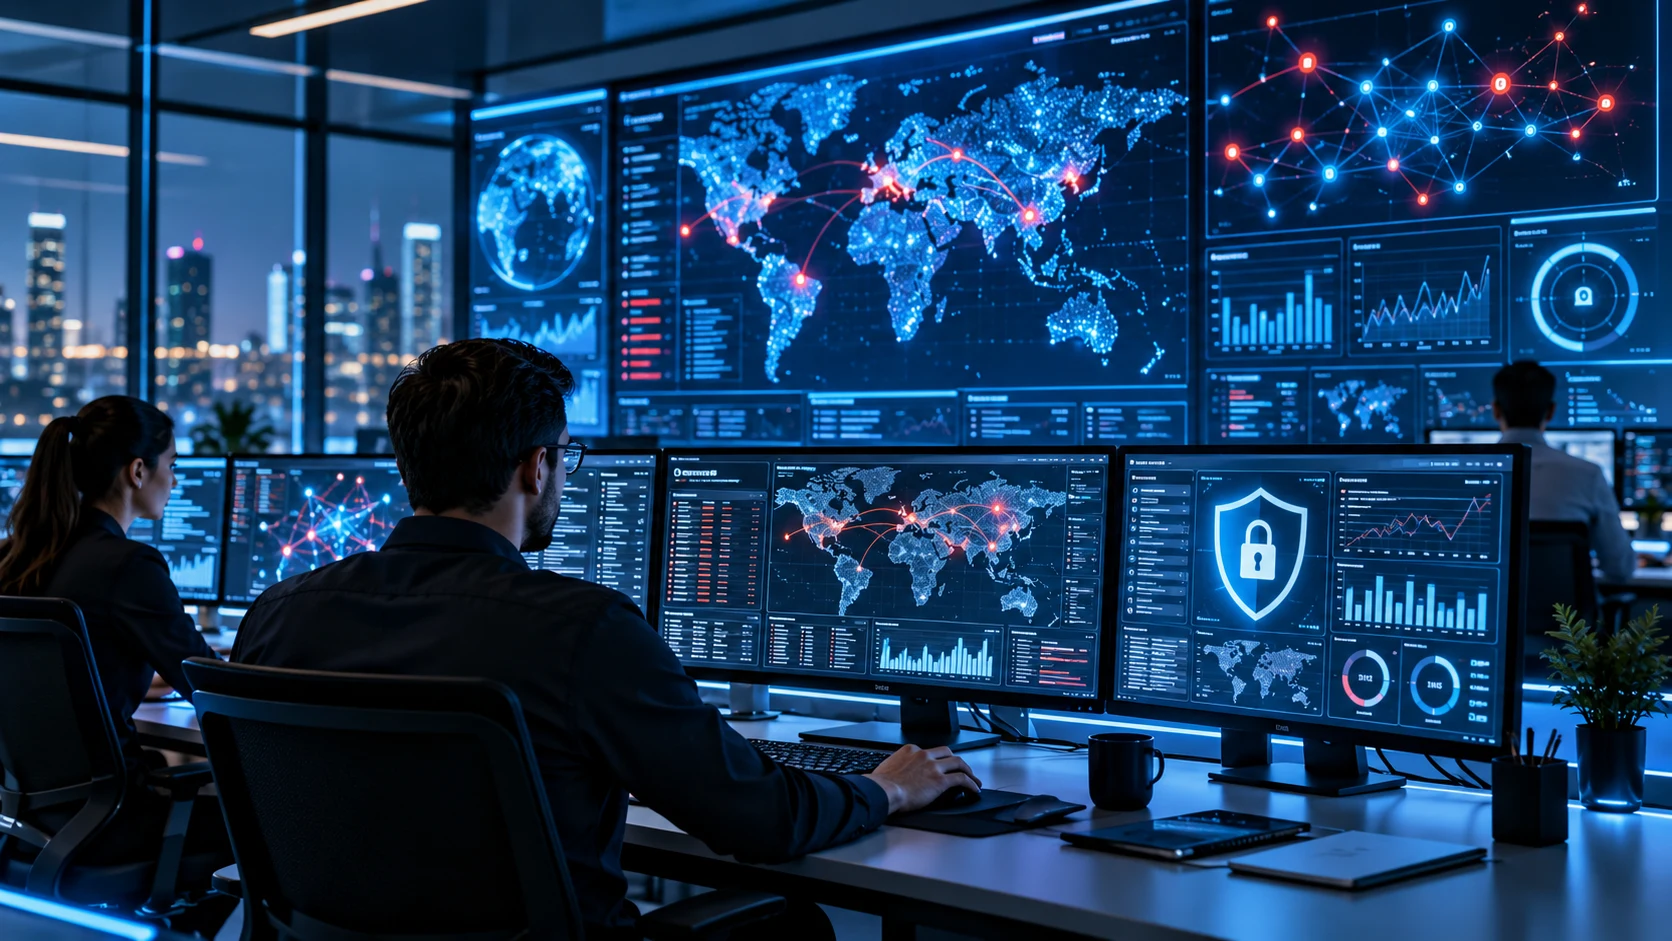
Cybersecurity threats are becoming more complex as businesses depend on digital systems, cloud platforms, and connected technologies. Traditional security measures alone may not provide enough visibility into suspicious activities across modern networks. Cybersecurity analytics helps organizations understand security-related data, identify potential threats, and respond to unusual behavior before problems become more serious.
By analyzing information from networks, applications, devices, and user activities, security teams can identify patterns that might indicate cyber threats. This data-driven approach improves threat detection, supports incident investigation, and helps organizations make better security decisions. Understanding cybersecurity analytics is important for businesses seeking stronger protection against digital risks.
What Is Cybersecurity Analytics?
Cybersecurity analytics is the process of collecting, examining, and interpreting security-related data to identify threats, vulnerabilities, and unusual activities within digital environments. It combines data analysis techniques with cybersecurity practices to improve threat detection and incident response. Organizations use cybersecurity analytics to understand what is happening across their networks and systems. This information helps security professionals recognize potential problems and make informed protection decisions.
Unlike security approaches that rely entirely on predefined threat signatures, cybersecurity analytics can examine patterns across large volumes of information. It analyzes network traffic, authentication records, application logs, and endpoint activities to identify suspicious behavior. Security teams can use these findings to investigate unusual events and prioritize potential threats. However, unusual activity does not always indicate an actual security incident.
Cybersecurity analytics plays an important role in modern security operations because digital environments generate enormous amounts of information. Manually reviewing every security event would be difficult and time-consuming for most organizations. Analytics platforms organize relevant data and highlight activities that deserve further investigation. This process helps security teams work more efficiently while maintaining visibility into potential cyber risks.
How Does Cybersecurity Analytics Work?
Cybersecurity analytics begins with collecting information from systems that generate security-related events. These sources may include firewalls, servers, computers, cloud applications, and network monitoring tools. The collected information often contains details about login attempts, file activities, system changes, and communication patterns. Security platforms bring these records together so analysts can examine activity across different parts of an organization’s infrastructure.
After collecting the information, analytics systems process and organize it into a format suitable for examination. This preparation may involve removing duplicate records, standardizing timestamps, and connecting events from different sources. Analytical rules and statistical methods help identify patterns that appear unusual or potentially dangerous. Some platforms also use machine learning to recognize behavioral differences that deserve further attention.
When suspicious activities are detected, cybersecurity analytics tools can generate alerts for security professionals. Analysts investigate these alerts to determine whether they represent genuine threats or harmless operational events. Depending on the organization’s security procedures, certain actions may be automated while others require human approval. Continuous monitoring and feedback help improve detection accuracy and support faster security responses.
Why Is Cybersecurity Analytics Important?
Cybersecurity analytics is important because modern organizations face security risks across increasingly complex digital environments. Employees access business systems through office networks, personal devices, remote connections, and cloud applications. Each environment generates information that can reveal potential security problems. Analyzing this data helps organizations maintain visibility across systems that might otherwise be difficult to monitor consistently.
Another important reason businesses use cybersecurity analytics is the need to recognize threats before they cause extensive disruption. Suspicious login activity, unusual data transfers, and unexpected system behavior may indicate security concerns. Analytics platforms connect related events and help analysts investigate them more effectively. Early recognition can reduce investigation delays, although no system can guarantee that every cyberattack will be detected.
Cybersecurity analytics also supports better security planning by showing where recurring problems occur. Organizations can examine incident trends, authentication failures, and operational weaknesses to identify areas requiring improvement. Security managers can use this information to prioritize resources and evaluate existing protections. A data-driven security strategy helps businesses make more informed decisions instead of relying entirely on assumptions.
Key Components of Cybersecurity Analytics
Data collection is a fundamental component of cybersecurity analytics because meaningful analysis depends on reliable information. Organizations gather security logs, network activity records, endpoint events, and identity management information. These sources provide different perspectives on what is happening throughout an IT environment. Combining relevant data helps analysts understand events that might appear harmless when examined individually.
Threat detection and event correlation are additional components that help connect security information. Correlation techniques identify relationships between activities occurring across multiple systems or time periods. For example, repeated authentication failures followed by unusual account behavior may require closer examination. Detection rules and behavioral analysis help security teams prioritize events that could indicate suspicious activities.
Visualization and reporting make cybersecurity analytics easier to understand and apply. Dashboards present important information about security alerts, system activity, and ongoing investigations. Reports help managers review trends, assess operational performance, and identify possible weaknesses in security controls. These capabilities support communication between technical specialists and business leaders who need to understand organizational security risks.
Types of Cybersecurity Analytics
Descriptive analytics examines historical security information to explain what has already happened. Organizations use it to review previous incidents, summarize alert activity, and identify recurring security patterns. Dashboards and historical reports help analysts understand how digital environments have behaved over time. This information provides context for evaluating existing security measures and recognizing operational changes.
Diagnostic analytics focuses on understanding why a particular security event occurred. Analysts examine related logs, system activities, and contextual information to investigate suspicious behavior. Predictive analytics takes a different approach by using historical patterns and analytical models to estimate possible future risks. These predictions can support preparation, but they cannot reliably forecast every attack or identify every emerging threat.
Prescriptive analytics helps organizations evaluate possible responses to identified security concerns. It may recommend actions based on established procedures, risk information, and previous incident outcomes. For example, a system might suggest additional verification when unusual account activity is detected. Human oversight remains important because security decisions can affect legitimate users, business operations, and sensitive information.
Common Cybersecurity Analytics Techniques
Behavioral analytics examines how users, devices, and systems normally operate within an organization. It develops an understanding of typical activities, such as login patterns, application access, and data usage. When significant deviations occur, the system can highlight them for further investigation. This technique is useful because some suspicious activities may not match previously identified attack patterns.
Statistical analysis and anomaly detection are also commonly used to identify unusual security events. Analytical models compare observed activities with expected patterns or established thresholds. For example, an unexpected increase in authentication failures or network activity might generate an alert. Security teams must evaluate these findings carefully because legitimate business changes can also produce unusual patterns.
Machine learning can help cybersecurity analytics platforms identify complex relationships within large datasets. Depending on their design, models may classify security events, recognize unusual behavior, or assist with alert prioritization. Threat intelligence can provide additional context about known cyber risks and suspicious indicators. Combining multiple techniques often produces more useful findings than depending on a single detection method.
Benefits of Cybersecurity Analytics for Businesses
One major benefit of cybersecurity analytics is improved visibility into security-related activities across business systems. Organizations can monitor information from multiple technologies through connected analytical platforms. This broader perspective helps analysts identify unusual events that might otherwise remain unnoticed. Better visibility also supports more efficient investigations by making relevant security information easier to locate and understand.
Cybersecurity analytics can improve incident response by helping security teams prioritize alerts and investigate related activities. Instead of treating every notification as equally important, analysts can examine contextual information and potential risk levels. Automated data processing reduces some repetitive investigation tasks. Faster analysis may help organizations contain security incidents sooner and limit unnecessary operational disruption.
Another benefit is better security planning and resource allocation. Historical incident information can reveal recurring weaknesses, inefficient detection rules, and areas requiring stronger protection. Organizations can use these findings to improve security policies and evaluate technology investments. Although cybersecurity analytics requires resources and ongoing maintenance, effective implementation can strengthen overall security management and operational resilience.
Cybersecurity Analytics Tools and Technologies
Security Information and Event Management platforms, commonly known as SIEM solutions, are central to many cybersecurity analytics programs. SIEM tools collect and analyze security events from different systems to support centralized monitoring. Examples include Microsoft Sentinel, Splunk Enterprise Security, and IBM QRadar SIEM. Their capabilities vary, so businesses should evaluate deployment requirements, integrations, and operational needs before selecting a platform.
Extended Detection and Response technologies, often called XDR, provide another approach to analyzing security information. These platforms combine signals from supported security technologies to assist with detecting and investigating threats. Endpoint Detection and Response tools focus specifically on monitoring and protecting devices such as computers and servers. Both categories can contribute useful information to a broader cybersecurity analytics strategy.
User and Entity Behavior Analytics, or UEBA, focuses on identifying unusual activities associated with accounts, devices, and other monitored entities. Security orchestration platforms can also support investigation workflows and automate approved response procedures. The appropriate combination depends on organizational size, available expertise, and technical infrastructure. Businesses should prioritize reliable integrations and manageable alert volumes rather than choosing tools solely by feature count.
Real-World Applications of Cybersecurity Analytics
Cybersecurity analytics is commonly used to monitor identity and account-related security events. Organizations can analyze login attempts, account activity, and access patterns to identify potentially unauthorized behavior. For example, repeated failed logins followed by access from an unfamiliar environment may require investigation. Security teams can examine the surrounding context before deciding whether protective action is necessary.
Network security monitoring is another important application of cybersecurity analytics. Businesses analyze traffic patterns and system communication records to identify unusual connections or unexpected changes in activity. Analytics platforms can help security professionals investigate events that differ from normal network behavior. This is particularly useful for organizations operating complex networks with numerous connected systems and applications.
Cybersecurity analytics also supports cloud security, incident investigations, and security compliance activities. Cloud environments generate activity records that help organizations monitor account usage, configuration changes, and access events. During investigations, analysts can use historical data to reconstruct relevant timelines and understand the scope of incidents. Well-maintained records may also support audits and demonstrate how organizations monitor certain security controls.
Challenges and Limitations of Cybersecurity Analytics
One challenge of cybersecurity analytics is managing the large volume of information generated by modern digital systems. Organizations may collect millions of security events across networks, devices, and cloud services. Processing this information requires suitable infrastructure, data management practices, and analytical tools. Poorly organized or incomplete data can reduce detection accuracy and make investigations more difficult.
False positives create another challenge because harmless activities sometimes resemble suspicious behavior. Excessive alerts can overwhelm security teams and make genuinely important incidents harder to identify. Organizations must regularly review detection rules, adjust analytical thresholds, and examine alert quality. Finding the right balance between sensitivity and accuracy requires ongoing testing and an understanding of normal business operations.
Cybersecurity analytics also raises concerns about data privacy, system integration, and technical expertise. Monitoring user activity requires appropriate access controls, retention practices, and compliance with applicable privacy requirements. Integrating information from different technologies may involve technical difficulties or inconsistent data formats. Skilled security professionals remain essential for interpreting results and making responsible decisions about potential threats.
Best Practices for Implementing Cybersecurity Analytics
Businesses should begin cybersecurity analytics implementation by identifying their most important systems and security objectives. Clear goals might include monitoring privileged accounts, improving incident investigations, or detecting unusual network activities. Organizations should determine which data sources are necessary to support those goals. This approach helps prevent unnecessary information collection and keeps the initial implementation manageable.
Data quality and analytical accuracy should remain priorities throughout implementation. Security teams need reliable timestamps, consistent event formats, and appropriate access permissions to support effective investigations. Detection rules should be tested against realistic scenarios before being widely deployed. Regular reviews help organizations identify missing information, reduce unnecessary alerts, and improve monitoring performance as business operations change.
Successful cybersecurity analytics also depends on employee training and established incident response procedures. Analysts should understand how to investigate alerts, document findings, and escalate serious concerns. Organizations should define responsibilities for maintaining detection systems and reviewing analytical performance. By combining appropriate technology with clear procedures and continuous improvement, businesses can build more effective security monitoring programs.
Conclusion
Cybersecurity analytics helps organizations understand security-related information and identify suspicious activities across digital systems. By collecting and analyzing data from networks, applications, and devices, businesses can improve threat detection and incident investigations. Techniques such as behavioral analysis, event correlation, and machine learning provide additional visibility into potential security risks. These capabilities support a more informed approach to protecting business information.
Implementing cybersecurity analytics requires reliable data sources, suitable analytical tools, and experienced security professionals. Organizations should establish clear monitoring goals, evaluate alert quality, and maintain appropriate privacy protections. Regular testing and continuous improvement help ensure analytical systems remain useful as technologies and business requirements change. Human oversight is essential for interpreting findings and making responsible security decisions.
As digital environments become more interconnected, cybersecurity analytics will continue to play an important role in security operations. Businesses that invest in effective monitoring can improve their understanding of threats and strengthen incident response capabilities. However, analytics works best alongside preventive security controls, employee awareness, and established security policies. Together, these practices help organizations develop a more resilient cybersecurity strategy.
Frequently Asked Questions
What is cybersecurity analytics in simple terms?
Cybersecurity analytics means examining security-related information to identify unusual activities and potential cyber threats. It helps organizations understand what is happening across their systems and supports better security decisions.
What is the main purpose of cybersecurity analytics?
The main purpose is to improve threat detection, support security investigations, and identify potential risks. It helps security teams analyze large amounts of information and prioritize activities requiring attention.
What is the difference between cybersecurity analytics and SIEM?
Cybersecurity analytics is the broader practice of examining security data to identify threats and patterns. SIEM is a technology category that supports this process by collecting, correlating, and monitoring security events.
Does cybersecurity analytics use artificial intelligence?
Yes, some cybersecurity analytics platforms use artificial intelligence and machine learning to recognize patterns, classify events, and identify unusual behavior. However, effective analysis also relies on established rules and human expertise.
Is cybersecurity analytics important for small businesses?
Yes, small businesses can benefit from monitoring account activity, security alerts, and unusual system behavior. The appropriate approach depends on business size, available resources, technical infrastructure, and security requirements.